Advanced Threat Prevention Discussions
Welcome to the Advanced Threat Prevention discussion area. Here, we explore Precision AI-powered protection that stops zero-day malware, exploits, and command-and-control attacks in real time—ensuring proactive defense and resilience against today’s most sophisticated threats.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Advanced Threat Prevention Discussions
Welcome to the Advanced Threat Prevention discussion area. Here, we explore Precision AI-powered protection that stops zero-day malware, exploits, and command-and-control attacks in real time—ensuring proactive defense and resilience against today’s most sophisticated threats.
About Advanced Threat Prevention Discussions
Welcome to the Advanced Threat Prevention discussion area. Here, we explore Precision AI-powered protection that stops zero-day malware, exploits, and command-and-control attacks in real time—ensuring proactive defense and resilience against today’s most sophisticated threats.

Discussions

Welcome to the Threat & Vulnerability Discussions!

To make this forum valuable and enjoyable for everyone, please review the following guidelines before participating: Rules and Best Practices Be Respectful: Treat fellow community members with professionalism and courtesy. Constructive discussions are encouraged; disrespectful or inflammatory comments are not. Stay On-Topic: This board is d...
JayGolf by • Community Team Member
  • 4412 Views
  • 0 replies
  • 0 Likes

Resolved! CVE-2004-0230—GUESSING TCP SEQUENCE NUMBERS AND INJECTING RST PACKETS not in threat DB

Hi All, CVE-2004-0230 does not seem to show up in the Palo Alto Networks threat database, but the below KB article seems to indicate that PAN have introduced threat mitigation for this CVE in PAN-OS 6.0. https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000CllyCAC I am wondering if this is an error in the PA threat database?...

Ben-Price by • L4 Transporter
  • 5905 Views
  • 3 replies
  • 0 Likes

Cool PDF Reader PDF Stream Handling Buffer Overflow Vulnerability - CVE-2012-4914

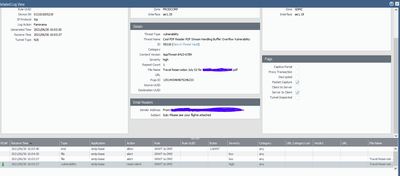
Today we are getting bombarded with reports of email issues. Digging into the reports we have a lot of users who aren't able to send PDF's and the culprit is that the attachments are getting flagged by PAN. The related CVE shows it was updated yesterday. I'm struggling to find much information about the CVE. I feel like given the volume of repor...

evievarga_0-1625076925319.png
evievarga_1-1625077009946.png

Mitigation recommendation for certain vulnerability assesment done by VAPT team

Hi Team, Current PAN OS -8.1.10Customer had run a VAPT assesment where they came up with certain Vulnerability such as90317 - SSH Weak Algorithms Supported 70658 - SSH Server CBC Mode Ciphers Enabled 71049 - SSH Weak MAC Algorithms Enabled While checking certain things are not there from the firewall end but while checking using their Vulnerabil...

CVE-2021-31166 vulnerability - any possible solutions from Palo to block this?

CVE-2021-31166 vulnerability - any possible solutions from Palo to block this? Or create a custom signature.info I came across, but not sure if this is something Palo is planning on adding to their threat vuln protection signatures. See Microsoft has a patch, KB5003173, but what about until machines can be patched?https://www.tenable.com/blog/mi...

tshooter by • L2 Linker
  • 6441 Views
  • 5 replies
  • 0 Likes

TCP timestamp response on MGMNT IP

In my case, the team is performing a vulnerability assessment on PA820Vulnerability Title: TCP timestamp response.Description: The remote host responded with a TCP timestamp. The TCP timestamp response can be used to approximate the remote host's uptime, potentially aiding in further attacks. Additionally, some operating systems can be fingerpri...

Codecov Breach

A conversation I have been hearing crop up is whether or not customers should be worried about Palo Alto being a Codecov customer and if that means that they are affected as well? Are only direct clients of Codecov affected?

PMcelroy by • L0 Member
  • 2285 Views
  • 0 replies
  • 0 Likes

Resolved! Base url category is different from sub url category the traffic was under allow need to know why it was not blocked

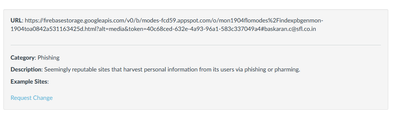
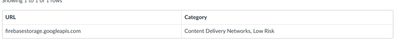
Hi Team, Below screenshot states that the base url firebasestorage.googleapis.com comes under content delivery network and the sub Url comes under phishing where customer wants to know why they were not blocking by the firewall.Also while im checking with the Virsutotal the below urls have been mentioned as phishing. I just wanted to know how to...

Vijaygvasan_1-1619514107687.png
Vijaygvasan_0-1619514053553.png

Host sweep alert from an iPad

We have an iPad that is triggering our scan block policy as a host sweep. The iPad is attempting to connect to one external (Internet) IP over port 443. It's happened for the past few days to a different external IP each time. Threat vault info.Name: SCAN: Host SweepUnique Threat ID: 8002 Has anyone else seen this behavior?What are the threshold...

  • 548 Posts
  • 80 Subscriptions