Advanced Threat Prevention Discussions
Welcome to the Advanced Threat Prevention discussion area. Here, we explore Precision AI-powered protection that stops zero-day malware, exploits, and command-and-control attacks in real time—ensuring proactive defense and resilience against today’s most sophisticated threats.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Advanced Threat Prevention Discussions
Welcome to the Advanced Threat Prevention discussion area. Here, we explore Precision AI-powered protection that stops zero-day malware, exploits, and command-and-control attacks in real time—ensuring proactive defense and resilience against today’s most sophisticated threats.
About Advanced Threat Prevention Discussions
Welcome to the Advanced Threat Prevention discussion area. Here, we explore Precision AI-powered protection that stops zero-day malware, exploits, and command-and-control attacks in real time—ensuring proactive defense and resilience against today’s most sophisticated threats.

Discussions

Welcome to the Threat & Vulnerability Discussions!

To make this forum valuable and enjoyable for everyone, please review the following guidelines before participating: Rules and Best Practices Be Respectful: Treat fellow community members with professionalism and courtesy. Constructive discussions are encouraged; disrespectful or inflammatory comments are not. Stay On-Topic: This board is d...
JayGolf by Community Team Member
  • 4403 Views
  • 0 replies
  • 0 Likes

Virus/Win32.WGeneric.ajtozf / ms-ds-smbv3

We have been seeing alot of detections for smbv3 for file detections varying from pdf to any office document. Wildfire has been picking up the traffic, marking it as Threat and either resetting it or alerting on in. This monthly only we have had about 300+ of the same signature detections. Anyone else seeing it in their environment as well? What...

Syslog to exclude BYOD subnets from logging

Hi all , We do have a few questions on Logging. 1. Can we exclude the BYOD subnet from alerting as they flooding us with irrelevant logs. (both URL and Threat monitoring)2. Can we exclude some category in URL from sending syslog messages. Example here we don't want to send URL log in the category privet-ip-address to the syslog destination. Ov...

Resolved! Microsoft.csharp.dll Virus/Win32.WGeneric.bcycrm - False positive - runtime silverlight Signed by Microsoft

Hi, It's seems that this file signature should be disabled as it is an official and signed binary from Microsoft of the Silverlight Runtime File Hash: fe1f3cde0bacb77a297360b5e022087456b8bf5bLink to Virustotal report for the file: https://www.virustotal.com/gui/file/65064f54e1da6200ff74d32da0f7693f07b6b44f7170b5e1bd35034ec4f1c140/detectionCurren...

rlesavre_0-1618330245906.png
rlesavre by L1 Bithead
  • 4456 Views
  • 1 replies
  • 0 Likes

ssl forward decryption not work with URL category (proxy-avoidance-and-anonymizers )PAN 10.0.5

I upgrade from Pan os 9.1 to 10.0.5 and i foud some issue in any proxy website with URL category (proxy-avoidance-and-anonymizers ) like https://www.proxysite.com/ it bypass any blocked traffic even with ssl decryption policy ,however other category like URL category( translate) like google translate can see block traffic and stop it !!!!!!

Resolved! Automatic IP block-list PAN 8.0

Hello all, I am wondering if there is any way to let's say block the IP address from a source for a set period of time. An example of this could be, we are being attack, same IP address hitting our firewall a 100 times in 3 minutes, It is being reported as "code execution vulnerability." Now the action is dropped, but the IP address could be r...

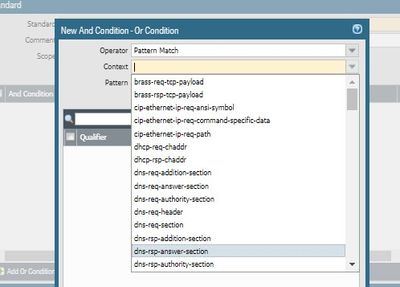
Resolved! custom snort signature add the pattern if the context operator is not found

creating a custom snort signature on Palo alto Firewall but didn’t found the concern context operator for match pattern.Shall we create a context operator or how it can add the pattern if the context operator is not available? For example:alert tcp $HOME_NET any -> $EXTERNAL_NET 443 (msg:"[CIS] Emotet C2 Traffic Using Form Data to Send Passwo...

Snort.jpg

Microsoft Directory Services/ms-ds-smbv3 - /Virus/Win32.WGeneric.badouv

Hello, We are seeing so many alerts in the threat logs that are linked to:Virus/Win32.WGeneric.badouvName: Virus/Win32.WGeneric.badouvUnique Threat ID: 398700357Create Time: 2021-02-03 13:41:24 (UTC)Threat ID: 1103259Current Release: 3615 (2021-02-03 UTC)First Release: 3615 (2021-02-03 UTC) We think it may be a false positive. how can we proceed...

Elhitti by L0 Member
  • 5917 Views
  • 2 replies
  • 3 Likes

SkyVPN - Really a C2 threat?

Hi, I have just spotted a treat alert of SkyVPN C2 traffic (ID 18871) in my logs and looked at the entry on the Threat Vault. This seems to be quite an old detection but when I looked around for any further information regarding SkyVPN, I couldn't see anything referring to it as a known threat; just a cheap domestic VPN. Does anyone have any kn...

djr by L4 Transporter
  • 3517 Views
  • 1 replies
  • 0 Likes
  • 548 Posts
  • 80 Subscriptions