Cortex XDR Discussions
Cortex XDR allows you to rapidly detect and respond to threats across your networks, endpoints, and clouds. It assists SOC analysts by allowing them to view ALL the alerts from all PANW products in one place, telling the full story of what actually happened in seconds and allows seamless response.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Announcements
Scheduled Maintenance: November 14–15 (starting Nov. 14 at 12:00 AM PST)
LIVEcommunity will temporarily operate in read-only mode as we prepare to welcome Idira!
Public content will remain accessible, but log-ins, posting and community interactions will be paused during this period. Thank you for your patience!
Cortex XDR Discussions
Cortex XDR allows you to rapidly detect and respond to threats across your networks, endpoints, and clouds. It assists SOC analysts by allowing them to view ALL the alerts from all PANW products in one place, telling the full story of what actually happened in seconds and allows seamless response.
About Cortex XDR Discussions

Cortex XDR allows you to rapidly detect and respond to threats across your networks, endpoints, and clouds. It assists SOC analysts by allowing them to view ALL the alerts from all PANW products in one place, telling the full story of what actually happened in seconds and allows seamless response.

Please note: All postings in LIVEcommunity are visible to other users; please keep your network secure by refraining from posting live IP address’s or domain names here. Contact your Customer Success team for network-specific questions.

Discussions

Welcome to the Cortex XDR Discussions!

To make this forum valuable and enjoyable for everyone, please review the following guidelines before participating: Rules and Best Practices Be Respectful: Treat fellow community members with professionalism and courtesy. Constructive discussions are encouraged; disrespectful or inflammatory comments are not. Stay On-Topic: This board is d...
JayGolf by • Community Team Member
  • 4741 Views
  • 1 replies
  • 3 Likes

Visualize Running processes through XQL and send alert?

Hello dear community! is it possible to visualize through XQL a prozess which was not terminated and is still running? In the causality view it is visualized, but I would need it to create a alert. If a special process is still running, get a mail through correlation rule or bioc rule. What do you say? Is that possible? BR Rob

RFeyertag by • L4 Transporter
  • 5876 Views
  • 5 replies
  • 0 Likes

Resolved! Cortex XDR Alerts

Hi, I can't seem to find what I'm looking for in the Cortex XDR console. I am trying to find a way to view all alerts generated whether it is from XDR or Analytics. The only way I can see this list is if I create an exclusion Investigation --> Exclusions --> Add Exclusion. Is there a more direct way to view these Alerts? Thanks

Cortex XDR

Hi people, 1) I have installed the cortex XDR on end user PC and when I tried to scan email attachment on the end user PC I am not able to see any option to scan email attachment. I am a system Admin and I want the end user to scan email attachment with cortex. At present I have to download the attachment and do scan with cortex. I don't want to...

lprasad by • L1 Bithead
  • 2949 Views
  • 2 replies
  • 0 Likes

Integrate Cortex XDR with the SIEM (Microsoft Azure) solution

Integration of Cortex XDR with the SIEM (Microsoft Azure) solution Had a few queries regarding it:- 1. Supported integration methods & recommended integration methods for integration with Microsoft Sentinel.2. What all logs can be forwarded (eg: Alerts, Incidents, Audit, management logs and endpoint/server logs, etc.)3. How do we evaluate di...

XDR agent install rolls back

Hi all, Has anyone ever had it where an agent will lose connectivity with the management console and will not reinstall afterwards? I have an endpoint that lost connectivity with the console. Would not check back in. I removed it via the Control Panel and when I went to reinstall it, it looks fine and then towards the end it rolls back the up...

CraigV123 by • L3 Networker
  • 10745 Views
  • 7 replies
  • 0 Likes

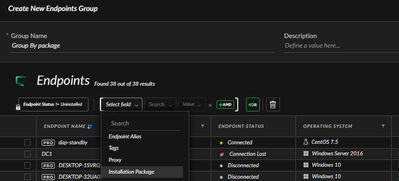
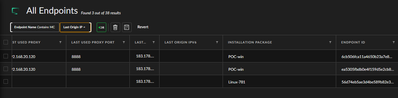
Adding Endpoint to Dynamic Group by "Installation Package" Name

Hi there, Recently I have received a request from client that they would like group endpoint automatically by the installation package, just like their previous deployment of their existing endpoint agents. Since it is much less admin overhead and straight forward for their deployment method e.g. push endpoint installer by department. Firstl...

MervynChan_0-1669257138136.png
MervynChan_1-1669257592492.png
MervynChan_2-1669257621182.png

External Alerts Mapping, Alerts are always assembled to one Incident

Hello, I have a little issue and I don´t know how to solve it. Hopefully someone knows a hidden or 'unofficial' feature of XDR regarding this. Briefly explained the structual background:I am logging from diffrent Forti Firewalls into the XDR, this works perfectly fine. Via the Parsing rules, the Logs are parsed into the External Alerts Mapp...

Resolved! Cortex XDR filter cloud apps for non-sanctioned storage

My goal is to determine which device/user has used Sanctioned and non-Sanctioned cloud storage, e.g., Onedrive, SpiderOak, NextCloud, Syncthing. There is a feature in Microsoft Defender for Cloud Apps that i'm hoping to find in Cortex, which contains a specific list of all Cloud Storage that is used and a list of each device/user that has used t...

  • 2674 Posts
  • 103 Subscriptions
Top Solution Authors



