Cortex XSOAR Discussions
Cortex XSOAR enables SOC analysts to manage alerts across all sources, standardize processes with playbooks, take action on threat intel, and automate response for any security use case.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Cortex XSOAR Discussions
Cortex XSOAR enables SOC analysts to manage alerts across all sources, standardize processes with playbooks, take action on threat intel, and automate response for any security use case.
About Cortex XSOAR Discussions
Cortex XSOAR enables SOC analysts to manage alerts across all sources, standardize processes with playbooks, take action on threat intel, and automate response for any security use case.

Discussions

Resolved! Add a war room filter for the main account tennant.

Hello all, We're trying to edit the layout of an incident in the Main Account tennant in order to display output of splunk searches. When adding the "War Room" section in the layout we're asked to select a war room filter from existing list (see below screenshot). But as we're on the main tennant we can't go to the playground war room and add a...
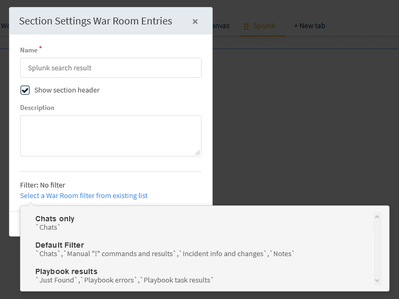
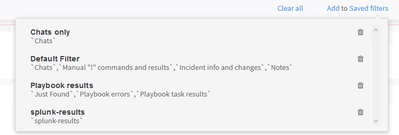
img01.PNG
IMG002.PNG

XSOAR web interface not working with GloabalProtect Clientless VPN

We have Palo Alto Global Protect set up and it works very well with various web applications, however it does not work with the Demisto/XSOAR web interface. It just shows a blank page, although all connectivity is allowed and I see packets flowing. The Demisto is 5.5 and the firewall is running PanOS 8.1.17. Is it possible to be some security f...

batd2 by • L4 Transporter
  • 3126 Views
  • 1 replies
  • 0 Likes

Resolved! XSOAR blacklisting O365 senders

Hello guys, When analyzing a phishing case, I would like to block a sender for all the company. I've read in the Microsoft doc and they say you can do it by creating a blacklist. I've not been able to find it in XSOAR. Is there a way of doing that? Kind Regards.

Demisto-Qradar Integration

Hi, How to filter out the incidents ingestion in to demisto from Qradar based on time.Eg:I have been integrated Demisto with Qradar on today and i want to start recieveing offences only generated from today.We have done some filtering to recieve only active offeneces on integration tab (status="OPEN") but we need to recieve offences which are ge...

  • 1310 Posts
  • 46 Subscriptions
Top Solution Authors



