Advanced Threat Prevention Discussions
Welcome to the Advanced Threat Prevention discussion area. Here, we explore Precision AI-powered protection that stops zero-day malware, exploits, and command-and-control attacks in real time—ensuring proactive defense and resilience against today’s most sophisticated threats.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Advanced Threat Prevention Discussions
Welcome to the Advanced Threat Prevention discussion area. Here, we explore Precision AI-powered protection that stops zero-day malware, exploits, and command-and-control attacks in real time—ensuring proactive defense and resilience against today’s most sophisticated threats.
About Advanced Threat Prevention Discussions
Welcome to the Advanced Threat Prevention discussion area. Here, we explore Precision AI-powered protection that stops zero-day malware, exploits, and command-and-control attacks in real time—ensuring proactive defense and resilience against today’s most sophisticated threats.

Discussions

Welcome to the Threat & Vulnerability Discussions!

To make this forum valuable and enjoyable for everyone, please review the following guidelines before participating: Rules and Best Practices Be Respectful: Treat fellow community members with professionalism and courtesy. Constructive discussions are encouraged; disrespectful or inflammatory comments are not. Stay On-Topic: This board is d...

JayGolf by • Community Team Member
  • 4422 Views
  • 0 replies
  • 0 Likes

Resolved! Spyware with DNS Protection

Hi All,Our Firewall drop DNS traffic of C&C ( us.jaxonsorensen.club, news.sqllitlerver.info & log.osloger.biz) with source IP Address of Firewall. This issue after update the Threat 28/05/2020. Will appreciate any help/suggestions. Best regards,Khai

Resolved! Microsoft Directory Services/ms-ds-smbv3 - Virus/Win32.WGeneric.yurld

We are see numerous alarms from our SIEM from our Palo Alto firewall. Here is a copy of a scrubbed log message below. When asking the user about their activity, they only RDP'ed into various servers from their laptop via the Globalprotect VPN for remote admin work and ran a batch file that re-maps drives. Additionally they noted browsing to \\&l...

Resolved! Microsoft URL being DNS sinkholed suddenly?

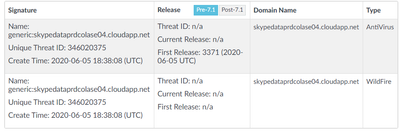
Has anyone else started getting DNS sinkhole threat alerts for the below domain? About half a day ago I started getting a tonne of sinkhole alarms from our PA for this URL. It looks to be a legitimate Microsoft domain and IP. In the PA threat log it comes up as Spyware. skypedataprdcolase04.cloudapp.net The PA threat vault shows the below:Anyone...

BStojceski_0-1591526540792.png

incorrect destination zone in threat logs

Hi, if the firewall is configured with zone protection profiles and the setting "set system setting additional-threat-log on" is configured, i have noticed the destination zone is not correctly (in my example 8.8.8.8 is reachable over the outside zone) displayed in the threat logs: I noticed it with version 8.1.8, 9.0.8, 9.1.2. Does anybody has...

JuergenHolzer_0-1591185185711.png

Resolved! DNS issues after implementing GeoBlock policy.

Hey guys, wanted to see if I can can get any input on this here - had to Geoblock one of the countries for inbound/outbound traffic completely. Everything was fine until I found out that one of the employees started having issues with email delivery to the certain customer - "domain of sender address [email protected] does not resolve customer....

MKarasev by • L0 Member
  • 4650 Views
  • 2 replies
  • 0 Likes

Resolved! Malicious traffic blocked by PAN : Virus/Win32.WGeneric.ajbecg(340897548)

Hi Team,These are the below sign identified in our network and want to know the reason for this trigger.Please provide the related application effected? Why are this signature identified and what the user is trying to access so that PAN blocked the traffic. Any additional information will be appreciated. Virus/Win32.WGeneric.ajbsuc(341044866) V...

Virus/Win32.WGeneric.ajqxax

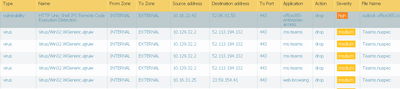
Starting yesterday I have seen virus alerts on my firewall relating to the above virus. The file names in question are Teams.nuspec and Teams-1.3.00.12058-full.nupkg. Googling around it appears the files are legit. File 1.3.00.12058-full.nupkg is the same version of the latest MS Teams update. Last month at this time I had false positive virus a...

How to stop MortiAgent Malware using the snort rule ?

Software Version9.0.5 Problem Description: How to stop MortiAgent Malware using snort rule ? I want to stop the MoriAgent malware by applying /using snort rule & also using yara rule?How to configure this in Palo alto ?Below are snort & Yara Rules:1. The below SNORT rule can be used to detect the MoriAgent Beacon.alert tcp $HOME_NET any...

Minemeld Syslog Miner Not parsing Messages

Hi, I am working with a new installation of Minemeld running on ubuntu 16.04. if I do a TCP dump I can see the Syslog but minemeld is not parsing them. I check the /var/log/Syslog and found this.It seems that some modules are missing and that gives an error. please let me know how can I install the missing Modules or how to fix this.Thanks Apr 2...

mmatos by • L0 Member
  • 3966 Views
  • 1 replies
  • 0 Likes

Tofsee TLS Fingerprint Detection

Hi all,Since the moment we updated our threat database to 8204-5736 we see THOUSANDS of 'Tofsee TLS Fingerprint Detection' threat matches.I assume they are false positives? Anyone else seeing the same?It's skewing our monitoring stats significantly so I may need to create an exception.Thanks.

  • 548 Posts
  • 80 Subscriptions