DNS based traffic shows incomplete when connected to GlobalProtect
Hi all I have an issue noticed that DNS-based traffic shows incomplete when users are connected to GlobalProtect.The same traffic is fine when we disconnect from GlobalProtect
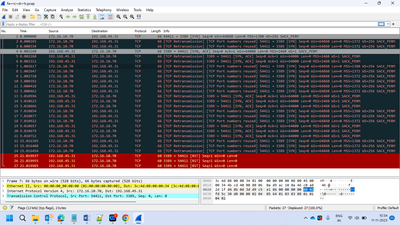
Hi All,We have recently configurated a Global Protect VPN in our environment. As we extended it to more people we started facing few issues:1. Not able to join zoom meetings.2. outlook shows disconnected3. Can not sign-in into skype4. Suddenly internet connectivity drops and have to reboot the machine. We are running global protect on PA- 850 (8...
Hi Friends, We have a customer who is facing issues while accessing RDP via Global Protect. User is not able to access the RDP machine after connecting to RDP. We have tried by adding the RDP ip in the include list. We have also tried by creating a specific policy for ms-rdp. It is hitting the correct rule but unable to access. For the logs we...
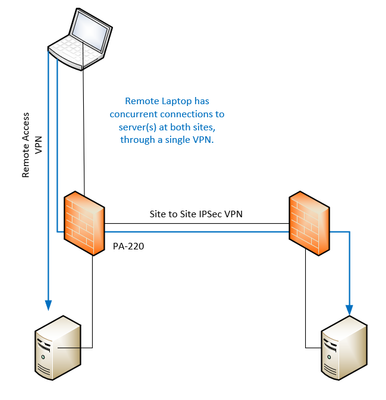
Hello,I am looking at setting up a remote access VPN on a PA220. The idea, however, is that the user would have concurrent access to a server at the PA220's site as well as servers at another site, that the PA220 has a IPSEC VPN with. Here is a diagram: In case this isn't clear.... the WAN interface of the PA220 would service both the remote ac...
Hi - we're all working remotely now - so I've connected GlobalProtect to reach resources on our domain. I was a little confused when I ran a ping scan on a particular subnet and all the devices returned the same MAC address along with the IP address, 02:50:41:00:00:02. I did a bit of research and learned that the GlobalProtect virtual ethernet a...
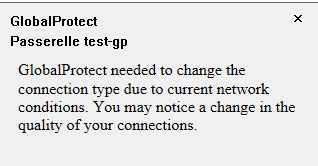
Hello, we are installing a new cluster of vm palo, and we have configure Globalprotect acces. We can connect to the portal, but when we connect, we have this message : Can someone tell us why we have this message ? and what is the impact of this change of connection type ? We use the Globalprotect 6.1.2 version. Thanks
We've run into an issue this morning where users are no longer able to authenticate via our ADFS (SAML) portal.This is the error users see: We opened a support ticket with Palo Alto, and this was the response from support engineer: Hello team, I found the cause of the issue. Looking at the logs I can see the following (I just picked one random ...
Does Global Protect typically use one DHCP pool for multiple profiles? What is best practices?
Having ran a PCI DSS compliance scan it has come back that our Global Protect VPN setup is flagged as a failing vulnerability for Redirection via Arbitrary Host Header Manipulation. We have it setup to redirect to azure to authenticate account details. The solution they have given us to fix the issue is; Implementing proper validation and sa...
Hi! We have problems with a customer that uses GP and pre-logon with machine certificate. It works for a couple of days, GP connects when you start your computer and works as intended. But stops working after a while. I can see these entries in the logs, the application seems to have som problems with the machine certificate: P13676-T145...
We're using Google SAML for our GP 2FA, and the certificate is nearing its expiration date. I'm looking for guidance on how to go about updating the cert. Discover a world of modified WhatsApp experiences with GBGenie. We specialize in providing a curated selection of WhatsApp mods and modded apps, packed with unique features and functionalities...
Hello Everyone, I am setting up a new PA460 and have a decent amount of users I set up. I have all the users set up and gave them new passwords. I was wondering, (on my current device) if I take the Password Hash from the user section in the Firewall's config using Notepad++, couldn't I simply copy the hash and paste that in as a hash for the ...
Two different users reported problems when connecting to GlobalProtect when using an iPhone as a hotspot. The users can connect to GP, but are then unable to use HTTPS or ssh to connect to internal assets via the VPN. If the user uses the same laptop and connects via wifi (not using hotspot), GP works fine. Tests with several other users usin...
Since I upgraded to the lastest fedora, all of my python/ansible script failed when they are decrypted by our palo alto ssl outbound policy. After some diging, fedora 35 was using openssl 1.1.1 and fedora 36 switched to openssl 3.0: https://fedoraproject.org/wiki/Changes/OpenSSL3.0 On the openssl 3.0 changelog, we can find this: OPENSSL chan...
Hello, Current setup is a 440 running 10.1.10-h2. Global Protect version is 6.1.2 I have double and triple checked that it's not a reverse dns issue, following this article: GlobalProtect app fails to detect Internal Network with Interna... - Knowledge Base - Palo Alto Networks global protect tries to connect internally to the vpn it fails wi...
| Subject | Likes |
|---|---|
| 1 Like | |
| 1 Like | |
| 1 Like | |
| 1 Like | |
| 1 Like |