Next-Generation Firewall Discussions
Palo Alto Networks Next-Generation Firewalls provide true, complete visibility everywhere, along with precise policy control. Ask your questions or provide insightful answers in the discussion forum specific to NGFW.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Next-Generation Firewall Discussions
Palo Alto Networks Next-Generation Firewalls provide true, complete visibility everywhere, along with precise policy control. Ask your questions or provide insightful answers in the discussion forum specific to NGFW.
About Next-Generation Firewall Discussions
Palo Alto Networks Next-Generation Firewalls provide true, complete visibility everywhere, along with precise policy control. Ask your questions or provide insightful answers in the discussion forum specific to NGFW.

Discussions

Welcome to the Next-Generation Firewall Discussions!

To make this forum valuable and enjoyable for everyone, please review the following guidelines before participating: Rules and Best Practices Be Respectful: Treat fellow community members with professionalism and courtesy. Constructive discussions are encouraged; disrespectful or inflammatory comments are not. Stay On-Topic: This board is d...
JayGolf by • Community Team Member
  • 4784 Views
  • 0 replies
  • 1 Likes

Should I override the intrazone-default to deny?

TL;DR: yes, almost always. We've had plenty of discussions on the behaviour of this default rule, and published Security Policy Rule Best Practices (paloaltonetworks.com) which provide guidance for logging. We've even discussed the results of these best practices, which often lead to the uninformed creating explicit policy to block what they n...

mb_equate by • L3 Networker
  • 12604 Views
  • 10 replies
  • 0 Likes

Resolved! Dynamic Decryption sources

Hello all, We are slowly rolling out Decryption to folks and was wondering if there is a way to dynamically add users, similar to user-ID. My current way is manually adding computer objects which was fine for the first 15 computers but is starting to get tedious. I know I can import objects using the API but am looking for a more dynamic metho...

MNoble by • L2 Linker
  • 5170 Views
  • 8 replies
  • 0 Likes

Resolved! PA-7050 Firewall Upgrade

Hi All, We are kind of confused on 2 documentations below. We are planning to upgrade PA-7050 Firewall. Our initial Target version is 10.2.8-h3 because document 1 says it is possible. BUT document 2 is saying this specific model is supported up until 10.1.X only. Links are below. Any Insights? Document 1: https://docs.paloaltonetwork...

Multiple ARP requests bringing network segment down

We have a guest network for which our PAN firewall is the default gateway. Periodically we have a wireless client begin ARP'ing for the gateway address over and over again. So much so that we can no longer ping the gateway address (PAN interface). It is always a single client doing this. Is there something I can do on the PAN to protect agai...

svanarts by • L1 Bithead
  • 2126 Views
  • 3 replies
  • 0 Likes

SSL Inspection

Hello I configured my firewall with SSL decryption. Regarding the certificate, what is the best practice ? Is-it to generate the certificate used for Outbound traffic from our internal PKI (with the problem to deploy the certificate on Linux system or application who not use Windows store) or to generate certificate from our public authority ?...

Resolved! Old Content Update Release Notes

Hi! Is there a way to see Release Notes from "old" (a year old) Content Updates (Apps & Threats)? I can't see them on the PANOS Dynamic Updates tab and I wanted to know if there is some database with all the content release notes. Thanks!Panorama

mR00t_s5 by • L2 Linker
  • 2899 Views
  • 2 replies
  • 0 Likes

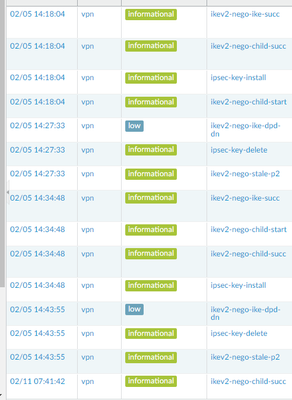
Resolved! Request help with the exact meaning of these IPsec event alerts for Palo Alto.

Hello All, I would like to know what is the meaning of the typical events we observe in the IPsec details in the monitor logs. ikev2-nego-ike-succ ikev2-nego-child-succ ipsec-key-install ikev2-nego-child-start ikev2-nego-ike-dpd-dn ipsec-key-delete ikev2-nego-stale-p2 ikev2-nego-ike-succ ipsec-key-expire

Kandarp_Desai_0-1678092309340.png

Resolved! Cannot ping inside interface from Windows PC with inside interface set as GW

I'm going a little bit crazy. I have a super simple setup, I have a Windows PC @ 10.0.0.10 My PA 440 has 10.0.0.11 as its MGT Interface and all communications between the Windows PC and the management interface work fine. I have an inside interface set as eth 1/8 Layer 3 with an IP of 10.0.0.1 and its assigned to the inside zone. Eth 1/8 is al...

Service/URL category

Microsoft Defender has a lot of endpoints it seems. I started a custom URL list with all the URLs needed for defender, created a policy in a global device template and said "Allow any source, any destination, using SSL, Web-Browsing, and windows defender atp app, using application default. I put the URL list I created in URL category area and di...

  • 1633 Posts
  • 62 Subscriptions
Top Solution Authors