Panorama Discussions
Post discussions about Panorama, a centralized network security management solution for all your Palo Alto Networks firewalls irrespective of their form factors or locations, in this forum.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Announcements
Scheduled Maintenance: November 14–15 (starting Nov. 14 at 12:00 AM PST)
LIVEcommunity will temporarily operate in read-only mode as we prepare to welcome Idira!
Public content will remain accessible, but log-ins, posting and community interactions will be paused during this period. Thank you for your patience!
Panorama Discussions
Post discussions about Panorama, a centralized network security management solution for all your Palo Alto Networks firewalls irrespective of their form factors or locations, in this forum.
About Panorama Discussions
Post discussions about Panorama, a centralized network security management solution for all your Palo Alto Networks firewalls irrespective of their form factors or locations, in this forum.

Discussions

Welcome to the Panorama Discussions!

To make this forum valuable and enjoyable for everyone, please review the following guidelines before participating: Rules and Best Practices Be Respectful: Treat fellow community members with professionalism and courtesy. Constructive discussions are encouraged; disrespectful or inflammatory comments are not. Stay On-Topic: This board is d...
JayGolf by • Community Team Member
  • 5176 Views
  • 0 replies
  • 0 Likes

Resolved! Query on Policy creation

I got a request from my client to create the below policy. The destination address is given as "IS NOT "abcd.xyz.com"". I checked all options to find the 'IS NOT' reference in the policy options but didn't find any. Please let me know if there are any references for the given scenario. Name of the policy: XYZSource Zone: TrustSource: AnyD...

nazddk by • L1 Bithead
  • 1835 Views
  • 1 replies
  • 0 Likes

panorama cannot be access

I have a PAM PA-410 Lab and I try to use Panorama but the FW will not allow me to install the license. I was told that it is because it is a LAB subscription. How can I change my subscription to 3 years to get the feature unlocked. Please help

pgarcia by • L0 Member
  • 1026 Views
  • 1 replies
  • 0 Likes

Resolved! Templates onboarding

Hi I have imported standalone firewalls, just finished with device groups. Now, regard templates, I can see each device has it's own default template and template stack. My question is, how can i "split" this template into seperator types (like interfaces, gateways). I would like to use same template for X devices.

chens by • L3 Networker
  • 2199 Views
  • 2 replies
  • 0 Likes

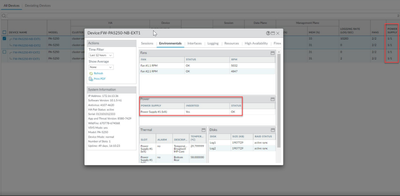
Panorama show power supply only 1 unit

We found an issue about monitoring managed device power supply. We managed PA5250 that have 2 power supply but we see only 1 power supply(left). PANOS -10.1.5-h1 and 10.1.6 found the same issue We want to know if this is normal or not?

power-supply.png

Panorama 11 Upgrades

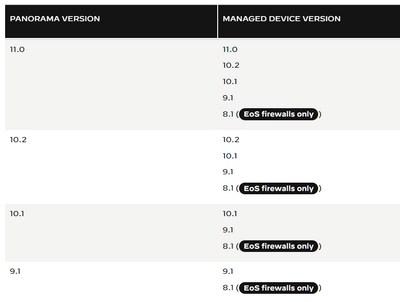
Any one running Panorama at 11.x code with managing the Palos that are running on 8.1.x code? . Currently we are running at 10.1.8-h2 code and we did not upgrade , because , the need for managing firewalls that are still running on 8.1. We came across a sticky situation, where we need to purchase Palo 1410 firewalls , that only runs on Pan-os 11...

MicrosoftTeams-image.png
RaviKola by • L0 Member
  • 1732 Views
  • 1 replies
  • 1 Likes

Resolved! Fans and Power Supply not Displayed on Panorama under Managed Devices - Health

I recently migrated from an M-100 to M-200 and noticed that environmental information (fans and power supply) is not displayed for my managed firewalls. M-200 is on PAN-OS 10.1.5-h2 and managed firewalls are on PAN-OS 9.1.13-h3. Has anyone experienced this? Any help with correcting this is greatly appreciated.

Traffic to panorama

Hello,I had a panorama instance in my cloudYesterday i removed my ha pair from panorama.I have followed all steps, disabled ha sync, disabled the panorama objects, templates and network, checked the box to copy these configuration to my firewalls, delete the panorama IP and etc. But after doing all changes in my firewall and panorama, completely...

Resolved! Email Alert on PAN/PAFW for new admin account Creation

Hi, I am looking to create email alerts for when ANY user creates a new admin account of anytype on both our Panorama and any of our firewalls managed by panorama. Our PAFW send/forward their logs to our M600 Panorama device. Any have any link or suggestions? Purpose being to know if any admin create local or alternate admin accounts, or s...

Resolved! Panorama - Log collector issues

Hi I just deployed a Panorama VM and I added a disk of 2TB. On Managed Collector, I see my Panorama device (VM) on collector name but the status is disconnected / Out of Sync. Currently, I have no firewall connected on the Panorama server. Is-it this status is normal until I connect a firewall to the Panorama or does I make an error on my conf...

jeromecarrier_0-1695723894121.png

How do I assign SD-wan interface profile to template when all sites have different speeds for fiber and cable.

How do I assign a SD-wan interface profile an interface in a template with 3 firewalls assigned to 3 groups based on site when each site has different speeds for each ISP? Do I have to go against palo alto recommendations and use 3 templates? Site 1 Fiber: 250Mbps/250MbpsSite 1 cable: 600Mbps/35Mbps Site 2 Fiber: 200Mbps/200MbpsSite 2 cable: 250...

Resolved! Validation Error: interface 'ethernet1/2' is already in use, but it isn't ... and zones are type unknown, but they aren't

Hi,When I try to push a config from Panorama to a PA-440, the commit fails because of these reasons. Which is strange because ethernet1/2 isn't in use (on the PA-440). Also the zones are configured and their type is defined.What am I missing here ? Thank you very much,

The Panorama IP has been changed on the firewall, but the firewall still has a session to the original IP

Panorama is used for management and log collection. The IP address of Panorama has not changed. There is a firewall outside Panorama, which maps the 3978 port of the firewall's exit IP to Panorama. The managed firewall was originally configured with the private network IP of panorama. Now it is changed to the mapped public network IP. After the ...

Wilbur by • L1 Bithead
  • 5818 Views
  • 4 replies
  • 0 Likes
  • 736 Posts
  • 47 Subscriptions
Top Solution Authors
Top Liked Authors
Labels