Next-Generation Firewall Discussions
Palo Alto Networks Next-Generation Firewalls provide true, complete visibility everywhere, along with precise policy control. Ask your questions or provide insightful answers in the discussion forum specific to NGFW.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Next-Generation Firewall Discussions
Palo Alto Networks Next-Generation Firewalls provide true, complete visibility everywhere, along with precise policy control. Ask your questions or provide insightful answers in the discussion forum specific to NGFW.
About Next-Generation Firewall Discussions
Palo Alto Networks Next-Generation Firewalls provide true, complete visibility everywhere, along with precise policy control. Ask your questions or provide insightful answers in the discussion forum specific to NGFW.

Discussions

Welcome to the Next-Generation Firewall Discussions!

To make this forum valuable and enjoyable for everyone, please review the following guidelines before participating: Rules and Best Practices Be Respectful: Treat fellow community members with professionalism and courtesy. Constructive discussions are encouraged; disrespectful or inflammatory comments are not. Stay On-Topic: This board is d...

JayGolf by • Community Team Member
  • 4791 Views
  • 0 replies
  • 1 Likes

why drop rst packet

The customer is capturing packets on the firewall. Check the files in the receive stage and find that the firewall has dropped the rst message sent by the client in the session. Please refer to the screenshot for the file reference. Can someone tell me why the pa-firewall dropped this rst packet

receive.jpg
drop.jpg
Felixcao by • L3 Networker
  • 4593 Views
  • 7 replies
  • 0 Likes

IP sec tunnel

Hi Team, We have multiple IP-sec tunnels and want to clean up unused tunnels. Like we have the option of an unused rule for security policy, or we will know by its hit count, is there any similar way we can find out an unused tunnel so we can delete it?

TSF file upload

I am trying to open a case in the portal for one of our customers and the page is not working. I have a TSF to upload as I believe our customer has evidence of exploitation of CVE-2024-3400

Microsoft Defender Outbound traffic policy

Trying to slim down a rule for outbound traffic with clients using MS defender. I built a custom URL list of the defender urls provided by MS. Added it to the policy under service/url category. The apps used are ms-update, ssl, web-browser, windows-defender-atp. The issue is I see traffic hitting ssl in the logs with url category as "any" whic...

PBR using Route failover

Hi All, Our organisation purchased two Mpls link and wants to configure an PBR like such 1) All intranet traffic like dns, ntp shoud go via primary MPLS 2) All internet related traffic should go via Secondary MPLS 3) In case Primary MPLS goes down all traffic (intranet and internet) should go via Secondary MPLS and vice versa. Please let m...

Diabled Application in VSYS1

I have received an high risk alert on PA3250 IOS 9.1.16 "Disabled applications in vsys1: 104apci-unnumbered-startdt-act 104apci-unnumbered-startdt-con 104apci-unnumbered-stopdt-act 104apci-unnumbered-stopdt-con 104apci-unnumbered-test-act 104apci-unnumbered-test-con 104asdu-file-transfer-type120 104asdu-file-transfer-type121 104asdu-file-transf...

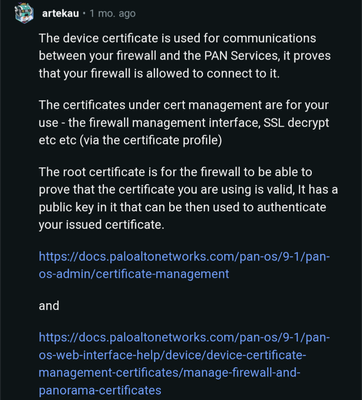
Elaboration on the differences between the PAN-OS root certificate, the device certificate, and the certificate under cert management?

I've been requested to get as much information as I can on this topic, and I've found a good one on Reddit. A piece of info that i found on reddit It's great, but somehow I still need much more elaboration on this. Could anyone provide me a document that elaborates on the differences between the PAN-OS root certificate, the device certificat...

thumbnail_1000001488.png
MFEC by • L0 Member
  • 5668 Views
  • 4 replies
  • 0 Likes

Resolved! Block privileged accounts from accessing the Internet

My company wants to block privileged accounts from accessing the internet on our servers using the Palo Alto firewalls. My first thought was to allow certain apps like ms-update and things of that nature to allow the access then block http and https right under that rule, but I'm not sure that would work. The company actually wants the privile...

Not able to login into URL from behind the palo alto

Dear Team, Greeting...! We are trying to access one URL from behind the palo alto, it was accessible but we are not able to log in to that URL, and when we checked using a mobile hotspot it was login successfully. Additionally, we checked the traffic logs and created a new security rule for the specific source to the destination to allow a...

Resolved! Need clarification on URL Filtering logs

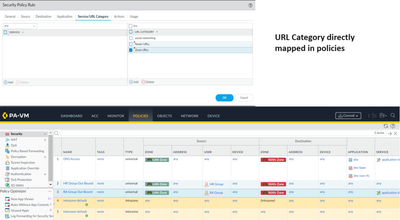
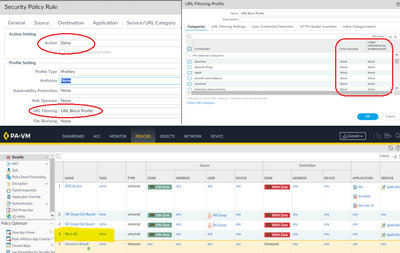
Hi everyone, Please help me get through this. We have configured PA-450 firewall and everything is working fine as expected.But, We have used the option URL category in the security policy without an URL filtering profile for all user group. Which is working fine but I cant see any URL user activity report.But we need block URL summary report. T...

Arun_R_0-1713249886072.png
Arun_R_1-1713250275858.png
Arun_R by • L1 Bithead
  • 2898 Views
  • 3 replies
  • 0 Likes
  • 1633 Posts
  • 62 Subscriptions
Top Solution Authors