Next-Generation Firewall Discussions
Palo Alto Networks Next-Generation Firewalls provide true, complete visibility everywhere, along with precise policy control. Ask your questions or provide insightful answers in the discussion forum specific to NGFW.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Next-Generation Firewall Discussions
Palo Alto Networks Next-Generation Firewalls provide true, complete visibility everywhere, along with precise policy control. Ask your questions or provide insightful answers in the discussion forum specific to NGFW.
About Next-Generation Firewall Discussions
Palo Alto Networks Next-Generation Firewalls provide true, complete visibility everywhere, along with precise policy control. Ask your questions or provide insightful answers in the discussion forum specific to NGFW.

Discussions

Welcome to the Next-Generation Firewall Discussions!

To make this forum valuable and enjoyable for everyone, please review the following guidelines before participating: Rules and Best Practices Be Respectful: Treat fellow community members with professionalism and courtesy. Constructive discussions are encouraged; disrespectful or inflammatory comments are not. Stay On-Topic: This board is d...
JayGolf by • Community Team Member
  • 4808 Views
  • 0 replies
  • 1 Likes

Elaboration on the differences between the PAN-OS root certificate, the device certificate, and the certificate under cert management?

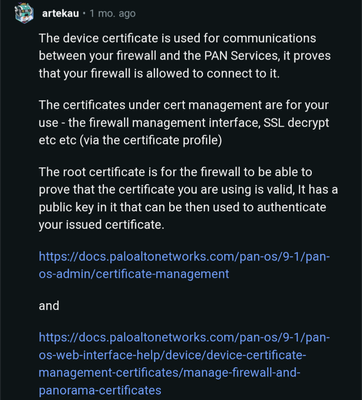
I've been requested to get as much information as I can on this topic, and I've found a good one on Reddit. A piece of info that i found on reddit It's great, but somehow I still need much more elaboration on this. Could anyone provide me a document that elaborates on the differences between the PAN-OS root certificate, the device certificat...

thumbnail_1000001488.png
MFEC by • L0 Member
  • 5691 Views
  • 4 replies
  • 0 Likes

Resolved! Block privileged accounts from accessing the Internet

My company wants to block privileged accounts from accessing the internet on our servers using the Palo Alto firewalls. My first thought was to allow certain apps like ms-update and things of that nature to allow the access then block http and https right under that rule, but I'm not sure that would work. The company actually wants the privile...

Not able to login into URL from behind the palo alto

Dear Team, Greeting...! We are trying to access one URL from behind the palo alto, it was accessible but we are not able to log in to that URL, and when we checked using a mobile hotspot it was login successfully. Additionally, we checked the traffic logs and created a new security rule for the specific source to the destination to allow a...

Resolved! Need clarification on URL Filtering logs

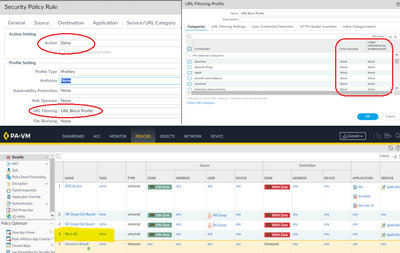
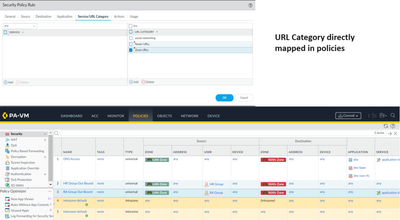
Hi everyone, Please help me get through this. We have configured PA-450 firewall and everything is working fine as expected.But, We have used the option URL category in the security policy without an URL filtering profile for all user group. Which is working fine but I cant see any URL user activity report.But we need block URL summary report. T...

Arun_R_0-1713249886072.png
Arun_R_1-1713250275858.png
Arun_R by • L1 Bithead
  • 2908 Views
  • 3 replies
  • 0 Likes

Layer 2 network extension

Is it possible to extend the layer 2 network over the layer 3 network to the other site using Palo Alto Basically I am trying to extend the VLAN to other site. Not sure if this can be achieved with Palo Alto. Any suggestion are welcome

Resolved! PA-220 shows alarm true for S1 12.0V IN B Power Rail

Hello Team, We have a PA-220 in our environment and we have received an alert which shows alarm is TRUE for 12.0V IN B Power Rail and voltage is 1.57 which is less than the min and max value. This is a standalone firewall. Please advise how can i proceed in this case. Can this impact our production? Below logs are for your reference: &gt...

Running 11.1.2 in production

Hi everyone I read that 11.1.2 is now the preferred release for 34xx, and desiring to upgrade due to some of the new features, I find myself concerned about this known issue: PAN-224763 - A TDB engine version mismatch issue affecting all firewalls, which in turn produces heartbeat failures, can cause the firewall to crash when installing conte...

SomeSuch by • L1 Bithead
  • 2571 Views
  • 2 replies
  • 0 Likes

Firewalls communicating to public IPs on Management Interface

We are currently seeing the Management Plane of our Palo Alto Firewalls communicating to the following IP-Addresses: 34.96.84.34 107.178.249.217 35.238.108.32 This communication occurs on different Platforms. We see more activity since PAN-OS 10, currently on PAN-OS 10.2.3 Disabled all telemetry on the firewall Disabled PAN-OS Edge Service N...

mattlede by • L1 Bithead
  • 7502 Views
  • 4 replies
  • 1 Likes

AWS-Palo VPN Phase-2 Rekeying

HI Team We have an issue with AWS Site to Site VPN, where we can see continuous rekeying of Phase-2 tunnels. It's a PA-3220 HA pair. It started happening recently as we can see previously the rekey did happen only after the Lifetime expired (Phase-2 Lifetime set to 3600 sec on both Palo and AWS). This VPN has been in place for over a year with...

Resolved! Security settings on NGFW to block dangerous user agent

Hi All, Good morning! I would like to get guidance from you regarding how to block user agents on Paloalto NGFW. I mean, when I am managing Web Application Firewalls (WAF) from other provider. I am able to configure a section within the security section in the WAF, where I can block bad bots, and any other bad user agent (e.g. python, Go lan...

Palo Alto PA 5220 running on 10.1.10 H2 is not mounting /dev/sd9 partition

When we booted up the firewall we're getting an error that AutoCommit failed to complete. This was seen while mounting the raid partitions, specifically /dev/sd9. After referring the documentation existing on Palo Alto community, in the link https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA14u000000wkxPCAQ&lang=en_US%E2%80%A9...

anfasks by • L0 Member
  • 1452 Views
  • 0 replies
  • 1 Likes

Resolved! How check NGFW valid for April 2024 Cert Advisory

Regarding the Certificate advisory for April 2024 and November 2024, if doing option 1, have content update and doing a reboot. This being good enough for the April 2024 deadline. How can you verify on the Panorama or NGFW that you are valid? The commands in the advisory FAQ 9, only work if you do Option 2 and upgrade to the recommended hotfix....

IPsec tunnel PA-Forcepoint Up but no traffic passing through

Hi , I'm configuring an ipsec tunnel between PA-5410 (route based )and Forcepoint Firewall (policy based), and showing up but when i try to ping from LAN-to-LAN i could not recieve any trafic or logs . from system log, ""PSec key deleted. Deleted SA: 172........[500]-.............peer[500] SPI:0xA83E98C1/0x3D6DB38C.'"" and ( eventid eq 'ips...

  • 1638 Posts
  • 62 Subscriptions