Next-Generation Firewall Discussions
Palo Alto Networks Next-Generation Firewalls provide true, complete visibility everywhere, along with precise policy control. Ask your questions or provide insightful answers in the discussion forum specific to NGFW.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Next-Generation Firewall Discussions
Palo Alto Networks Next-Generation Firewalls provide true, complete visibility everywhere, along with precise policy control. Ask your questions or provide insightful answers in the discussion forum specific to NGFW.
About Next-Generation Firewall Discussions
Palo Alto Networks Next-Generation Firewalls provide true, complete visibility everywhere, along with precise policy control. Ask your questions or provide insightful answers in the discussion forum specific to NGFW.

Discussions

Welcome to the Next-Generation Firewall Discussions!

To make this forum valuable and enjoyable for everyone, please review the following guidelines before participating: Rules and Best Practices Be Respectful: Treat fellow community members with professionalism and courtesy. Constructive discussions are encouraged; disrespectful or inflammatory comments are not. Stay On-Topic: This board is d...
JayGolf by • Community Team Member
  • 4787 Views
  • 0 replies
  • 1 Likes

SSH Proxy Bock Session with Unsupported Algorithm - What are the palo alto predefined unsupported SSH algorithm and version.

Palo Alto SSH Proxy blocks ssh traffic with error message unsupported Parameters. This is because of the SSH Proxy profile. However where can I find the parameter used for this communication and what is the recommended / supported parameters/algorithm... I could not find any document stating this...For SSL we can see that these parameters are ...

Different telemetry region in ha firewall

Firewall A Previously Default Device Telemetry region is America After sudden commit fails due to error : 'Americas' does not match lcaas region 'in' So i changed the telemetry to india which is present in the drop down. Now , In firewall B vice versa i am receiving error : 'in' does not match lcaas region 'america' And also there is only ame...

Impact after Changing the key size setting clears the current certificate cache.

Due to VA Scanner scan my firewall having vulnerabilities of SSL Certificate Chain Contains RSA Keys Less Than 2048 bits . So I plan to follow below KB to change the key size. https://docs.paloaltonetworks.com/pan-os/10-2/pan-os-admin/certificate-management/configure-the-key-size-for-ssl-forward-proxy-server-certificates In the KB mentioned as...

JiaXiang by • L4 Transporter
  • 3916 Views
  • 4 replies
  • 0 Likes

Resolved! How can I run a curl from PAN OS?

Hi; How can I run a curl command from PAN OS NGFW? say to some web-site. I have tried but it seems like curl is not supported. Also, it would be great to see if the curl request can be initiated from a specific IP Address on the PAN OS NGFW? The PAN OS version is 10.1 Kindly Wasfi

PA-1410 / PAN-OS 11 doesn't include many MS Root CA's

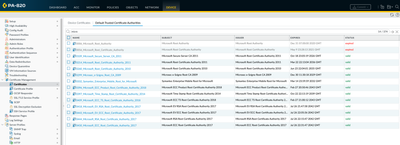
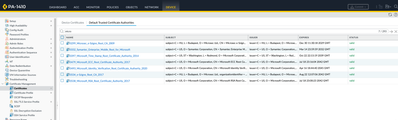
We do TLS decryption, and cutover a site to new PA-1410's running 11.0.2. While testing MS updates on endpoints, we were getting notifications that the client couldn't contact the update server. Looking in the decryption log, none of the calls to the MS URL's were trusted. I looked at the default included trusted CA's from our 820's that were...

820.png
1410.png

PAN-OS 11 interface counter descriptions

We've recently deployed PAN-OS 11.0.1-h2 in production on some PA-1400's (terrifying, I know). Practically, the firewalls seem to be functionally identical to the firewalls they're replacing. However, we've noticed that the "receive errors" counters are incrementing at a steady rate (3-5 per second). We believe the culprit to be the following ...

Resolved! PA-5400 Series Port HA1 Down every time there is an upgrade

Hi everyone, I found a problem every time we upgrade the PA-5420 firmware. After the device reboots, port HA1 is always down. I tried to find the relevant logs. It could not find any reason for this happening. Has anyone encountered this kind of problem? I want to know what is the root cause of this problem. We directly connect Active and Pass...

Resolved! BGP peering over virtual-wire interface

Hello, I have existing eBGP connection between 2 routers, layer3 connectivity is done with vlan going customer side and with /30 IP address they are peering. My question is that if i pass this BGP peering on Palo-Alto firewall with Virtual-Wire interfaces. Will I be able to see the prefix customer side of peer announcing or will I only see t...

Memmed by • L0 Member
  • 2919 Views
  • 2 replies
  • 0 Likes
  • 1633 Posts
  • 62 Subscriptions
Top Solution Authors



