Next-Generation Firewall Discussions
Palo Alto Networks Next-Generation Firewalls provide true, complete visibility everywhere, along with precise policy control. Ask your questions or provide insightful answers in the discussion forum specific to NGFW.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Next-Generation Firewall Discussions
Palo Alto Networks Next-Generation Firewalls provide true, complete visibility everywhere, along with precise policy control. Ask your questions or provide insightful answers in the discussion forum specific to NGFW.
About Next-Generation Firewall Discussions
Palo Alto Networks Next-Generation Firewalls provide true, complete visibility everywhere, along with precise policy control. Ask your questions or provide insightful answers in the discussion forum specific to NGFW.

Discussions

Welcome to the Next-Generation Firewall Discussions!

To make this forum valuable and enjoyable for everyone, please review the following guidelines before participating: Rules and Best Practices Be Respectful: Treat fellow community members with professionalism and courtesy. Constructive discussions are encouraged; disrespectful or inflammatory comments are not. Stay On-Topic: This board is d...
JayGolf by • Community Team Member
  • 4781 Views
  • 0 replies
  • 1 Likes

X-Forwarded-For on Threats logs

what`s mean below article? https://docs.paloaltonetworks.com/pan-os/10-0/pan-os-admin/policy/identify-users-connected-through-a-proxy-server/use-xff-values-for-ip-based-security-policy-and-logging For non-URL Filtering logs, XFF IP logging is supported only when packet capture is not enabled.-->> It mean that XFF ip is visible only whe...

Palo Alto Service Route config for Dynamic Update/Wildfire/IPS

Hi, What service source interface I need to change for IPS /Dynamic/Wildfire Update ? We want to configure custom interface instead of Management interface.Now I've configured custom source interface for "External Dynamic Lists" and "URL Updates" but the system still using management interface for IPS and Wildfire Update. Do I need to change sou...

EvanRaci_0-1681107358954.png
EvanRaci by • L1 Bithead
  • 3023 Views
  • 2 replies
  • 0 Likes

IP Block List Feeds

We're looking to add a dynamic block list rather than manually blocking bad IP's as we find them. I understand that Palo Alto comes with one or more of these feeds, do we know how often they are updated?Asking for a friend.

Resolved! Global Protect VPN User did Not Sign Out Automatically after Disconnected

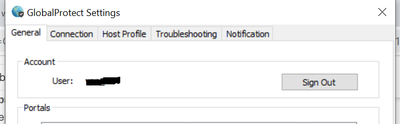
Hi All, After we connected GlobalProtect VPN, the GlobalProtect Client App is not asking for username and password again for the next login. We need to manually sign out from GlobalProtect Client to completely logout the user. Is it normal for GlobalProtect Client App to still Sign in even after disconnected? Are there any way to configure at P...

EvanRaci_0-1680621682641.png
EvanRaci by • L1 Bithead
  • 3805 Views
  • 1 replies
  • 0 Likes

how to stop sending duplicate user-ip-mapping by xmlapi

hello..we are using UIA and ClearPass (login/loginout type) to get user-ip-mapping. the issue is Palo Alto firewall is receiving duplicate user-ip-mapping. user-A (using) : 192.168.1.100 receiving from User ID Agent correctly. user-B(not using): 192.168.1.100 receving from XMLAPI incorrectly. user-B ip-user-mapping is sending periodically 45 min...

zinkt101 by • L1 Bithead
  • 2453 Views
  • 2 replies
  • 0 Likes

Resolved! The traffics tab does not appear on the monitor.

Cordial greetings Engineers A PA-410 device with version 10.1.3 has arrived and we identified that in the monitor tab you do not see all the possibilities to see the FW logs (I attach image). Similarly, the device was updated to version 10.2.3-h4 but the behavior remains the same. Does anyone know the reason for this behavior?

Device Telemetry can't be removed/disabled from Panorama and/or local

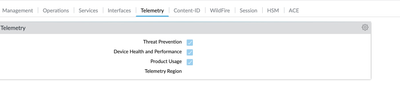
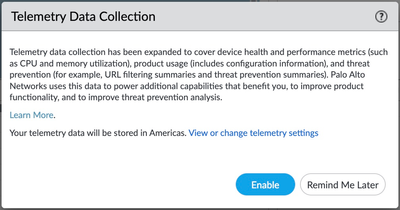
We currently have difficulties to remove the Device Telemetry options in any way. it seems as this Options doesn't work as expected. This issue persisted across several Versions of PanOS / Panorama Panorama 10.2.2-h2 - When trying to remove the device telemetry options from the template stack the settings are still checked and a commit & ...

mattlede_0-1662714252725.png
mattlede_1-1662714278257.png
mattlede by • L1 Bithead
  • 16792 Views
  • 15 replies
  • 1 Likes

URL Filtering is not working for Global Protect users

Hi all, We have a requirement of GP user should access certain URLs. But once i assign the URL category in security policy, GP user is not getting internet access.. SCENARIO 1 : Security Policy: Source > GP & Source user Group Destination > WAN Action > Allow Internet is working with full access. SCENARIO 2: Security Policy...

Having issues with Vmware horizon client RDP application through palo alto

The initial login works fine but when we try to open any RDP session, it gives an error as “Unable to Connect". But when on the personal network it works fine. Do not see any drops on the firewall, the initial connection is on TCP 443 after which a connection to tcp/4172 PCOI is created and is terminated by a TCP-FIN. Tried to provide an access...

Resolved! PA3020 EoL vs PanOS 9.1 EoL

Hi there, Checking this page, https://www.paloaltonetworks.com/services/support/end-of-life-announcements/end-of-life-summary I see that the EoL for PanOS 9.1 is December 2023. This page, https://www.paloaltonetworks.com/services/support/end-of-life-announcements/hardware-end-of-life-dates shows the Eol for the PA3020 to be October 2024. Howe...

Ander by • L0 Member
  • 3660 Views
  • 1 replies
  • 0 Likes

Firewall crash after executing this command : debug dataplane show dns-cache print

Hello, After exceuting this command : debug dataplane show dns-cache print My firewall crashed and failover happened. I saw in the in the failover this error : "non-fonctionnal (Dataplane down : path monitor failed) After firewall restart and some manipulation the firewall is up again. Do you know why this command made crash the firewall...

Mamoudou by • L2 Linker
  • 2145 Views
  • 1 replies
  • 0 Likes

FW stops forwarding files to WF 500

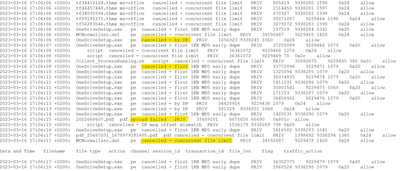
Hi, We have a PA-5250 that suppose to send files to a WF-500 appliance. Both are at 10.2.3 version. The FW suddenly stopped sending file to our private wildfire cloud. When we checked the "wildfire-upload.log" we see the following: "cancelled - first" "cancelled - concurrent file limit" "cancelled - by DP" Does anyone knows what can be the reas...

AmitKa79_2-1678982036842.png
AmitKa79 by • L2 Linker
  • 1805 Views
  • 1 replies
  • 0 Likes
  • 1632 Posts
  • 62 Subscriptions
Top Solution Authors