VM-Series in the Public Cloud
The VM-Series is the virtualized form factor of the next-generation firewall. Use this discussion as a resource to discuss VM-Series deployments across public clouds like AWS, Microsoft Azure, Google Cloud Platform, Oracle Cloud, and Alibaba.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
VM-Series in the Public Cloud
The VM-Series is the virtualized form factor of the next-generation firewall. Use this discussion as a resource to discuss VM-Series deployments across public clouds like AWS, Microsoft Azure, Google Cloud Platform, Oracle Cloud, and Alibaba.
About VM-Series in the Public Cloud

Welcome to the VM-Series in the Public Cloud discussion forum! This community exists as a resource for you to discuss VM-Series deployments on AWS, Microsoft Azure, Google Cloud Platform, Oracle Cloud and Alibaba. We encourage you to engage in this rapidly growing community to share ideas, pose questions, and propose real-world solutions to any challenges that may arise.

Disclaimer:
This forum is provided for Live Community members to discuss and share information pertaining to the VM-Series deployments on AWS, Microsoft Azure, Google Cloud Platform Oracle Cloud and Alibaba. Please use the information from this forum at your own risk and make sure to test and verify proposed solutions presented here. For information on contacting Palo Alto Networks support, click here.

Discussions

Welcome to the VM-Series in the Public Cloud Discussions!

To make this forum valuable and enjoyable for everyone, please review the following guidelines before participating: Rules and Best Practices Be Respectful: Treat fellow community members with professionalism and courtesy. Constructive discussions are encouraged; disrespectful or inflammatory comments are not. Stay On-Topic: This board is d...

JayGolf by • Community Team Member
  • 3736 Views
  • 0 replies
  • 0 Likes

NGFW with azure gateway load balancer

If I have an Azure Gateway Load Balancer set up with my NGFWs (Interface eth1/1), do I have to use a separate interface for traffic originating inside Azure to point to? I would assume yes since GWLB technically uses vxlan and so I'd need a separate interface to stick in the backend pool of an internal LB I have set up (where all the default rou...

How to retain Public IP Address Assigned to a host on VMSeries Firewall on Azure

Hello Community, I want to deploy Palo Alto VM Series firewall Infront of some workloads already existing on my Azure tenant and still ensure that services calling the workloads use the existing public IP Addresses assigned to these workloads when the traffic passes through the VM Series firewall. It is easier to deploy when workloads haven'...

ORufai by • L0 Member
  • 2921 Views
  • 1 replies
  • 0 Likes

2 Palo Alto VM-Serie for IPsec VPN

Hello We deploy 2 VM-Series on Azure as recommanded by PA. These 2 FW manage Inbound/Outbound traffic and between our internals zones. A public load balancer have been configured. We need to connect our Azure infrastructure with our local datacenter via IPsec VPN between PA on Azure and firewall on our datacenter. Do you know if it's possibl...

Resolved! VM - Series

Hello, people! I have a important question to solve. So I think here is the right place to ask. When we talk about VM Series and looking for a different licenses, can you tell me the difference between VM-100 and VM-100-ENT? What kind of licenses we have when we talk about VM-100 and VM-100- ENT? What is a main difference between them? In which...

AWS, gw loadbalancer and geneve

hi, I have set up two palos in different az's in AWS. I have utilized the gw lodbalancers and done the bootstrapping so to get them "healty" etc. The soultion is working fine!! But I am having a very hard time understanding how to get the panorama access working. I have panorama running on prem, and will be managing the palo's in AWS utilizin...

Packets loss but no drops - VM Series, AWS, GWLB

i have a server sending traffic on 443 through GWLB to my Palos and out to the internet The logs all say 'aged out' Packet capture reveals the SYN arriving wearing GENEVE, being de-encapsulated, source NATed and forwarded out Untrust The SYN/ACK arrives on Untrust, but there is no record of the firewall forwarding these packets to GWLB and...

Palo Alto and Azure Application Gateway

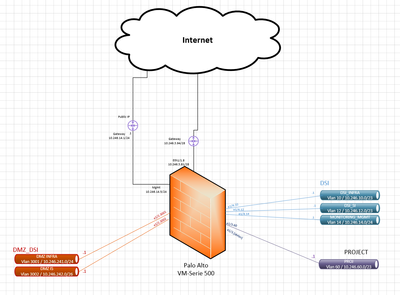
Hello I'm deploying infrastructure on Azure with Palo Alto firewall. We will host web application (appli1.company.com & appli2.company.com) on a vnet dmz. My design is based on Hub/Spoke configuration and I configured an vNet Peering between my DMZ vnet and my Hub where is hosted the firewall. I would like to be able to access from Inter...

jeromecarrier_0-1666942498038.png
jeromecarrier_1-1666942586263.png

VM-500: HA1 Down, HA1 Backup Up, HA2 Up.

NOTE: This appears to have been an issue in the Cloud space. I suspect a VMotion or reboot of the VM Host resolved the problem as an unrelated issue with spinning up access to the VM was resolved at the same time this HA issue was resolved and no configuration changes were made. ------------------------------------------------------------------...

Configuration VM-Series on Azure cloud

Hello I'm deploying my first Palo Alto on Azure (I already deployed physical appliance) but I'm blocked. I would like to deploy this type of design. The global network defined is 10.200.0.0/16 who are splitted in serverals sub-networks. I have one Untrust zone for Internet access and several zone for networks where we host our servers for I...

jeromecarrier_1-1664963571129.png

Resolved! D-NAT not working in GCP

Hello Everyone, I have deployed PA-VM in GCP. In that we have configured 3 VPCs (MGMT, Untrust & Trust). In the Trust VPC we have created Windows Server 2016, in PA we created D-NAT & Security policy. In GCP, Under Trust VPC Firewall Ingress traffic is allowed & Route is forwarded to PA-VM instance with 500 priority. For Untr...

Packets being denied intermittently.

My company has had an issue for over a year and Palo Alto cant figure it out. We're using Azure's Palo Alto offering. * We have a security rule that is sourced from our trusted paas and destined to Azures Paas storage. Port 1433 app id: mssql db encrypted.* Multiple times a week traffic all of a sudden goes from being allowed under a specifi...

AWS and Inbound SSL Inspection

Hello all, After some help as not getting much from support. We have a customer with an Amazon AWS solution. We have a web server in the trust zone and we have been asked to set up inbound ssl inspection. There is a load balancer after the firewalls. The client uses an Amazon cert of some sort and we have created a cert and private key on the ...

how to setup palo alto for dual stack for IPv6 internet

Hi, I have configured PAVM in azure with IPv4 and everything is working fine. so I decided to add IPv6 as a Dual stack. And Azure provided me single Public IPv6 and it configures on the Azure load balancer and mapped with an untrust interface on the firewall with my private IPv6 range fd6e:8b94:25ca:b001::/64, and on trust interface range is fd6...

  • 535 Posts
  • 107 Subscriptions
Top Liked Authors
Labels