General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Announcements
Scheduled Maintenance: November 14–15 (starting Nov. 14 at 12:00 AM PST)
LIVEcommunity will temporarily operate in read-only mode as we prepare to welcome Idira!
Public content will remain accessible, but log-ins, posting and community interactions will be paused during this period. Thank you for your patience!
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

PA 1410 MGMT port will not establish a 1000/FULL connection to Nexus 9k

We noticed that the management port of our PA1410s will not negotiate to 1000/FULL when connected to a Nexus 9k switch port (Not a quad, normal port). Using the same cable, if we connect a laptop to the PA it negotiates to 1000. Same if we connect a laptop to the same switch port. This was attempted with two different 6e cables. Same result. ...
IDIRA SIA Target validation failure

While i am using the IDIRA SIA to connect to a windows Server using ZSP policy, I am getting Certificate validation failed error. In the global Settings, i have disabled the target validation. Somehow it is still ding the target validation. Anyone else face this problem ? Can you suggest where else i can check ?

PAN-OS 11.1 — Source-Based DNAT on TCP 443 While GlobalProtect Uses Same Public IP

Subject: PAN-OS 11.1 — Source-Based DNAT on TCP 443 While GlobalProtect Uses Same Public IP We have a PA-460 running PAN-OS 11.1.10-h1. Our GlobalProtect portal and gateway are both bound to ethernet1/1 on the same public IP, using TCP 443. Authentication is handled through Duo SAML. We need to expose an internal HTTPS/WCF application on TCP 443...

mikeb by • L0 Member
  • 141 Views
  • 1 replies
  • 0 Likes

Google captcha error

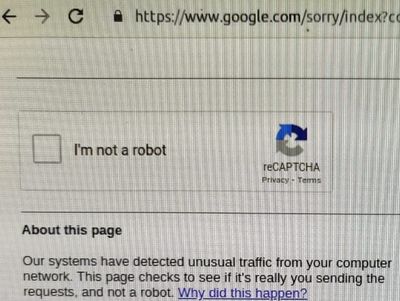
Most of the users are getting captcha error in google.com Wondering why PA is not blocking such requests. Will the DOS policy in PA help prevent such unlimited outbound queries? Page says our systems have detected unusual traffic from your computer network.

google2.jpeg
ceapen01 by • L2 Linker
  • 4427 Views
  • 5 replies
  • 0 Likes

5th Gen Hardware | ARE | PANOS 12.1

Just throwing this out there for everyone. Sounds like the 5th gen hardware x5xx HAS to run Advanced Routing Engine (ARE.) Palo has fully redesigned the routing functionality and gotten rid of the "virtual router" for the new "logical router" in ARE. This should be a huge consideration for admins as you look to migrate from 3rd gen (ie 5200s)...

Help registering a PA-440 bought online in the US

Help registering a PA-440 bought online in the US for use in Oman Hi everyone, I bought a PA-440 firewall online from a seller in the United States. The unit is now in Oman, where I plan to use it at SpiritHub Roastery. It’s still unregistered, and I’m trying to register it under our company’s Customer Support Portal account. I’ve contacted Palo...

info by • L0 Member
  • 139 Views
  • 2 replies
  • 0 Likes

Unable to Create a New Support Case – Portal Access Issue

Hi Team, I am encountering the error message shown in the attached screenshot when trying to create a new support case. After logging into the portal, when I attempt to create a case for one of my customers, I receive the attached error message. Could you please look into this issue and help me resolve it? Please let me know if you need any addi...

Trying the DNSProxy feature for Static Response

Hie, Situation - Wanted to kaminsky the DNS Responses for my client from the FWComplication - None of the dig are responded Need your help on this? Client Requests for Promise/Spoofed IP keviv@keviv-VMware-Virtual-Platform:~$ ifconfig ens37ens37: flags=4163<UP,BROADCAST,RUNNING,MULTICAST> mtu 1500inet 192.168.21.21 netmask 255.255.255.0 ...

ocpfn4 by • L0 Member
  • 649 Views
  • 1 replies
  • 0 Likes

Resolved! Panorama SD-WAN Plugin Compatibility

Hello All! Seeking clarification on whether or not I need to upgrade my Panorama SD-WAN plugin. Currently, I am running PAN-OS 10.2.x and using SD-WAN plugin version 3.0.3. In the compatibility matrix the maximum PAN-OS version listed for this plugin version is "Latest". Does this refer to the latest version based on the minimal PAN-OS versio...

nohash4u by • L3 Networker
  • 412 Views
  • 2 replies
  • 0 Likes

How to disable Telemetry?

How do you actually disable this new cloud telemetry? Last week I performed a PANOS update on my cloud NGFW firewalls and telemetry was forced on. The blurb in the firewall says to visit Hub->TenantManagement or Hub->StrataCloudManager->Settings->Tenant, neither of which exist as a path. The built-in PANOS documentation page says n...

2026-10-13_095412.png

About CVE-2026-91403

We are currently verifying whether we are affected by the Java-related vulnerability (CVE-2026-91403). 1. After reviewing Palo Alto’s security advisory,we were unable to confirm the existence of the Java-related vulnerability (CVE-2026-91403). Does this mean it has not yet been disclosed, or that we are not affected? 2. I checked the manufactu...

n-tomo by • L2 Linker
  • 320 Views
  • 1 replies
  • 0 Likes
  • 24483 Posts
  • 125 Subscriptions
Top Solution Authors
Labels





