Cortex XDR Discussions
Cortex XDR allows you to rapidly detect and respond to threats across your networks, endpoints, and clouds. It assists SOC analysts by allowing them to view ALL the alerts from all PANW products in one place, telling the full story of what actually happened in seconds and allows seamless response.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Cortex XDR Discussions
Cortex XDR allows you to rapidly detect and respond to threats across your networks, endpoints, and clouds. It assists SOC analysts by allowing them to view ALL the alerts from all PANW products in one place, telling the full story of what actually happened in seconds and allows seamless response.
About Cortex XDR Discussions

Cortex XDR allows you to rapidly detect and respond to threats across your networks, endpoints, and clouds. It assists SOC analysts by allowing them to view ALL the alerts from all PANW products in one place, telling the full story of what actually happened in seconds and allows seamless response.

Please note: All postings in LIVEcommunity are visible to other users; please keep your network secure by refraining from posting live IP address’s or domain names here. Contact your Customer Success team for network-specific questions.

Discussions

Welcome to the Cortex XDR Discussions!

To make this forum valuable and enjoyable for everyone, please review the following guidelines before participating: Rules and Best Practices Be Respectful: Treat fellow community members with professionalism and courtesy. Constructive discussions are encouraged; disrespectful or inflammatory comments are not. Stay On-Topic: This board is d...
JayGolf by • Community Team Member
  • 4633 Views
  • 1 replies
  • 3 Likes

Resolved! Automation rules

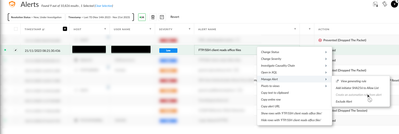
Hi all! Still fairly new to Cortex XDR. Currently trying to make some sensible alert automation rules.I have a specifik alert that puzzles me. I get some "FTH/SSH client reads office files" alerts. I have a legitimate use case for this, so I want to automatically resolve these alerts for a particular set of hosts.But ... I am not able to create ...

Allan_Holdt_0-1700558668197.png
aholdt by • L1 Bithead
  • 2815 Views
  • 2 replies
  • 1 Likes

Scaning files for malware

Is it possible to use Cortex XDR to analyse malicious Microsoft Office files, such as Word, Excel and PowerPoint documents? If I right click on Office file and choose Scan with Cortex XDR will Cortex check if that file is not used for delivering malware, including binary files, documents, scripts, archives a macros?

Sedlacek by • L0 Member
  • 2388 Views
  • 2 replies
  • 0 Likes

Legacy Exceptions - Endpoint version compatibility

Hi, everybody, I plan to accept Legacy Exceptions générated from my profile based policies. Major part of the endpoints are running [CE] versions, prior to 7.9. All these versions are supported. Does anyone had problems when activating these Legacy Exceptions in regard of ther endpoint versions? Thank's a lot ! Cheers.

What happens to existing prevention profiles when enabling the "Host Insights" license?

Hello Does anybody know what happens to the configuration of existing prevention profiles when the "Host Insights" license is activated? The environment currently has several prevention profiles that have the "XDR Pro Endpoint capabilities" enabled. The settings for host insights will appear under that setting according to this deployment vid...

Automate Isolation Endpoint

Just wondering if there is somewhere in xdr to tell it to isolate an endpoint automatically if we get a critical/high/medium alert or confirmed malware/ransomware alert. I thought there was something in the profiles to change for active this function.

Resolved! Unable to install XDR agent in Window server 2019 and 2022

Hi I have issue installing Cortex XDR 8.2.0.45438 on both 2019 and 2022 Server. with error logs below: ExecServiceStartCA: Service: cyserver ExecServiceStartCA: Error 0x800705b4: Service failed transition to 4 state (current state 1) ExecServiceStartCA: Error 0x800705b4: Failed, retrying (attempt no. 1)... ExecServiceStartCA: Error 0x8...

Resolved! Evasion Technique - 3348100960

“Behavior of hiding RWX code by modifying it to RX” I've been seeing this alert that is considered high criticality and is blocking Windows updates. Everything I can see says that this is benign. XDR is saying that the Windows process is a non-whitelist CGO. I've verified that this is the legitimate Microsoft WerFault.exe There is no desc...

CharlieJohnstonNTS_0-1699971904273.png
CharlieJohnstonNTS_1-1699972124759.png
CJNTS by • L2 Linker
  • 3068 Views
  • 1 replies
  • 0 Likes

Deploying Cortex XDR Agent for macOS with VMware Workspace ONE (AirWatch)

In order to deploy the Cortex XDR Agent to macOS you have to have both the Config.xml and Cortex XDR.pkg files bundled in the same deployment file. Workspace ONE does not support the uploading/deployment of a .zip file so you have to use a workaround. Cortex XDR Agent Application:1. You will first need to pull the Cortex XDR Uninstaller out of ...

BWilga by • L0 Member
  • 8249 Views
  • 5 replies
  • 3 Likes

Cortex XDR trail version for testing purpose.

We are trying to integrate the Cortex XDR incident logs to Splunk using the API pull method. We customised the Splunk TA taking reference from the Splunk TA for Palo Alto NW. So is there a trail version of Cortex XDR available in order to test the integration using API or is there any other ways to test the custom made Splunk TA?

RK21VTH by • L0 Member
  • 2669 Views
  • 1 replies
  • 0 Likes

Script for Agent Upgrades

Does anyone know of a way to build/apply a script in XDR that would perform agent upgrades at scheduled times? Example: upgrade to latest agent version on 10 endpoints starting at 8PM on Saturday.

Disk Decryption on MAC OS

Hi Everyone, I'm seeking for help on how to decrypt the drive on MAC OS after the encrypting the drive using the Cortex XDR Tenant/Console? I tried to check and use on this documentation guide by Palo Alto Networks but I think it is not working or do I miss something. https://docs-cortex.paloaltonetworks.com/r/Cortex-XDR/Cortex-XDR-Pro-Admin...

EJaspe by • L1 Bithead
  • 2177 Views
  • 3 replies
  • 0 Likes

XDR and XSOAR mirroring fails

Hi, I have XDR integrated with XSOAR for bidirectional incident mirroring... The strange thing is that when I close incidents in XSOAR as false positives, they appear as 'Resolved other' in XDR via the API...If I close incidents as false positives in XDR through an automation rule, they remain open in XSOAR... Does anyone know what this migh...

tlmarques by • L4 Transporter
  • 1970 Views
  • 2 replies
  • 0 Likes
  • 2663 Posts
  • 102 Subscriptions
Top Solution Authors
Top Liked Authors



