GlobalProtect Discussions
GlobalProtect discussions offers topics about our network security for endpoints that protects your organization's mobile workforce. This area is dedicated to GlobalProtect discussions to help you answer questions.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
GlobalProtect Discussions
GlobalProtect discussions offers topics about our network security for endpoints that protects your organization's mobile workforce. This area is dedicated to GlobalProtect discussions to help you answer questions.
About GlobalProtect Discussions
Welcome to the GlobalProtect discussion area! Here, you can engage in conversations about GlobalProtect, explore new insights, and stay updated on ongoing discussions. Check back regularly for the latest updates and community insights on GlobalProtect.

Discussions

Pre Logon then on Demand traffic flow

Hi Community, We have GP prelogon then on demand.For pre logon we are using machine cert for authentication.For on demand we are using SAML MFA. I see that prelogon works fine for few users but one they logon to PC and click on connect they get error that PCis not in intune. So need to understand that for pre logon it uses only machine cert for ...

Retain Connection on Smart Card Removal behavior on GP

Hello, There are Smart Cards being used for the GP authentication. One of the options for Windows endpoints is to disconnect the GP as soon as Smart Card is removed and that was tested, option in the app settings: "Retain Connection on Smart Card Removal" set to No.But the result after removing the Smart Card is that prompt is shown to the user ...

nikoo by • L3 Networker
  • 4970 Views
  • 4 replies
  • 0 Likes

global protect clientless using guacamole

Hi all,Start working with global protect using MFA and try using guacamole for proxy rdp connection.after building the guacamole server (updated one using Guacamole 1.1 on Ubuntu 20.04) the server is working on the internal network but when accessing it from outside I get the following message. Access Error: 404 -- Not FoundCan't locate document...

SShnap by • L3 Networker
  • 11193 Views
  • 5 replies
  • 0 Likes

Radius Auth Profile with PEAP-MsCHAPv2

Has anyone successfully integrated Radius Auth profile PEAP-MsCHAPv2 with NPS or any other Radius platform? I have configured my Radius Auth Profile and attached relevant Cert profile to it as per below knowledgebase article.https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000CmkRCASHowever we are unable to establish succes...

NamalW_0-1600837232072.png
Namalw by • L2 Linker
  • 12760 Views
  • 2 replies
  • 0 Likes

Resolved! Restrict GP gateway selection to specific user groups via panorama

Due to some internal department/company shuffling we have a requirement to authenticate a specific subset of our user base via ldap only, bypassing our existing SAML setup. Reading other forum posts and Palo docs I've learned that once you enable SAML on a gateway that's pretty much all you can use, so I'm looking at setting up a secondary gatew...

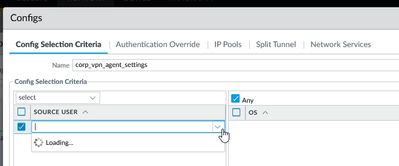
jjsimpson_0-1620934233088.png
jjsimpson_1-1620934447675.png
jjsimpson_2-1620934681139.png

Event Reminder: GlobalProtect - Secure and Seamless Remote Workforce Deployment

Hey everyone, Just incase you missed it, I wanted to take a second and let everyone know about a new LIVE event that is happening on July 6th at 8 AM PDT. This event is going to be all about GlobalProtect and how to deploy a secure and seamless remote workforce. It is going to be a Live interactive event that will be covering all aspects ...

jdelio_0-1623773094470.jpeg
jdelio by • L7 Applicator
  • 3467 Views
  • 2 replies
  • 1 Likes

Blank page on internet explorer when opening email links

I have a few users reporting problems with opening some web pages in internet explorer (IE) when connected to GlobalProtect. Clicking on the email link simply opens up a blank page in IE. When the same link is pasted in Chrome, it works OK.When using Cisco AnyConnect, the problem with IE does not occur and email links open as normal. Has anyone ...

MartinE by • L2 Linker
  • 5718 Views
  • 2 replies
  • 0 Likes

Resolved! using local database of user for GP but adding DUO as 2FA doesn't work

hello team we are trying to using local database of user for GP but adding DUO as 2FA doesn't work, still is not working we follow the below link from DUO: https://duo.com/docs/paloalto#:~:text=Click%20on%20your%20configured%20GlobalProtect,Profile%22%20selections%20for%20client%20authentication. we use the SAML option but when we try to authent...

GLOBAL PROTECT login failing intermittently with 2 factor authentication for security groups

We are implementing 2 factor authentication and it is failing intermittently when using security groups in the authentication profile. When we use "all" in the LDAP tree, it works like a champ. When we go to a single group, it fails with "user not in allow list" but when checking the user database, the user-id is listed. If we use the same au...

RRAPP by • L1 Bithead
  • 3489 Views
  • 3 replies
  • 0 Likes

GlobalProtect Linux CLI - connect pre-logon

I'm trying to configure my client to automatically connect to the VPN when it is booted. This should happen before a user logs on. My shell script in cron is not running @reboot. The client connects perfectly when run by the user, but not pre-logon. The client version is deb_5.1.1.

cfinkenb by • L0 Member
  • 5280 Views
  • 2 replies
  • 0 Likes

HIP checks for anti-malware and mobiles

We want to enable HIP check on anti-malware for Windows and Mac. I have configured the HIP objects, Profile, and notifications for no match which is working but two issues. 1. the notification shows when IOS and android mobiles connect.2. How can I apply this to a policy to restrict for Windows and Mac unless they have up to date AV software and...

nathanh1 by • L0 Member
  • 4192 Views
  • 3 replies
  • 1 Likes

Resolved! Excluding MS Teams from GlobalProtect

I'm trying to exclude MS Teams traffic from GlobalProtect. We are using the entire O365 platform but I only want to exclude MS Teams. Has anyone been able to successfully get this to work? I found some older community posts but most seemed to have inconsistent results. I'm running PAN OS 9.0.x and GP 5.2.6. Is excluding "%LOCALAPPDATA%\Mic...

Does Global Protect support LEEF format on forwarding the log to Qradar

Hi Everyone, Greeting!!I have a concern regarding the Global protect log forwarding for forwarding the logs to Qradar SIEM Tool. The concern is about whether Global Protect support for LEEF Format if it does support i want a document that contains the required fields about the Global protect to be sent to the SIEM Tool.I want to confirm two thin...

Disable NetBIOS over TCP/IP on PANGP Virtual Ethernet Adapter?

It is our corporate policy standard to disable NetBIOS over TCP/IP for the IPv4 component of all network adapters on corporate devices as a preventative security measure. This is achievable via powershell scripting on all Windows devices. However, we run into issues with the PANGP Virtual Ethernet Adapters being created by the GP 5.1.x softwar...

jsykora by • L1 Bithead
  • 8631 Views
  • 1 replies
  • 0 Likes
  • 1722 Posts
  • 67 Subscriptions
Top Solution Authors
Top Liked Authors
Labels