General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Announcements

Welcome Idira to LIVEcommunity!

Our community just got stronger! Explore new identity security resources, connect with experts, and discover more ways to learn and collaborate.

Meet Idira

General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

GlobalProtect Release for Ubuntu 26.04 LTS ?

Hello together.recently was the new Ubuntu 26.04 LTS release, until now the provided GlobalProtect client supports only Ubuntu 24.04:https://docs.paloaltonetworks.com/compatibility-matrix/reference/globalprotect/where-can-i-install-the-globalprotect-app?otp=linux#linux When can we expect the new GlobalProtect version for Ubuntu 26.04 ? Best re...

Management Tenant for on-prem customer

How do I request a light or management tenant in Idira so that a customer can download from the Idira Marketplace? The customer opened a ticket, but was directed by Support back to the sales team. I can’t seem to open an Idira ticket. Idira isn’t an option that I can pick from.

TCP-RST-FROM-CLIENT and TCS-RST-FROM-SERVER

Hi All, As captioned in subject, would like to get some clarity on the tcp-rst-from-client and tcp-rst-from-server session end reasons on monitor traffic. Even with successful communication between User's source IP and Dst IP, we are seeing tcp-rst-from-client , which is raising some queries for me personally. Are both these reasons are normal ...

Jimmy20 by • L2 Linker
  • 330537 Views
  • 8 replies
  • 2 Likes

SSL Decryption Issue on PA-520 Running PAN-OS 12.1.7-h3

We are experiencing an issue with SSL decryption on a PA-520 running PAN-OS 12.1.7-h3. After enabling decryption, the firewall operates normally for approximately three hours. However, over time, the number of decryption failures gradually increases until all new connections are rejected. Disabling decryption immediately restores normal operatio...

PA 1410 MGMT port will not establish a 1000/FULL connection to Nexus 9k

We noticed that the management port of our PA1410s will not negotiate to 1000/FULL when connected to a Nexus 9k switch port (Not a quad, normal port). Using the same cable, if we connect a laptop to the PA it negotiates to 1000. Same if we connect a laptop to the same switch port. This was attempted with two different 6e cables. Same result. ...

R.Dervan by • L0 Member
  • 147 Views
  • 1 replies
  • 0 Likes

We are currently assessing the scope of the CVE-2026-119618 and CVE-2026-123158 vulnerability.

We are currently assessing the scope of the CVE-2026-119618 and CVE-2026-123158 vulnerability. Based on Palo Alto’s official documentation, there does not appear to be any information indicating that CVE-2026-119618 and CVE-2026-123158 affects their products. Therefore, we understand that Palo Alto products are not affected by this vulnerabi...

n-tomo by • L2 Linker
  • 381 Views
  • 1 replies
  • 0 Likes

No proposal chosen ikev1

After upgrading to panos preffered version 12.1.7-h3 my ikev1 ipsec tunnel with ipsec crypto md5,3des,nopfs is not coming up , knowing that ike phase 1 is successful but ike phase 2 is giving no proposal chosen error , the algorithms matches the other peer and i tried downgrading the tunnel came up, i would appreciate any help

IDIRA SIA Target validation failure

While i am using the IDIRA SIA to connect to a windows Server using ZSP policy, I am getting Certificate validation failed error. In the global Settings, i have disabled the target validation. Somehow it is still ding the target validation. Anyone else face this problem ? Can you suggest where else i can check ?

PAN-OS 11.1 — Source-Based DNAT on TCP 443 While GlobalProtect Uses Same Public IP

Subject: PAN-OS 11.1 — Source-Based DNAT on TCP 443 While GlobalProtect Uses Same Public IP We have a PA-460 running PAN-OS 11.1.10-h1. Our GlobalProtect portal and gateway are both bound to ethernet1/1 on the same public IP, using TCP 443. Authentication is handled through Duo SAML. We need to expose an internal HTTPS/WCF application on TCP 443...

mikeb by • L0 Member
  • 204 Views
  • 1 replies
  • 0 Likes

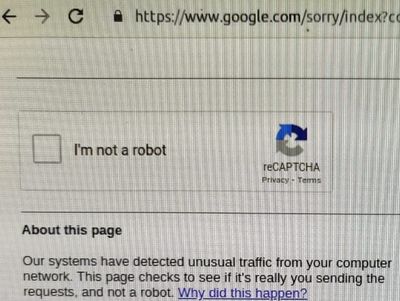
Google captcha error

Most of the users are getting captcha error in google.com Wondering why PA is not blocking such requests. Will the DOS policy in PA help prevent such unlimited outbound queries? Page says our systems have detected unusual traffic from your computer network.

google2.jpeg
ceapen01 by • L2 Linker
  • 4488 Views
  • 5 replies
  • 0 Likes
  • 24487 Posts
  • 125 Subscriptions
Top Solution Authors
Labels