General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

how many LDAP servers

How many LDAP servers can be defined in the LDAP server profile? I have 4 currently and am being asked if there is a limit. Thanks

jclingan by L0 Member
  • 4411 Views
  • 2 replies
  • 0 Likes

Migrate from Virtual Wire Mode

I am currently using the PA-500 in virtual wire mode, including monitoring, AV, Malware, etc. and web filtering. I want to start transitioning to layer 3 in order to move off of our Cisco ASA (currently sits on the inside of the PA500). What is the best way to start this process without lossing my current setup and with minimum downtime? Outs...

jharlow by L3 Networker
  • 3156 Views
  • 2 replies
  • 0 Likes

Lync 2013 | Skype 2015 > How to setup Security (app-id / ports) for transparent AV/Sip/Web Services

Palo’s I have searched, read these forums and have gone through many manuals, suggestions from the Internet regarding Palo (2020 Series) configuration to secure Lync 2013 / Skype Business 2015: but still experiencing some issues with how to setup our Firewall for Federation access. From a company perspective, our Lync is working great, our exter...

Only correlated events with "critical" severity shows up in Panorama.

Hi All, I tried to look up for this info, but didn't get much help. Not all "correlated events" are showing up in Panorama, If I change my context to the individual firewall I can see all correlated events. But the only ones that appear to forward to panorama are the ones flagged as "critical" severity. Also based off my reserach, I do see ...

bsyeda by L2 Linker
  • 4084 Views
  • 1 replies
  • 0 Likes

Resolved! Create test syslog

I want to know when our PBF rule hits by sending an email when sees the syslog. I want to test this but don't want to actually fail traffic over. There are test commands on the cli but haven't been able to find how to create a false syslog. Please let me know how to create a false syslog. Thank you

treese by L3 Networker
  • 17168 Views
  • 8 replies
  • 0 Likes

Static IP's for VPN Users?

I have a customer that is asking if its possible to assign static addresses to VPN users. This is required because of existing upstream firewalls that have ACLs tied to source IP addresses. This is done so that users can VPN into the network and then gain access to specific resources that are managed by a different group. I was wondering if anyo...

Set user ID issue

Hi..All I have a problem with the user ID.A year ago, I have configured the MS Active Directory and user ID.Today I found that the user ID does not work properly.I was just checking the problem IP- user-mapping count is zero,but the number of IP- user-mapping-MP is normal.Is it for some reason the other information? And why is that management pl...

wooki by L1 Bithead
  • 2627 Views
  • 1 replies
  • 0 Likes

Resolved! Slowness with http file transfer after placing PA in-line

We recently place firewall in-lline and now when needing to use http file transfer it takes over 5 min. Before PA's in transparent mode it was a 20sec process. Is there any thing I can check to see why this is now happening? Or something I need to modify? Over scp works fine but we are not looking to use SCP as primary file transfer method.

Configuring GlobalProtect with Wildcard Certificate

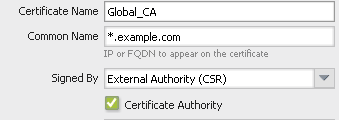
Hi All, I'm configuring GlobalProtect for the first time and would like to ask a few questions about using a Wildcard certificate to set this up. After going through the below document, I have some questions: https://live.paloaltonetworks.com/t5/Management-Articles/How-to-Use-a-Wildcard-SSL-Certificate-with-Subject-Alternative/ta-p/52849 1. Th...

gp1.png
Bocsa by L3 Networker
  • 14436 Views
  • 2 replies
  • 0 Likes

Allowing Lync: enabling SSL decryption blocks it

Hi, In a test setup I'm trying to allow MS-Lync while SSL decryption is enabled. I've got a general rule to enable SSL Decryption with the proper certificate installed on the clients end. In my security policies I've got a rule to allow Lync based on App-ID. Lync however refuses to even sign in. The only thing I have noticed that DNS reques...

Allow-Lync.PNG
age out.PNG
Arne-VDH by L3 Networker
  • 3989 Views
  • 3 replies
  • 0 Likes

Resolved! Restart GUi

Have an issues to where no matter what browser I use GUI will never load. Is there a service I can restart via GUI to restart

Resolved! Convert Template to Template Stack

We use Panorama to manage our firewalls and have a template configured with settings for all of our devices. I would like to split the devices by region for administrative access and would like to retain the current settings in the template. I can create a new stack, but would lose the settings in the current template so wondered if it's possibl...

Ash2k by L2 Linker
  • 7502 Views
  • 3 replies
  • 0 Likes

Resolved! XML API commit-all not working

Hi all, Does anybody have an idea why the following happens, and what the solution might be? I'm trying to perform a commit-all via the REST API using the the following URL:https://panorama.domain/api/?REST_API_TOKEN=hash&type=commit&action=all&cmd=<commit-all><shared-policy><device-group>"Group-Name"</device-gro...

  • 24452 Posts
  • 125 Subscriptions
Top Solution Authors
Top Liked Authors
Labels