General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

Resolved! Behaviour of A-URL subscription in PANOS 8.1

Hi all,Knowing that PAN-DB URL4 license is no longer for sales since last Nov, we have renewed our subscription to A-URL now. After renewal, I can see my other WF, TP licenses have been renewed successfully in Device -> License, however, still showing my PAN-DB license is going to expired in WebUI, and cannot see my A-URL license? Our firewa...
Resolved! Failed to Send Email Reports

Hi Team, We have configured, Email Scheduler for the Daily report, We are tested the email severs communication and the email scheduler communication also fine. But we are not receiving the report, We are receiving the below error in system logs, " Failed to email PDF reports to '[email protected]' for email profile Administrator " Please help me w...

Resolved! RA VPN - SAML testing without affecting production

Is there a way to test SAML authentication for Remote Access without affecting the production environment? In FortiGate I can create multiple independent portals and assign specific users/groups to the portals, but not sure if it is possible in PA. I am a bit concerned about having to ask for long maintenance windows in order to making SAML auth...

Destination NAT & port forwarding not working as expected

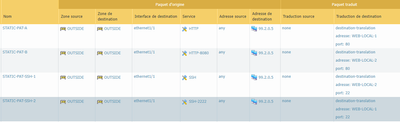
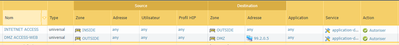
in a lab environment, i'm trying to test destination Nat & port forwarding, i mapped the port 80 to WEB-1 and 8080 to WEB-2.while testing i can access only WEB-1.i did another test where i mapped TCP 22 to WEB-2 and 2222 to WEB-1, i can SSH to WEB-2 as expected but not to WEB-1.you will find the NAT Rule as Security Policy.NAT rules:SECURIT...

NAT RULES.PNG
SEC RULE.PNG
TCP.PNG
calob_IT by • L0 Member
  • 2617 Views
  • 1 replies
  • 0 Likes

Knowledge sharing: Globalprotect troubleshooting/investgation. Split tunnel,Globalprotect app/agent configuration options and etc. to solve issues

Hello to All, Just as a note I have issues with my old community account, to this is why I am using new one for now (Edit: the issue is fixed but I will keep this article under this profile). I had to use several options in the split tunel options to solve VPN issues and I decided to share it. 1.The first issue we had is that some applicatio...

Resolved! JSON parser extractor name with a "-"

I have a JSON list (URL https://ip-ranges.cloud.signiant.com/MediaShuttle) with one part of the JSON path name containing a minus sign ("-"): { "us-east-1": { "all_ips": [ "3.83.158.71", "3.87.14.184", "34.207.126.66", "34.227.155.76", "34.236.155.245", "5...

CURL ERROR: bind failed with errno 97: Address family not supported by protocol

After the customer upgrades the Firewall to version 9.1.10, the following message appears in the System Log, which is not displayed any more. CURL ERROR: bind failed with errno 97: Address family not supported by protocolCURL ERROR: Operation timed out after 60000 milliseconds with 0 out of 0 bytes received Is this what is the reason.

Jay.Yang by • L0 Member
  • 12559 Views
  • 1 replies
  • 0 Likes

Microsoft always on VPN (Windows 10 clients) through Palo Alto

Hi All,We have several Windows 10 clients (3rd Party but using our infrastructure) that need to transit through our PA-3260 to their home network via MS always on vpn. Unfortunately this does not work, we have a very open "any-any" rule in place for these but still they wont connect.Does anybody have any pointers on how to get this to work ?. Re...

Scott64 by • L1 Bithead
  • 7707 Views
  • 3 replies
  • 0 Likes

PPPOE interface - dynamic IP - GP Portal

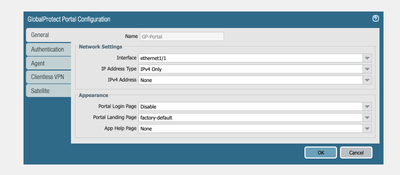
When establishing a connection via PPPOE there is no possibility to select the IP ("None") assigned by ISP in the Global Protect portal configuration, only the interface, which is not sufficient for it to work. I would expect that the IP assigned by ISP is created as an dynamic address object. To make GP work with portal & gateway, I had ...

Bildschirmfoto 2019-01-18 um 00.17.31.png
Bildschirmfoto 2019-01-18 um 00.17.08.png
pan219 by • L2 Linker
  • 16527 Views
  • 7 replies
  • 0 Likes

Resolved! PAN OS 8.1 support after March 1st 2022

Hi All, I see that support for PAN OS 8.1 will end on March 1st 2022 for some Palo Alto platforms. On other Palo Alto platforms, PA-200, PA-500, PA-5000 series and M-100, support for PAN OS 8.1 will continue until their respective hardware EOL dates e.g., 23 October 2023 for the PA-500. I just wanted to double check, that all aspects of PAN OS 8...

Ben-Price by • L4 Transporter
  • 5225 Views
  • 2 replies
  • 0 Likes

Captive portal

Hi Team, please confirm whether in pan-os 10.0 and later do we require SSL-Decryption for captive portal. Is SSL-Decryption is mandatory for Captive portal.

Resolved! Guidance on swinging an Exchange 2016 On-Prem server from ASA to PA 820 (vWired currently)

Hello everyone, currently I've about 3 publicly available servers still running through an old ASA5510 that I would like to move to the PA 820 that we have. 2 of them will be easy as they're basically web servers but its the Exchange server that has me concerned. I'm looking for a guide or some assistance in helping pre-create the security polic...

Knowledge sharing: Containers (Docker, etc.), Kubernetes, Openshift, Palo Alto CN series container firewalls

I hope everyone knows about the Palo Alto Beacon training platform as recently I found a great training about the CN series firewalls as we started needing security in our AWS kubernetes cluster. Palo Alto has youtube videos but they are not enough (Introduction to CN-Series and Demo - YouTube) Beacon – Palo Alto Networks Home : Beacon (palo...

Destination Zone

Hello I found in documentation : "Assign destination zone based on Interface packet would egress from" What is behind this "would" ? How is choose the destination zone , based on FW topology or routing table or ? I have set a route (next hop Tunnel interface) to a subnet and a NAT rule.I have a traffic from 2 differents source zone but same dest...

  • 24463 Posts
  • 125 Subscriptions
Top Solution Authors
Top Liked Authors
Labels