PA 3060
Hello I have A/P cluster PA 3060 with 9.0.9 I want to upgrade to 9.1.11 Can i directly do it ? Or do i have to download 9.1.0 first ? and then download+ install 9.1.11 Is downloading 9.1.0 necessary ?
Our community just got stronger! Explore new identity security resources, connect with experts, and discover more ways to learn and collaborate.
Hello I have A/P cluster PA 3060 with 9.0.9 I want to upgrade to 9.1.11 Can i directly do it ? Or do i have to download 9.1.0 first ? and then download+ install 9.1.11 Is downloading 9.1.0 necessary ?
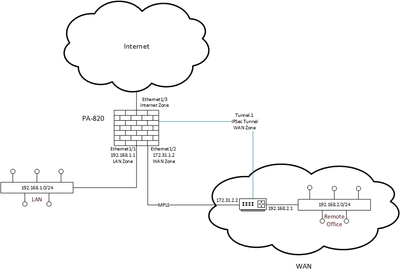
Greetings to allI have the scenario described in the graph: I use Captive Portal based authentication for certain devices. It works fine for the LAN zone, but not for the WAN zone.In the WAN Zone we have remote offices that connect through the MPLS of a service provider. Then, over that data link, we build an IPSec tunnel to establish the connec...
HelloI am using PA VM-50 and wonder if there is any restriction on the number of Layer 2 subinterfaces that I can create under 1 interface. I have more than 50 vlan subinterfaces created and the one I have added recently does not seem to pass traffic. Thanks
Hi, As i have two user ID agent and both are working fine. Iam continuously received this alert on email please suggest
we are getting error: Disk quotas add up to more than 100% while committing any changes in panorama
Hi,We have a PaloAlto firewall which is connected to a Cisco switch and on this Cisco swtich an AP is connected.On the firewall I use ethernet 1/2 port to handle the free wifi clients. This port is in Layer 3 mode.This port is connected with the Cisco switch. The port on the Cisco switch is configured in access mode and in vlan 5.On my AP I set ...
Hello we have a customer with central location acting as Datacenter with PA 3000 series. The panorama also stays in same DC. All the other locations worldwide are connected to central DC over IPSEC tunnels. Most of the firewalls running at remote sites are having 8.x version. We want to upgrade all of them to 10.x . I checked hardware wise all m...
Hello We have an active/passive cluster (PA-820) which we use for IPSec tunnels (with 30 different partners).One of the partners insisted on having a redundant connection using two IPSec tunnels with different peers. So we came up with the idea of enabling ECMP. Based on the routing table, this looks fine (same destination network listed twice, ...
I need to graph GlobalProtect current users + traffic via SNMP. I cannot find anything in SNMPwalk or in the available MIBs.I looked through some older discussions but it seems there is no immediate answer. Any update?Thanks
I'm looking at this document. https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000ClipCACIt says our selected NAT addresses (2.2.2.0/24 on PA-2020 in this case) need to be routed to a tunnel interface, in order for policy lookup to work. Let's imagine I'm using 2.2.2.0/24 on the PA-2020 for NAT'ing traffic not only towards...
Customer updated all devices to latest PANOS version after receiving the email for CVE-2021-3064. However, the PANOS versions for the devices are still showing the older version (8.1.6) in the customer support view. Customer can open each devices and change the PANOS version manually. Cx asks, Shouldn't It update the PANOS version on this view b...
Hi Everyone we got the problem for session end reason “threat”, cause we detected the coin miner traffic through firewall and transmission to internet, even we saw the session end reason already hit to threat when the spyware traffic initially and threat log show result to drop for same session, but the traffic seems like still pass through t...
hello we have a customer with PA220 runing 8.1.8 and they want to upgrade to 10.0.8 I know 10.0 is supported on PA220 but is there any performance issue on PA220 for panOS 10.0.X LIKE slowness etc ? Any guidelines if is it worth to upgrade to 10.0.X for PA 220?
We have taken over an account. I need to move 4 firewalls for our customer from their existing support portal into our support portal. Can someone give me directions here to get started.-Mark
We want to prevent Globalprotect from connecting when user is on the internal network. We have the client set to manual connect/disconnect but users can be stupid and connect anyway.We don't have an internal gateway, and dont want any ssl tunnel when user is on internal network.We tried putting in an ip address of a reachable lan server in the ...
| Subject | Likes |
|---|---|
| 6 Likes | |
| 3 Likes | |
| 1 Like | |
| 1 Like | |
| 1 Like |
| User | Likes Count |
|---|---|
| 6 | |
| 3 | |
| 2 | |
| 2 | |
| 2 |