An interesting POC using Palos
Just watched an interesting way of hiding C2 traffic which bypasses Palos in the demonstration. Would be good to know if there is solution to capture this.https://www.youtube.com/watch?v=eVr0kKdgM2I
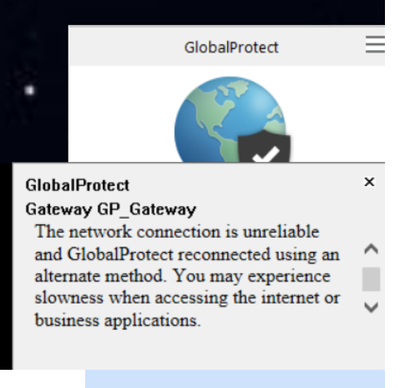
Hi, I have a requirement where two scenario, Branch office and Head Office. ++Branch office has Sophos firewall and Head office have Palo alto firewall.++Branch office users are enforced with using Global Protect when they are outside of the organization that is BO(Work From Home). Which the GP will directly connect with HO.++When the same user ...
Hello, I was given a chunk of IP addresses and domains/urls to update into an existing blacklist on the firewall. I go to objects and create ip-netmask for ip addresses and FQDN objects for domains/urls. Some of the domains i received come in the form of url like "xxxxxx.xxx.com/*" and "https://xxxxxxxx.com/xxxx/xxxx.zip " I decided to create...
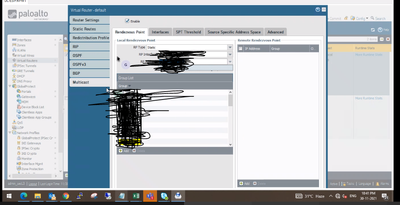
Hi Team, We have already used one interface for RP can we use one more interface to configure RP ??please find below snapshor for reference
I am using Powershell to make API requests to Panorama which cause various commands to be executed on specific NGFWs. I would like to do a commit-all to a specific firewall, not the entire DG/template stack. The documentation Commit-All (paloaltonetworks.com) lists the following command:curl -X GET "https://<panorama>/api/?key=apikey&t...
Hi,I bought a PA-200 new many years ago but support long expired on it. I've been using it simply as a home office firewall since then and have never upgraded PANOS so it's at 4.1.6. Honestly it's running fine, but the old SSL version is forcing me to use old browsers now and really it needs to be upgraded.PA only shows firmware back to versio...
Hello I have several questions to ask you about the user ID.1)We say that the LDAP does not map between the ip and the user, so who does the mapping between the ip and the user name? 2) then, when we configure the mapping of group. I do not understand the mapping of group in what it consists? To associate the name of the user and his ip or to ...
Hi, A question regarding HIP notifications. I have enabled HIP notifications for GP clients connecting in and they trigger when a violation of the HIP profile is detected e.g. firewall turned off, but just wanted to clarify something in the Palo documentation. Palo documentation below seems to indicate that the HIP profile needs to be attached ...
Hello , I have multiple firewall with running PAN-OS 9.1.11 and above version.i am facing an issue to generate XML output command of ARP managment. When i run the ARP managment command to set XML output on i am getting the below error:- admin@PA-VM-Passive> set cli op-command-xml-output on admin@PA-VM-Passive> show arp management Server er...
Hello , we have a customer who renewed the premium partner support When we go to License tab , we can see Premium Partner support renewed But when i go to Support Tab, it still shows date of 2020 Is it cosmetic ? We already tried to fetch the license via cli but same status on support TAB
Anybody know how to configure gre over ipsec ?from the 9.0,pa support gre tunnel and only one word describe about this feature.(Optional) Select Add GRE Encapsulation to enable GRE over IPSec.Add GRE encapsulation in cases where the remote endpoint requires traffic to be encapsulated within a GRE tunnel before IPSec encrypts the traffic. For exa...
I'm running PAN-OS 10.1 on a VM-100. I have DHCP on an interface and use a script to update an address object with the default gateway from the DHCP interface. I have a static route with next hop set to this address object and path monitoring enabled. I've run into a situation where if the DHCP lease expires (something upstream fails with the pr...
Hi all, We are using tunnel monitor on the IPSec tunnels and i am wondering if rekeying childs SA, causes the tunnel monitor to bring the tunnel down. In additon i would like to know if PA stores a log of all the rekeys for each tunnel. TIA
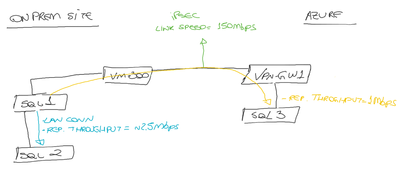
Hi folks, I'm facing some throughput issues with a site to site vpn between my onprem site (vm-300) and azure (VpnGw1).Scenario:- Windows cluster + SQL Always on Availability Groups (async commit)- 2 nodes on premises (sql01 and sql02)- 1 node on azure (sql03).- Link speed 150Mbps- Latency between on prem and azure: 15ms Ipsec tunnel is working,...
| Subject | Likes |
|---|---|
| 1 Like | |
| 1 Like | |
| 1 Like | |
| 1 Like | |
| 1 Like |