Resolved! Error when logged into support account
When i log into palo alto customer support portal, "An unexpected error has occurred. Please contact support" is showing. Tried logging out and logging in.
Our community just got stronger! Explore new identity security resources, connect with experts, and discover more ways to learn and collaborate.
When i log into palo alto customer support portal, "An unexpected error has occurred. Please contact support" is showing. Tried logging out and logging in.
Folks,Our Active-Passive pair takes too long to show the status(i.e. active or passive) when one of the firewall is rebooted. i.e. as of now things are running fine, but if I reboot the passive firewall it will take a very long time to once again come up as passive. It goes through the "not ready" and "initial" stages before getting in the "pass...
Hello everyone, I hope you can help us. We have some users who are connected to global protect, but from time to time, they lose access to the internal resources. When this happens, they have to update the connection in the GP client to be able to access, and when they do this it works, they can access the internal resources. Has this happened t...
We have a process that sends MSSQL (1433/tcp) to a cloud service that occasionally just stops working - so trust to untrust. It is mostly on 'larger' data transmissions. Turned off all the flood protection in the zone protection profile on the outside interface, and there is no issue. Can I see where that is being triggered? Any thoughts on chan...
I used to be able to make changes to objects (address/groups/application groups) ect. But now when I made the change I have to go through my policies and NATs and update them manually. Any ideas? Is there an update object option that I'm not aware of?
Hello All - I am fundamentally not understanding the difference between Template and Device Group. Using teamplate i can push a policy to multiple Firewalls. Looks Device Group also does the same thing. What is the difference, and use case. When to use template and on what scenario i have to use Device Group? Thanks RB
Hello, I am totally new to Palo Alto and trying to set up VPN connection from Android Strongswan VPN Client app to Palo Alto without GlobalProtect. I have requirement so client's IP is unknown and can be any public IP. At the moment IPSec tunnel is UP but I always setting error on client side: "setting up TUN device failed, no virtual IP found...
No blocks observed but US gateways are dropping the traffic going to ohio.gov were as the UK gateway it works. The logs do not show any blocks. Any ideas how to troubleshoot would be helpful. Opened a TAC case however its dragging out for 3 days now
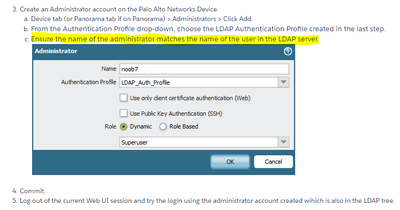
Hi All, Why do we need step 3 mentioned in the KB below for the WB UI authentication with LDAP?:https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000ClGuCAK Why do we need to create a local user? Won't Palo be an LDAP proxy (grabbing username/password and verifying it against LDAP server database)?
Is it possible to export all Certificates at once from a Palo Alto Firewall via API? Without having to pass the names of the certificates from the API call, because in the documentation I've only seen it possible that way.
Hello. I've been trying to use PVLAN with palo alto. I have two isolated host which are on the same subnet and wanted them to communicate through palo alto. I was able to manage with a switch using local proxy arp but from what I've searched palo alto doesn't have that feature. I see the arp packets from host A going to palo alto but since the d...
My PA-450R did not come with a power supply and has the phoenix connectors for connecting power to it. Is the an off the shelf power supply that is recommended for this unit or will I need to supply my own power?
Hi there, Has anyone noticed an increase in false positives with Unique Threat ID 85253 since the update 8971 (2025-04-28 UTC)? We are experiencing a rise in false positives but haven't opened a ticket yet. Thanks, Daniel
Hello! I may be trying to do something impossible, but it seems like the configuration elements are all there. We have a static default route to our ISP that is set with path monitoring so that we failover to a backup route when the gateway is unreachable. We are trying to figure out a way to be emailed when the path monitor fails. I have ...
Hi all, while using ECMP for the last 2 years without any issues using 3 ISP's with different weight and enabling Symmetric Return and Strict Source Path, I found that some sites with authentication access and Proofpoint secure emails access are being timed out because of their sensitivity of the source ISP change during the session. In most of...
| Subject | Likes |
|---|---|
| 6 Likes | |
| 4 Likes | |
| 2 Likes | |
| 1 Like | |
| 1 Like |
| User | Likes Count |
|---|---|
| 6 | |
| 4 | |
| 2 | |
| 2 | |
| 2 |