GlobalProtect Discussions
GlobalProtect discussions offers topics about our network security for endpoints that protects your organization's mobile workforce. This area is dedicated to GlobalProtect discussions to help you answer questions.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
GlobalProtect Discussions
GlobalProtect discussions offers topics about our network security for endpoints that protects your organization's mobile workforce. This area is dedicated to GlobalProtect discussions to help you answer questions.
About GlobalProtect Discussions
Welcome to the GlobalProtect discussion area! Here, you can engage in conversations about GlobalProtect, explore new insights, and stay updated on ongoing discussions. Check back regularly for the latest updates and community insights on GlobalProtect.

Discussions

GlobalProtect keeps re-authenticating automatically

We need GlobalProtect setup with DUO via RADIUS and we need the user to have to manually re-auth after 11 hours. We have struggling to get this to work. Login Lifetime or Cookie Auth Expiration both automatically re-auth the user even when GlobalProtect is set to On-Demand and set to not remember username and password. (The biggest issue with th...
See the users version of Global Protect in Panorama

I am getting ready to test upgrading GlobalProtect using the "Allow Transparently" option of the upgrade for a small subset of users. I want to verify the upgrade worked from Panorama without reaching out to the user for verification that it worked. I can't seem to locate where I would see the user's client version for GP in Panorama. My initial...

Bo_Olsen by • L0 Member
  • 12915 Views
  • 3 replies
  • 0 Likes

Creating self signed Certificate for IOS device 14 and 15 on Palo Alto firewall

Hi Folks, Our GP VPN Portal and Gateway Certificate had expired recently. When we created an new self signed certificate on Palo Alto firewall and mapped it to GP VPN Portal and Gateway. We are able to connect to portal and Gateway and it is working fine for windows and Android device. But when we try to connect to GP Portal through IOS device ...

Resolved! Global Protect install error on Surface X with SQ2 processor

Trying to install Global Protect on a new Surface X Pro and run into the below error. "This installation package is not supported by this processor type. Contact your Product Vendor"Its a Surface Pro X with Windows 10 64Bit SQ2 processor. Tried installing GlobalProtect64-5.2.5-c84, 5.25, and 5.18 all give me the same error message.

GlobalProtect iOS Certificate issue

Hello, I’m in the middle of trying to make a gateway for iOS devices and I’m having an issue. I use MobileIron to push out the config and it uses an MI SCEP cert; I’ve added the MI SCEP CA to the PAN device and set it up as the auth profile. If I only do UN/PW I have no issue but as soon as I add cert requirement, the iPhone GP app has an erro...

COlson by • L2 Linker
  • 2898 Views
  • 1 replies
  • 0 Likes

Issues using Elliptic Curve DSA certificates with GlobalProtect agent

Anyone else come across this? Anyone using ECDSA certs for their GlobalProtect Portal or Gateways? Have you tried non-Windows/MacOS clients? Configuring GlobalProtect Gateways to use ECDSA certs instead of RSA certs breaks everything except Windows, MacOS, and mobile agents. As the SSL cert industry seems to be heading toward deprecating RSA c...

fjwcash by • L4 Transporter
  • 7719 Views
  • 4 replies
  • 0 Likes

GP Issue Gateway Fake

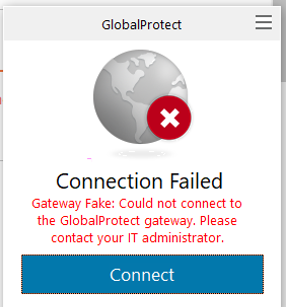
Hi, I am facing the issue with Pan GP where I get an error Gateway Fake: Could not connect to the GlobalProtect gateway. Please contact your IT administrator.I tried to remove the certificate and also reinstall it multiple times and delete the Palo alto network file also and re-install the Pan GP but no luck. Uninstall all applications but no so...

chanderjain_0-1638027354282.png

Does enforce users to connect GP option works with internal host detection?

We want to enforce users to connect GP when they are outside of the network. But when they use their same machine in internet network, this option should get disabled.Can I solve this problem using internal host detection (internal GP gateway) ? If yes , there should not be ip-user-mapping by GP in internal network .

Deepak25 by • L3 Networker
  • 2284 Views
  • 1 replies
  • 0 Likes

Connecting via a RDP connection drops RDP and VPN connection

We have a server that runs some automated processes. These processes requires that Global Protect be connected. When I RDP into the server and then connect the VPN on the server, the RDP session is temporarily disconnected. When it reconnects the VPN is no longer connected. I can't seem to keep both connections at once.

JAMF Upgrade broke HIP report

Greeting All.JAMF Cloud did an upgrade this morning. This update caused the jamf client binary to be updated on my computers.After the jamf client upgrade GlobalProtect no longer shows JAMF (Casper) in the hip report.Tested GP version 5.2.5 & 6.Has anyone else experienced this issue?

JasonBTR by • L1 Bithead
  • 5547 Views
  • 5 replies
  • 0 Likes

Resolved! Strange issue with GlobalProtect Wi-fi vs Ethernet

Hi Everyone, I need your help as I'm facing a very strange issue with GlobalProtect, the VPN used in my company.When I'm working from home I switch on my PC which is already connected to an ethernet cable: GlobalProtect connects almost immediately (usually to Europe Primary) and I'm able to access my company network drives, folders and remote de...

Capture_VPN_Ethernet.PNG
Capture_VPN_WiFi.PNG
Capture_VPN_WiFi_then_Ethernet.PNG
  • 1711 Posts
  • 68 Subscriptions
Top Solution Authors
Labels



