VM-Series in the Public Cloud
The VM-Series is the virtualized form factor of the next-generation firewall. Use this discussion as a resource to discuss VM-Series deployments across public clouds like AWS, Microsoft Azure, Google Cloud Platform, Oracle Cloud, and Alibaba.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
VM-Series in the Public Cloud
The VM-Series is the virtualized form factor of the next-generation firewall. Use this discussion as a resource to discuss VM-Series deployments across public clouds like AWS, Microsoft Azure, Google Cloud Platform, Oracle Cloud, and Alibaba.
About VM-Series in the Public Cloud

Welcome to the VM-Series in the Public Cloud discussion forum! This community exists as a resource for you to discuss VM-Series deployments on AWS, Microsoft Azure, Google Cloud Platform, Oracle Cloud and Alibaba. We encourage you to engage in this rapidly growing community to share ideas, pose questions, and propose real-world solutions to any challenges that may arise.

Disclaimer:
This forum is provided for Live Community members to discuss and share information pertaining to the VM-Series deployments on AWS, Microsoft Azure, Google Cloud Platform Oracle Cloud and Alibaba. Please use the information from this forum at your own risk and make sure to test and verify proposed solutions presented here. For information on contacting Palo Alto Networks support, click here.

Discussions

Welcome to the VM-Series in the Public Cloud Discussions!

To make this forum valuable and enjoyable for everyone, please review the following guidelines before participating: Rules and Best Practices Be Respectful: Treat fellow community members with professionalism and courtesy. Constructive discussions are encouraged; disrespectful or inflammatory comments are not. Stay On-Topic: This board is d...
JayGolf by • Community Team Member
  • 3737 Views
  • 0 replies
  • 0 Likes

Azure ALB sandwich with vm-series

Dear Team, I am aware that Sandwich deployments are possible on AWS. I would like to know if Sandwich configuration is possible on Azure as well. Azure knows that only one load balancer is connected. If anyone has a successful sandwich configuration, please let me know. I would appreciate it if you could share any related documents. ...

VM Series Licensing Methods

Hi Team, I have an doubt regrds the BYOL and PAY AS YOU GO methods in VM series. First can i use the credits in both the methods BYOL PAYG? If yes than how we can use it Second as per my understanding the BYOL require the auth code from the Customer support portal utilizing credits first ? for example if i buy 100 creds so i need to done ...

Resolved! VM-Series bootstrap in AWS - content packages not getting installed

Hi everyone, I am currently trying to register a newly created VM-Series firewall to Panorama.The bootstrap process is working and the firewall can register to Panorama, nevertheless, it cannot apply the configuration pushed by Panorama since the content update packages are not installed and therefore some objects like EDLs from Palo Alto are no...

VM Series in Azure Active/Active

Hi I would like to have this configuration (see picture) for both inbound, outbound and east west and on prem via vpn and expressroute Is that the best solution to achieve this? are all the firewalls active active? I cannot find documentation on setup of this active / active Thanks

Screen Shot 2024-02-08 at 13.18.23 PM.png
kalledog by • L0 Member
  • 2440 Views
  • 2 replies
  • 0 Likes

Resolved! Clarity on Overlay routing with GWLB for Combined (Centralized Egress + Distributed Ingress) deployment model

Hi, I am looking for some clarity on the Overlay routing feature on VM Series FW. I am using the Combined (Centralized Egress + Distributed Ingress) deployment model described in this Securing Application in AWS - Centralized Model Deployment Guide. In this pattern, overlay routing is enabled so that the FW can handle both inspection and NAT...

Screenshot 2024-02-04 at 1.31.23 PM.png

Hub and Spoke VPN

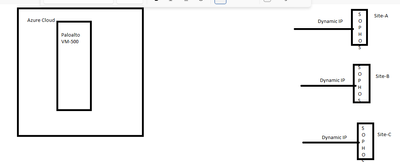
Hello, We have one PA firewall in azure cloud and rest we have Sophos on Mutiple sites with Dynamic IP's We want to configure Hub and spoke VPN. with all sophos means PA site is Hub and rest of the site Spoke we dont want mutiple tunnel of each and every site. Request will come from the peer site with dynamic IP's is this configuration is pos...

jhussain1_0-1706876545946.png

Azure PA HA DNS

Hello community 🙂I'm running an v9.1.x Active\Passive cluster on Azure and we had several problems with the "quick" failover.Because I need the firewall(s) to perform DNS resolution on internal fqdn objects I had them configured with private DNS servers running on Azure VMs. While digging in to the failover issue I observed that the new active ...

AWS Reference Architecture, Subnet Sizes and Automation

1. The AWS Reference Architectures (AWS - Palo Alto Networks) and associated automation libraries all use a /16 CIDR for the Security VPC and a /24 for each subnet - including those for the TGW attachments and GWLB endpoints. AWS recommend deploying these resources in the smallest subnet available, a /28 - as they use a single IP and should not ...

mb_equate by • L3 Networker
  • 4068 Views
  • 1 replies
  • 0 Likes

Paloalto GWLB cluster IPsec tunnels with on-prem

Dear Team, I want to deploy Paloalto 2 - VM-300 with integration of GWLB on AWS. both will be active and passing the traffic. However i have referred Paloalto documents with two-arm mode and one-arm mode. I will be having an IPsec connectivity with (on-prem DC) in this case, how this will work ? on prem user >>> IPsec >>&...

Unable to access the web end point when the VM series is deployed in Azure availibility zones

Hi Team, I initially deployed firewall VM series in no zones. Created each VM with the 3 interfaces(Management with public ip address), when It is deployed in no zones, I am able to access the web endpoint using public ip of the mgmt public IP. however, I am not able to access the web interface of the firewall when I deploy VMs series in av...

Capture.PNG
image (3).png

Resolved! Sub Interfaces or VLAN interfaces supported on VM-300 in AWS?

Hi, We were wondering if sub-interfaces or VLAN interfaces are supported on the VM seriies in AWS. We would like to separate customer traffic using these VLANs/ sub-interfaces as we do in our own DC, but it doesn't seem possible in AWS on the VM-300 as there are no options when I highlight the individual interface. If sub-interfaces and VLANs a...

pmchenry by • L0 Member
  • 10175 Views
  • 6 replies
  • 0 Likes

GCP VPC Peering

Hi, We are deploying PA VM in GCP (Common Firewall Deployment Architecture). Deployment Architecture is attached. In Trust VPC we have configured Internal Load Balance (TCP), Created VPC Peering between Trust VPC & Web VPC. From Trust VPC Instance (VM) we are able to ping Web VPC Instance (VM) & Vice Versa. Web VPC Default route is...

Resolved! IKEv2 IKE SA negotiation is failed as responder, non-rekey. Failed SA

I am not sure why am I getting this IKEv2 IKE SA negotiation is failed as responder, non-rekey. Failed SA error when my custome is trying to send traffic to my VM-100 via IPSEC tunnel. This was working until yesterday but suddenly it stopped working since morning. There isn't any changes happened on both sides. Attached logs. ====> Failed SA...

kshukla by • L1 Bithead
  • 165479 Views
  • 9 replies
  • 2 Likes
  • 536 Posts
  • 107 Subscriptions
Top Liked Authors
Labels