General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Announcements
Scheduled Maintenance: November 14–15 (starting Nov. 14 at 12:00 AM PST)
LIVEcommunity will temporarily operate in read-only mode as we prepare to welcome Idira!
Public content will remain accessible, but log-ins, posting and community interactions will be paused during this period. Thank you for your patience!
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

Resolved! Whitelisting IP Addresses

I am trying to whitelist some IP addresses. I added the IPs to our allow policy in the URL category section. Is there anything else that I should be doing? The purpose of this is to allow our printer providers servers so our printers can communicate with their servers. Thank you!
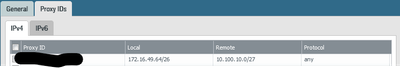
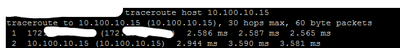
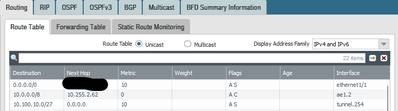
Prioritize Tunnel Static Route over L2 physical route

Hi, I have an IPSec Tunnel between a remote central site and a PA-220. This tunnel advertises it's remote internal network in 10.100.10.0/27. A static route has been created in the PA with a metric > 1 (10), to route traffic in direction of 10.100.10.0/27, through the IPSec tunnel interface, tun.254. This route is effectively worki...

PA-1.png
pa3.png
pa-2.png

Resolved! Aggregate Interface with sub-interface

Dear all, I am designing a new network for a client and they have lots of zones. my idea is to create an aggregate interface (ae1) and create sub-interfaces for the individual zone. I read aggregate interface can be done on SD-WAN level and could not find any documents related to my design (Not SD-WAN). However, I found this post https://live....

Shadow by • L2 Linker
  • 7146 Views
  • 2 replies
  • 0 Likes

Civil3D 2023 and Global Protect

Greetings Programs, We have a client that is an engineering firm. They have a few remote engineers and we are starting to see issues with Civil3D 2023(AutoCAD). Majority of these end users have Windows 11 OS with Global Protect installed on it to VPN into the office to access a network shared drive. When the end users open Civil3D 2023 (AutoCA...

EDraper by • L0 Member
  • 2208 Views
  • 1 replies
  • 0 Likes

FQDN object not resolved

Hi, We have this fqdn object created: 2021-01-08 12:26:14.872 +0100 dnscfgmod: Fqdn SIEMENS OWNCLOUD SERVER/cco.siemens.com could not be resolved If i run a ping from MGMT A interface is resolving:ping host cco.siemens.comPING cco.siemens.com (212.231.11.154) 56(84) bytes of data. The DNS is OK, reachable, and resolving. If i go to the web and c...

dns.JPG
BigPalo by • L4 Transporter
  • 5281 Views
  • 4 replies
  • 0 Likes

Panorama stop showing logs suddenly

Hi, We have a panorama M100. Panorama is showing logs but suddenly stop doing it. We can not see any logs until we restart logd proccess or appliance. Panorama version is 8.0.8 Why is this happening?

Resolved! Recommended action for real-time-detection URL category

Can you please help me clarify the new real-time-detection category, which is covered by the URL filtering license? According to the article the Advanced URL filtering "real-time-detection" URL category is not a classification by itself, but a real time inspection, which can return either Benign or as one of the risky category types, e.g. Pa...

batd2 by • L4 Transporter
  • 13696 Views
  • 6 replies
  • 1 Likes

Resolved! User resetting expired password through Global Protect

Is a user able to update their password (when its expired or a force change is required) in Global Protect when using SAML Azure AD authentication? There is this older document saying its possible when using Radius with PEAP-MSCHAPv2 authentication but I'm wondering about SAML. Expired Active Directory Password Change for Remote Users (paloalt...

Claw4609 by • L5 Sessionator
  • 23287 Views
  • 1 replies
  • 0 Likes

Root certificate install

If I install a new certificate why does the root certificate have to be installed as well with it (well that is what I saw on a demo) ? I thought the root certificate was needed more on the client side or other firewall connecting to the one I'm referring to. I may be misunderstanding something. Also I will be requesting new certificates to r...

Cortex XDR on mobile phone

Hi all, I am running Cortex XDR and when I click on the all end points, I can see the endpoint device like PC and server. I have install the endpoint agent on those PC and server. They are Domain joined PC and server. How can I install this Cortex XDR agent on mobile phone? and second question is can we install cortex XDR on home PC which is not...

lprasad by • L1 Bithead
  • 4586 Views
  • 5 replies
  • 0 Likes

Resolved! PA-220 Reboot

Hi Team, Firewall got rebooted instead of generating a tech support file can we do any other troubleshooting to check why the firewall was rebooted. If i generate the tech support file i have to go to Palo to check what it is and wait till i get the response. Instead, if I can check few commands, it will be better. In Cisco ASAs we can analyze...

Resolved! PA 500 Cisco 3560

Hi there, I am totally new here in Paloalto firewall. I have PA 500 and want to do lab test and I want to find a basic instruction to set up PA to connect internet and also connect to Cisco switch. I am very familiar with Cisco ASA and switch since we do all CLI but I understand PA firewall is all GUI. Any help I would be appreciate. My unders...

phugiay by • L2 Linker
  • 9987 Views
  • 13 replies
  • 0 Likes

Resolved! IPSEC Tunnel to ASA - PeerID issues

I am setting up an IPSec tunnel to an ASA. I am getting an error message about the PEERID type only allowing IP but received FQDN. Per the other KB article, I changed the PAN Exchange mode to Aggressive. Now the PAN received a FQDN of the ASA side and gave listed the FQDN in the system logs.My question.. where in the ASA can you configure PEER a...

SDorsey by • L4 Transporter
  • 8788 Views
  • 5 replies
  • 1 Likes
  • 24482 Posts
  • 125 Subscriptions
Top Solution Authors
Labels