RFC1918
Basic trust to untrust policy I see internal address sending snmp to addresses like 10.0.0.1, 192.168.1.x. Do people create a policy to block internal traffic going to RFC1918 on the untrusted interface?
Hi Guys, I was trying to add Peap-MSchapV2 for our Radius Authentication for Management Interface. I configured Radius Server Profile with PAP with Windows NPS, seems everything is working fine. And then I generate a new Certificate Signing request and signed by Organisations CA server, and downloaded the intermediate certificate etc and u...
Prerequisites Currently, user has two admin accounts. Default local admin account(Superuser) New local admin account synchronized with Cisco Duo(Superuser) End user has to consider how to treat “Default local admin account”. As a result of consideration, the following items are the options to deal with it: Option1: To make “Default local admi...
Looking for suggestions of how others track config changes: who made the change and what changed; similar to config audit but for every change made over time. The goal is training and accountability. I’m aware of Rancid, which may or may not work as it’s intended for Cisco configs, and looks to only provide diff output. Syslog is an option but...
So, this morning, all going swell. P1. Hm, okay. Looks like an application issue, SQL related. Nothing on the firewall or policies were touched. The policy is using Layer 7 App-ID MS-SQL to get a server to communicate with the MSSQL server over TCP-1433. At the end of the day I had an idea to remove protect profiles and drop from Layer7 to L...
Hi, We have a new deployment of Panorama using Datalake storage. Log data from the firewalls is successfully coming through to Panorama, however, there is no "Apps Seen" or info shown for apps under Policy Optimizer. Rule Usage data is available, and the app data is shown correctly on the local firewalls. Setup > Management > Policy Ruleba...
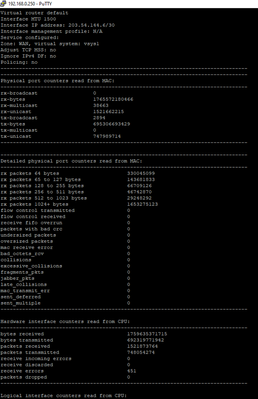
Hi, My monitoring system is detecting packet loss on my panorama device. When pinging the DG there is no packet loss. When checked the interface stats on the cli I can see the below. admin@MANPANORAMA01(primary-active)> show interface management -------------------------------------------------------------------------------Name: Management ...
Is there any place that I can put in an IP address and see if it is on an external dynamic list somewhere? Going to this site:https://docs.paloaltonetworks.com/resources/edl-hosting-service and clicking around hoping to hit the right one (such as Azure > Public Cloud) and then having to go through each cider is brutal and time consuming.
Hi, I am migrating WatchGuard to Palo and there seems to be a lot more configuration options on the Palo. WatchGuard configuration is below. What is the best way to configure this within Palo? Where is the option to set default-originate? router bgp 64801bgp router-id 169.254.3.3timers bgp 4 12neighbor 10.200.34.2 remote-as 64601neighbor 10...
While installing cortex agent in windows 7 ver 6.1 getting compatibility error Checked windows 7 version was 6.1 64bit operating system Checked all the windows patches checked .Net Framework is enabled have tried installing older version as well as new but still getting same error. Any solutions for these
Hi Guys. Recently we changed the slow internet provider to a faster one with 100/100 (up/down load). It was changed on the same interface of the FW. ( Eth1/2- same for the old and the new service provider) Ever since the change, the download is intermittent or the download freezes. Below is the detail session view of the session when the downloa...
I'm having trouble figuring out what expression to use(in a Custom URL Category) to match any variation of HTTP requests for an entire website. For example, I want a single expression to be able to match/block/permit the following HTTP requests... example.com/ example.com/path abc.example.com/ abc.example.com/path xyz.abc.example.com/ xyc.abc....
For some odd reason the firewall is not resolving external fqdn's that are part of an Address groups..
I get SSO errors whenever I try to go to any PaloAlto site besides Live and support.paloaltonetworks.com. I went to open a ticket to have the problem solved, but I am unable to do so due to an SSO error. How am I supposed to go about getting support for this?
Dear Sir, Asper our dictation we install two Palo alto PA440 box in CESC office and for registration we create a account username: ********* and Password: *********** and it create successfully. But when we try to support portal by using the account details it display (UnAuthorized Access /Your membership has expired or has not been approved, p...
| Subject | Likes |
|---|---|
| 2 Likes | |
| 2 Likes | |
| 2 Likes | |
| 1 Like | |
| 1 Like |





