Resolved! exchange 2016 exclusions
HiIs it possible to install cortex XDR on an exchange 2016 server?Do I need to make any exceptions before I install the traps? Cortex XDR Thank you
hi, is there any module or convertor that can allow using SFP as etherent and what exact part number of it please?
Target is to forward the PA device status to a monitoring tool (Cacti). But "Cacti" respond SNMP error. Both v2 and v3 show the same error. Other devices (C2960) from the same subnet of PA has no problem. Below is the PA settingsSNMPv3Name: TestSNMP Manager: <IP_of_Cacti>User: testuserEngineID: <leave_blank> (I have 2 PA form an HA)A...
What is the difference between the control plane and management plane? Or are the the same thing?
Hi All, We are trying to downgrade from 10.0.6 to 9.1.15. After we downgrade to 10.0.0 first , the auto commit have error. It mention failed to commit policy to device. Do anyone have go through the same problem? My suggestion is we just downgrade to 9.1.15 since we already in base version 10.0.
Hi,I will be upgrading my 3050 firewall (managed by panorama) to a 3250 soon and am curious if there are any best practices guides out there moving from a 3050 to a 3250? Thanks!
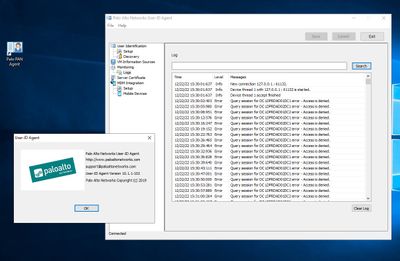
We've noticed errors in the Monitoring logs of our Windows servers running the PAN Agent ID software. The User ID is working fine but the error is continually filling the logs. (error screenshot attached) PAN o/s 10.1.6 h3 and the Agent ID version is 10.1.1-102. useridd.log ========== 2022-12-21 08:38:10.822 +0000 Error: pan_ssl_conn_ope...
Hi All, Same session id, see 37 entries in threat log at 9:28 and only 1 entry in traffic log at 11:16Session ended reason is tcp-rst-from-client There is a threat log before there is a traffic logHow to explain such a long time difference? Does anyone know what's going on? thanks
Dear Team, If I look at the bottom of the dashboard, I can see 'session expire time'. I think that option refers to the last time I logged out. But the date info doesn't seem to fit I would like to know what the setting is and why the time is not correct. If anyone has any information or related documents that they know about this, I ...
Dear and valuable Live Community Members, One of our customers came to us with some questions in regard to the issues he is facing to correlate the logs for DNS Sinkhole, and we are wondering if there is a solution to it. The customer currently has the following situation:• Rule ‘DNS_Service’: this rule will allow DNS traffic from the FSMA I...
Hi All, We will doing a RMA replacement for PA-3220. The faulty unit is cannot access anymore from GUI or CLI and it's managed from Panorama. We only have the backup configuration and not the device state. So, what we should? 1)Do we replace the fault unit with the new one, configure the HA with the active unit and replace the S/N in the firew...
We received following alert:-----domain: 1...eventid: tls-X509-validation-failedobject:fmt: 0id: 0module: generalseverity: highopaque: Public Cloud Server certificate validation failed. Dest Addr: panos.wildfire.paloaltonetworks.com, Reason: unable to get local issuer certificate We don't use decryption policy.We need assistance to resolve this...
Basic trust to untrust policy I see internal address sending snmp to addresses like 10.0.0.1, 192.168.1.x. Do people create a policy to block internal traffic going to RFC1918 on the untrusted interface?
Hi Guys, I was trying to add Peap-MSchapV2 for our Radius Authentication for Management Interface. I configured Radius Server Profile with PAP with Windows NPS, seems everything is working fine. And then I generate a new Certificate Signing request and signed by Organisations CA server, and downloaded the intermediate certificate etc and u...
Prerequisites Currently, user has two admin accounts. Default local admin account(Superuser) New local admin account synchronized with Cisco Duo(Superuser) End user has to consider how to treat “Default local admin account”. As a result of consideration, the following items are the options to deal with it: Option1: To make “Default local admi...
| Subject | Likes |
|---|---|
| 2 Likes | |
| 2 Likes | |
| 2 Likes | |
| 1 Like | |
| 1 Like |





