General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

FQDN security in policy

Hi All, I am quite new to palo alto. can anyone explain me what happened if we configured object as a FQDN, IP and URL..I have created one security policy where I have implemented destination as a FQDN (nslookup results into 1 IP address) but user is reporting that it's not working..For that, FQDN default TTL is 5 mins, refresh time is 6 hours.....

Resolved! PAN-OS 8.1.0 SMB Issues

Hello all, Please be advised, there is a current issue with PAN-OS 8.1 which seems to break anything SMB related, e.g. mapped network drives. Sessions have an end reason of "resources-unavailable" and go into state "Discard" in the session table. Upon speaking with a TAC engineer, this is a known issue and they are working towards a fix. Edit: T...

QoS and IPSec

Hi All, I would like to enable QoS on an IPSec tunnel. The tunnel is carrying mostly voice and signalling traffic.If the voice traffic has a marking, eg EF, will this marking be copied to the outer IP header (the IPSec tunnel header)? Or, will I have to create a separate QoS policy, which prioritises IPSec traffic as it egresses the physical int...

Luke_R by • L2 Linker
  • 2145 Views
  • 1 replies
  • 0 Likes

After Apply SELF-SIGNED ECDSA CERTIFICATE IN SSL/TLS PROFILE Cannot Access to Management Interface

I have a HA Firewall Active/Passive. Due to certificate is already expired I have exactly follow below guide to create my Self Sign ECDSA Certificate and apply it to my Passive firewall. The issue is when the passive firewall is in HA mode that time I`m unable to access to the management interface. When I make it as standalone mode that time the...

JiaXiang by • L4 Transporter
  • 2921 Views
  • 1 replies
  • 0 Likes

Resolved! Expedition: Export - Base Configuration Output

Export in base configuration output screen Device-Groups does not show arrows to expand organizational groups and sub groups. When trying to import from Panorama 10.0.Currently running Ubuntu 16.04.6 and the Expedition shows 1.2.15 but had error messages when performed the install but it seems to work. Does any know how to fix the device group n...

Gol4 by • L0 Member
  • 2582 Views
  • 1 replies
  • 0 Likes

PA Firewall Performance Chart

Spoiler (Highlight to read)Looking at the comparison chart, if I was interested in the 3430 and I use SSL decryption, threat prevention\wildfire\URL filtering and IPSEC vpn does that mean I would get roughly 9/2 Gbps or 12.2 Gbps?Looking at the comparison chart, if I was interested in the 3430 and I use SSL decryption, threat prevention\wildfire...

roma_0-1648500614096.png
roma by • L2 Linker
  • 2121 Views
  • 1 replies
  • 0 Likes

WMI On server 2022 for USER-ID

Hi There, Have a pair of PA-3220s. User-ID was working swimmingly. Recently upgraded our DCs to Windows Server 2022 and WMI is routinely failing and showing "Not connected" under server monitor. Doing some reading on WMI and Server 2022, and it sounds like Microsoft did something under the hood in 2022 that required updates or changes from 3rd p...

kaumell by • L0 Member
  • 4328 Views
  • 1 replies
  • 0 Likes

Resolved! SSL certificate for passive firewall

There is an active passive pair having SSL certificate (management only) with different CNAMES (its own management IP). While the CSR generation and certificate import (signed by ECA) is successful on active peer, the CSR generated on passive peer is getting erased whenever commit is done from active peer. How to generate CSR and install SSL cer...

Resolved! IPSEC VPN - app-id

Hello all,We have a software ipsec connection that will be between an inside server and a server in the cloud. The PA will just be a pass through so to speak, (nating and security rule).The ipsec requires UDP 500 and 4500 and the IP 50 protocol. Do you know which app-id's I'll need for that?The palo has these 4 app-id's:ike tcp/500, udp/500ipsec...

roma by • L2 Linker
  • 7325 Views
  • 2 replies
  • 0 Likes

PA-5200 MIB file for SNMPv3 need them for monitoring

PA-5200 MIB file for SNMPv3 I need them for monitoring I find them here:https://docs.paloaltonetworks.com/resources/snmp-mib-files.htmlbut the file type is .md5 and .my, but I need file type .mib or .smi to work in the monitoring software. Where I can get those files for PAN-OS 10.1

Bulk way to search logs for many IPs?

I have a list of over a 100 IP addresses that I would like to search logs to see if there has been any activity. Is there a way to search the logs files by feeding the FW a file containing the IP addresses? Thank you.

ccfritz by • L1 Bithead
  • 3418 Views
  • 1 replies
  • 0 Likes

Resolved! using Azure MFA with Global Protect

Hello, To configure Global Protect to use our already Existing MS MFA server, I followed this KB: https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000ClkkCAC I think I had to do one or two extra things as well, but in any case it's working. However, it only prompts for the second factor if after I disconnect the Global Pr...

Extending Eval license

Hi there, My Eval Request is going to be expired soon, and I'd like to extend it for another 60 days but I don't know how? Could someone please advise me how to extend my Palo Alto Eval license ? As I can't see any options in Palo Alto portal for license extension.Thanks

AK74 by • L2 Linker
  • 3464 Views
  • 1 replies
  • 0 Likes

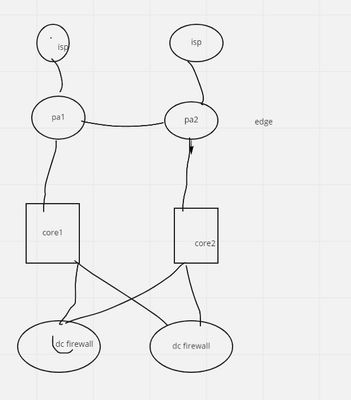
design help

Hi all , I have the above topology , Now the question where should iI keep the dmz zone on edge firewall or dc firewall Thanks

pa dmz.JPG
simsim by • L4 Transporter
  • 1931 Views
  • 1 replies
  • 0 Likes
  • 24479 Posts
  • 125 Subscriptions
Top Solution Authors
Labels





