General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Announcements
Scheduled Maintenance: November 14–15 (starting Nov. 14 at 12:00 AM PST)
LIVEcommunity will temporarily operate in read-only mode as we prepare to welcome Idira!
Public content will remain accessible, but log-ins, posting and community interactions will be paused during this period. Thank you for your patience!
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

Resolved! Upgrade Minemeld Ubuntu 16.04 to 18.04

I tried a do-release upgrade on Ubuntu 16.04 LTS and it took me to 18.04 LTS without issue. However minemeld says "Bad gateway" when I try to log into it. I tried to check for updates and figured maybe the source would be changed from xenial-minemeld main to bionic-minemeld main ie)deb HTTP://minemeld-updates.panw.io/ubuntu bionic-minemeld mai...

ksauer507 by • L3 Networker
  • 3722 Views
  • 2 replies
  • 0 Likes

Resolved! Syntax for security policies without security profile

Hi all, in my security policies on a PA-firewall (or in panorama) I want to be able to filter out all the security policies which have no security profile(s) . I tried a few combinations in the line of (profile-setting/profiles eq 'none') but alas, no joy 😕 Is it even possible?

KenVaBr by • L1 Bithead
  • 3940 Views
  • 1 replies
  • 0 Likes

macOS Big Sur 11.6.2 - Global Protect 5.2.8-23 - Connected but Internet is not actually working

Hello all,I received from work a MacBook Pro with macOS Big Sur 11.6.2, I've installed the GlobalProtect 5.2.8-23 which is the only one that I had access to, and it seems like whenever I connect the GP, the connection is successful but there is no Internet Connection.As soon as I disconnect the GP, everything is working.I searched on the live co...

alberaru by • L0 Member
  • 2553 Views
  • 1 replies
  • 0 Likes

Blocking Torch browser

Hi All, I would really appreciate if some one can help me on this. I am planning to block Torch browser through a firewall rule, using App-ID. But as per information in the community we cannot entirely block the functionality of Torch browser using App-ID. Once we block from the security rule, normal web traffic will go through the firewall. Ple...

Log Forwarding

Hello everyone, Before the question, the context.I have a panorama wich managed a lot of devices groups. we have a lot of rules for them. Which all these rules uses the default profile for log forwarding.I have a new syslog server and i need to forward the logs from all the devices and not from panorama. I created the new syslog server and i man...

Maryan by • L0 Member
  • 3431 Views
  • 3 replies
  • 0 Likes

Custom Vulnerability Signature to block older versions of Chrome

After reviewing this KB article: https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000ClSOCA0 It looks like you can create custom vulnerability signatures for named browsers. Could you also do that to limit browser access via a security policy based on a minimum version number? For example: create a vulnerability signature...

Match next line at cli

Is there a way to match the next "X" number of lines when piping to match at the cli?I am entering:show zone-protection zone outside | match udpand would like to show the matched line and the next three.This would be analogous to grep -A 3Cheers!

Resolved! Reconnaisance Protection - Action Alert

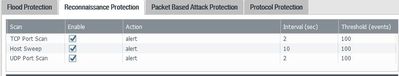
Hello,I configured zone protection, (reconnaissance protection), and enabled the tcp\udp port scan and host sweep and chose the default as action "alert".Afterwards, I noticed in the monitor logs this vulnerability appeared, "ZGrab Application Layer Scanner Detection". The severity is medium. Where do I change the action? I can change it in the ...

vp.JPG
vun2.JPG
roma by • L2 Linker
  • 20073 Views
  • 5 replies
  • 0 Likes

Need example of Configure IPSec VPN with Source NAT

Hello, I'm attempting to setup a few remote sites to a Hub site all sites have a Palo Alto 3260 firewall. All remote sites have the same internal IPs and subnets on the Trusted side and I'm needing to connect all sites using a IPSEC VPN. I would like to Source NAT but cannot find the documentation to assist in setting this up using IPSEC. Als...

Issues when installing Cortex on Debian

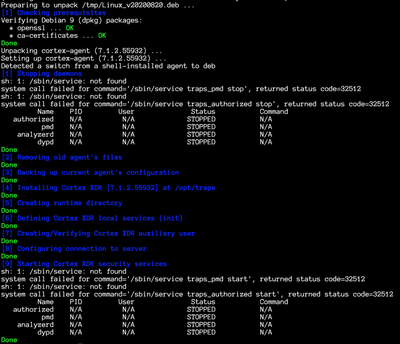
Hello, Currently, we are installing the Cortex XDR agent on Debian servers. We have followed the steps as the documentation says. But, when the services are gonna be started it shows an error: "sbin/service: not found". All the services show "Stopped" status. If I check the "/opt/traps" directory and if I run the command "dpkg -l | grep corte...

Cortex XDR.png
iscott by • L2 Linker
  • 4616 Views
  • 3 replies
  • 1 Likes
  • 24483 Posts
  • 125 Subscriptions
Top Solution Authors
Labels