General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Announcements
Scheduled Maintenance: November 14–15 (starting Nov. 14 at 12:00 AM PST)
LIVEcommunity will temporarily operate in read-only mode as we prepare to welcome Idira!
Public content will remain accessible, but log-ins, posting and community interactions will be paused during this period. Thank you for your patience!
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

dmz data flow

Hi, Please advise Hi,I have a design flaw . I am trying to test dual dmz . dmz server the gateway is on the dmz firewall . If the server in dmz wants to send data to dc server it has to go back through the same switch How to avoid this ? And also, please point out pros and cons for the below design Thanks
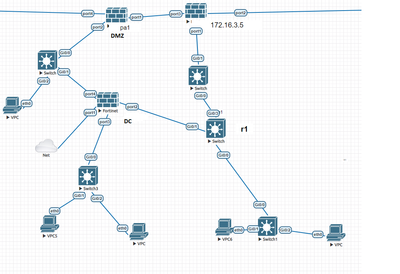
dual dmz.PNG
simsim by • L4 Transporter
  • 5938 Views
  • 7 replies
  • 0 Likes

Resolved! GlobalProtect MAC Address Filter?

Hello folks, I am being asked if GlobalProtect could be locked down to only except a specific list of MAC addresses (our corporate laptops) only. I see information about Device Block list or HIP configuration. I don't really want to specify a block list, but rather an allow list and block everything else. Is that possible? We using PA 3020 ...

OMatlock by • L4 Transporter
  • 14494 Views
  • 6 replies
  • 0 Likes

Resolved! Unable to Commit

I've just changed the configuration of the management ip address, but can't commit the change. When I attempt to submit it I get the following error: admin@PA-3050# commit...ID population failedError: id 10630 is outside allowed range [1-3583](Module: device)Commit failed admin@PA-3050# show deviceconfig systemsystem {ip-address 192.168.0.50;ne...

Resolved! A connection issue between PA and SW

Hi, PA port e1/2 is connected to switch port f1/5(L3). Both devices can see each other's ip and mac address. The Virtual router and Security zone and Magagement profile Ping are configured. but both devices cannot ping each other. Did I miss some step? Thank you

Resolved! OSPF v2 and v3 in PA

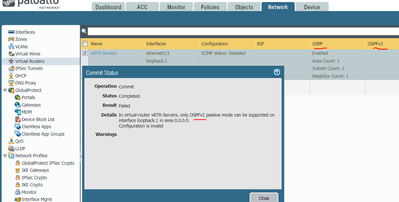
Hi, ospf is configured at the PA. please see the below screenshot. but after commit, it shows the below error message. Based on the picture, PA is using ospf2, why it shows the erro message? Thank you

DavidyPalo_0-1640018474562.png

Globalprotect PanGPS service

Sometimes our Globalprotect client application stops working on windows 10 OS.It seem to start after an uninstall\reinstall happend.After the reinstall, GP works, but then when the user reboot or logoff\login to windows, and start GP,GP removes the PanGPS service and stops working. If I do a quick repair, it works again until the next reboot. I ...

URL Override is missing

Hello, I just upgraded to PAN-OS 9.0.0 succesfully, but I cannot find the URL Override setting? Does anyone know where is it located? Thanks.

qafcopa by • L1 Bithead
  • 4980 Views
  • 4 replies
  • 0 Likes

Port Mirror Query

Hi Team,Palo Alto port mirroring will forward only a copy of encrypted traffic "https" after decrypting itor also can forward un-encrypted traffic "http" as well

PA-220 not reaching Palo Alto

Our company was recently sold off and their IT department erased our firewalls leaving them reset back the to manufacturer’s configuration. I’ve built it back as much as possible, but I’m missing something. I’ve worked with other firewall devices, but PA is proving challenging. How do I configure it to connect to serverlist.paloaltonetworks.com,...

Where do I start?

Hi I'm a network engineer being tasked to take over our PA firewalls since the guy who normally handled them is leaving. Where do I even begin to learn about this stuff? I've never had to work with these before. Thanks

Resolved! why hacktool vulnerability is set to medium action alert?

Hello,I've been looking a history entries in our threat log and it seems to me that most of the default settings for vulnerabilities - "action" are set to low, for example to "alert" - although they classify the threat as "medium" or "high". For example in the screenshot below the threat of this hacktool is set to "alert". Shouldn't this be a se...

Capture11.JPG
roma by • L2 Linker
  • 3533 Views
  • 1 replies
  • 0 Likes

Palo Alto troubleshooting tool for IPsec

Hello I established an Ipsec tunnel (policy based) between palo Alto and Cisco FW.phase 1 & phase 2 are up and running but trying to transfer data, fail.Capture packet (merge recieved and transmit) shownSource : SYNDest : SYN ACKAnd then Dest : retransmit SYN ACK. If this capture is within transmit pcap, this mean the re transmission packet...

transmit.png
  • 24483 Posts
  • 125 Subscriptions
Top Solution Authors
Labels