General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Announcements
Scheduled Maintenance: November 14–15 (starting Nov. 14 at 12:00 AM PST)
LIVEcommunity will temporarily operate in read-only mode as we prepare to welcome Idira!
Public content will remain accessible, but log-ins, posting and community interactions will be paused during this period. Thank you for your patience!
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

Agentless User-ID Not Connected (RESOLVED)

EDIT: I have resolved my issue... adding this in case someone runs into the same issue I did. Basically, I'm an idiot lol. Issue was because my AD servers are in a security zone and I needed to add a security policy that allowed the management IP address of the Palo into the AD Zone. Once that was added, I get a connected status in Server Monito...
Resolved! Firewall Events as Report

Hi All, Is there a way where, I can generate report of firewall events, Like login events from system logs, As daily basis. And I will share through email. NGFW

Migrate Panorama from VMware to AWS

Has anybody migrated Panorama from on prem to AWS? There are a few options that are available to us, and I am trying to decide which option is the best. Also, if you can list any "gotchas" during the migration that would benefit us, that would be really helpful.These are the options that I see. Option 1: Use SRM and our connected VMware on Cloud...

Fr4nk4 by • L2 Linker
  • 4979 Views
  • 2 replies
  • 0 Likes

Resolved! IPSEC ON SECONDARY ADDRESSES

Hello,just a little question it is possible to terminate a vpn-ipsec with a secondary adresses on external interface or I must use the main interface?thks,ALex

alle by • L3 Networker
  • 5299 Views
  • 3 replies
  • 0 Likes

Resolved! SSL forward-proxy certificate import

I've gerenated a CSR to give my enterprise CA. Now, I've recieved the enterprise CA-signed certificate ann imported it onto the firewall.The status reads "valid". The "Key" box is checked, however the "CA" box isn't. Also, when I select the certificate, the option for "Forward Trust Certificate" is grayed out. Did I do something incorectly when ...

Geoblocking Missing

We are on 8.1.21 - When creating a geoblocking rule I do not have the option for 'Regions' in my rule drop down. Is this due to my version OR do i need to upload a geoblocking list [how?] thanks!

IOS users are unable to connected with global protect

Hi, Iam facing the issue with global protect is not connected with IOS users and getting this error after entering username and password. )P1839-T259 12/22/2021 17:19:18:962 Debug( 127): set session proxy to 1-0x104d4b5d0.P1839-T259 12/22/2021 17:19:18:962 Debug( 237): Portal or gateway login, set connect timeout to 30.0P1839-T259 12/22/2021 1...

Joshan_Lakhani_1-1640180248925.png
Joshan_Lakhani_2-1640180278610.png

NAT before IPSEC

Hi folks, We have a vendor requiring a public IP for the encrypted traffic. Their guidance is based on Cisco configurations using "NAT before IPSEC" configurations. Can anyone share/link a guide for this configuration on Palo? Currently on PAN-OS 9.0 should it matter. Thank you.

Update to PAN-OS 10.0.8-h4 causes slow GUI response on PA-820

Hello,After updating our PA-820's to 10.0.8-h4 I have noticed the GUI to be extremely slow to respond. I am actually getting a faster GUI response from a PA-220 on 10.0.7 than our PA-820's. Has anyone else noticed this? Waiting for 'Monitor, Traffic' is incredibly slow and almost unusable. It can take up to 25 seconds for the screen to respo...

dmz data flow

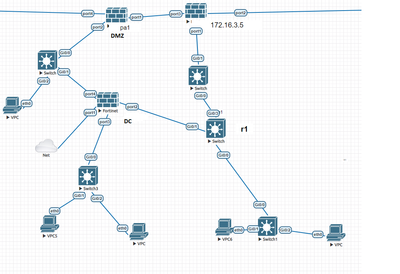
Hi, Please advise Hi,I have a design flaw . I am trying to test dual dmz . dmz server the gateway is on the dmz firewall . If the server in dmz wants to send data to dc server it has to go back through the same switch How to avoid this ? And also, please point out pros and cons for the below design Thanks

dual dmz.PNG
simsim by • L4 Transporter
  • 5937 Views
  • 7 replies
  • 0 Likes

Resolved! GlobalProtect MAC Address Filter?

Hello folks, I am being asked if GlobalProtect could be locked down to only except a specific list of MAC addresses (our corporate laptops) only. I see information about Device Block list or HIP configuration. I don't really want to specify a block list, but rather an allow list and block everything else. Is that possible? We using PA 3020 ...

OMatlock by • L4 Transporter
  • 14487 Views
  • 6 replies
  • 0 Likes
  • 24479 Posts
  • 125 Subscriptions
Top Solution Authors
Labels