This website uses Cookies. By clicking Accept, you agree to the storing of cookies on your device to enhance your community and translation experience. Read our Privacy Policy.
Click Preferences to customize your cookie settings.






Deduplication issue and config document regarding aggregator and output
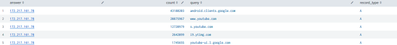
Hi Experts, I’m testing with Splunk but, I got a problem about deduplicate. I’ve been input different 1000 indicators of IPv4 after deduplicate, there is 750 indicators of IPv4. below one IP address has a different value but, after deduplicate, I can see only one indicator. My expectation is that don’t deduplicate or there is multi value for t...

 Raido_Rattameis