Next-Generation Firewall Discussions
Palo Alto Networks Next-Generation Firewalls provide true, complete visibility everywhere, along with precise policy control. Ask your questions or provide insightful answers in the discussion forum specific to NGFW.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Announcements
Scheduled Maintenance: November 14–15 (starting Nov. 14 at 12:00 AM PST)
LIVEcommunity will temporarily operate in read-only mode as we prepare to welcome Idira!
Public content will remain accessible, but log-ins, posting and community interactions will be paused during this period. Thank you for your patience!
Next-Generation Firewall Discussions
Palo Alto Networks Next-Generation Firewalls provide true, complete visibility everywhere, along with precise policy control. Ask your questions or provide insightful answers in the discussion forum specific to NGFW.
About Next-Generation Firewall Discussions
Palo Alto Networks Next-Generation Firewalls provide true, complete visibility everywhere, along with precise policy control. Ask your questions or provide insightful answers in the discussion forum specific to NGFW.

Discussions

Welcome to the Next-Generation Firewall Discussions!

To make this forum valuable and enjoyable for everyone, please review the following guidelines before participating: Rules and Best Practices Be Respectful: Treat fellow community members with professionalism and courtesy. Constructive discussions are encouraged; disrespectful or inflammatory comments are not. Stay On-Topic: This board is d...

JayGolf by • Community Team Member
  • 4875 Views
  • 0 replies
  • 1 Likes

Monitoring SD-WAN Tunnel-IF via ping

Hi Guys, We're looking to connect multiple Palo Alto devices to our core Palo Alto via SD-WAN. In some cases, we have three internet connections at the customer site, each connected through a different ISP. Our goal is to monitor each tunnel by pinging the destination tunnel interface IP address from our Monitoring Tool throught our Core Palo Al...

DHenze_0-1731336658860.png
D.Henze by • L1 Bithead
  • 3157 Views
  • 4 replies
  • 1 Likes

Clientless VPN - Application is not accessible

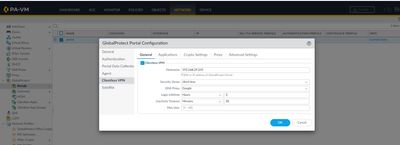
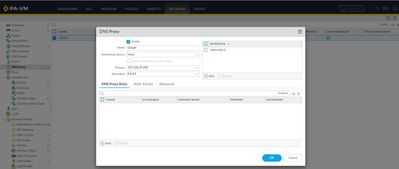
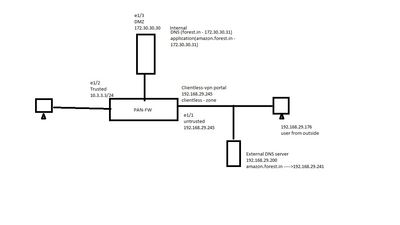
Hello All, This is my topology I have configured Clientless VPN hosting two application as, paloaltonetworks.com (external-application) and amazon.forest.in (internal hosted application). But i am unable to access the application that hosted inside. In this question have attached my configuration also. other than that there is no sent byte f...

qst.jpg
q1.jpg
q2.jpg
Q3.jpg

10.2.10-h9 Log Display Bug?

In the release announcements at Support PAN-OS Software Release Guidance it says that 10.2.10-h9 is the preferred release but on this page it also says that displaying filtered logs doesn't work properly and points you to a fix in 11.1.5 However this problem with log display is not listed in the known issues for 10.2.10 and I can't find a desc...

djr by • L4 Transporter
  • 1762 Views
  • 2 replies
  • 0 Likes

Resolved! How download a base image for Pan-OS 820

Hello. Good morning. I am trying to update my tall stick to version 10.1.12. However, when loading this update the system tells me that I need to load the base image 10.1.0. I have tried to find the base image on the support portal but have been unable to download it. Does anyone know where I can get it? The computer I am upgrading is a PaloAlto...

Resolved! CVE-2024-9474 PAN-OS: Privilege Escalation (PE) Vulnerability in the Web Management Interface

Hello!I just received and was reading this email CVE-2024-9474 PAN-OS: Privilege Escalation (PE) Vulnerability in the Web Management Interface and if I'm reading it right, the guidance is to upgrade to 10.2.12-h2 or greater (I'm on a PA-220, 11 is not supported). I've been trying to stick with the Preferred versions here Support PAN-OS Software ...

VBenfanti_0-1731943900461.png

Adhering to OpenSSL Security Level 2 Post-Uprade to PAN-OS 11.1 & LAter

Hello, In the PAN-OS upgrade guide there is a new step (step 7) when upgrading to PAN-OS 11.1 & later which refers to regenerating or re-importing all certificates to adhere to OpenSSL Security Level 2 requirements. Is there any easy way to check the status of existing certificates to ensure they meet this standard? Will any referenc...

Windows-Update configuration PA-1410

Hello, I have a Microsoft Configuration Manager Current Branch 2403.It uses WSUS to get updates catalogs and download them. The server itself has its own way to retrive updates, it does not go via WSUS. Does anyone know how to configure this? I've used this website to configure a url category "windows update": https://learn.microsoft.com/fr-fr/...

Security Policy for SSL & Web-Browsing only

Hi, I was wondering, is it bad practice to create a security policy with only the applications SSL & Web-Browsing in it? Ensuring best practice security profiles are on the policy as well. I've tried searching the web for suggestions and might be missing it. If someone can point me in the right direction?

ArthurAT by • L1 Bithead
  • 1399 Views
  • 2 replies
  • 0 Likes

Resolved! BGP on 3220 series

hello all I am working on a BGP configuration on a HA 3220 series install the BGP status is staying at connect not establish I enabled BGP on the IP addresses inbound /outbound -- no hits on the policy Q are there show commands or debugs that can help me determine what the issue is ? many thanks

S.Byrne by • L3 Networker
  • 1908 Views
  • 2 replies
  • 0 Likes
  • 1658 Posts
  • 63 Subscriptions
Top Solution Authors