General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

Resolved! How could i drop"unknown RADIUS authentication protocol"?

Hi! Recently we were receiving in our environment alerts of failed authentications from different random IP's and random usernames, i was able to reduce them following the next article: Detecting Brute Force Attack on GlobalProtect Portal Page - Knowledge Base - Palo Alto Networks, and creating a dynamic list, adding tags with forward logs, drop...

RTudon_0-1717363128954.png
R.Tudon by • L1 Bithead
  • 3295 Views
  • 3 replies
  • 0 Likes

PA-410 Firewall not fetching dynamic and software updates

We have a customer who is not able to fetch software version and dynamic updates In CLI, we checked reachability to updates.paloaltonetworks.com, and we are able to reach and also updates.paloaltonetworks.com address is getting resolved we then restarted the management server from CLI still no luck . we then manually added the dynamic updates ...

Resolved! Zoom phone custom signature thru: ssl-req-chello-sni

Hi everyone! We are currently moving our phone system to zoom, and we had an issue with the zoom application, some of their traffic its categorized as an incomplete causing that some calls hang out, or don't ring, I made an custom application, using the signature ssl-req-chello-sni and pasting the complete server's name that was registred in t...

R.Tudon by • L1 Bithead
  • 3198 Views
  • 1 replies
  • 0 Likes

Missing information on ACC

The ACC tab on Panorama shows inconsistent information about traffic, even though logging profiles on the managed firewalls is correct and send all traffic and threat logs to Panorama. Panorama ACC seems to only show "sactioned" applications, missing all other details. The ACC on the managed firewalls is accurate.This problem started with PAN-OS...

Senibo by • L1 Bithead
  • 1488 Views
  • 1 replies
  • 0 Likes

Resolved! Same Mac address shared by two paloalto firewalls

Hi, I have seen strange behaviour between two palo alto firewalls. I have pair of PA-3020 and Pair of PA-500 in Active/standby scenario. They serve two different networks but to provide interconnect between two networks they (Eth 1/3) are connected to Cisco Nexus switch via FEX (VLAN 129). Has anyone seen a case where two different models of th...

DCN by • Not applicable
  • 13513 Views
  • 4 replies
  • 0 Likes

Block scanning from shodan

Hello, Anyone have successfully block scanning from shodan.io? www.shodan.io ? It looks like Checkpoint has written specific signature to block shodan scanning, http://blog.checkpoint.com/2016/01/04/check-point-threat-alert-shodan/ -E

Delete Shared Objects in Panorama

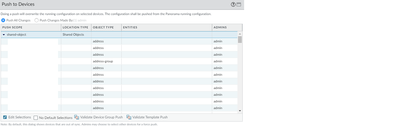
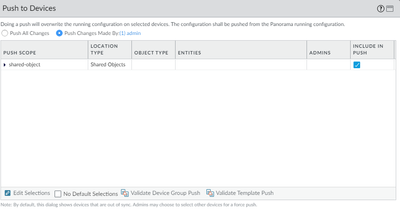
Hi. I want Delete Shared Objects in Panorama Pusht to Panorama ↓↓↓↓ Equipment A and B do not have their addresses registered in the shared policy. It keeps bringing up addresses and service information from other firewalls. I want to delete the shared policy without using the push changes made function. The panorama software versi...

DFA.png
제목 없음.png
캡처.PNG
qmso475 by • L3 Networker
  • 4525 Views
  • 2 replies
  • 1 Likes

Resolved! NFR Bundle License

Hi, For NFR bundle license, I see the description as below: "PA-1420, NFR bundle subscription (Advanced Threat prevention, Advanced DNS, Advanced URL filtering, GlobalProtect, Advanced WildFire, SD-WAN, Standard support), 1 year (12 months) term." Just to confirm, is it the bundle license already include support as well? So in case custome...

Resolved! User ID group mapping, not pulling groups

I have a problem, I'm setting the user ID group mapping, I can pull users, but not groups, I see 0 groups, I restarted the service, no luck, I verified all server monitoring is connected, and traffic is going to DC'd, the PAN-OS is 10.1.5, I have a similar setup in a pair of firewalls that are on pan-os 9.1.13 with no issues, any advice that po...

Resolved! GlobalProtect - Cannot connect to local gpd service

Hi there! I have a little problem with GlobalProtect and I don't know how to solve it..I use Ubuntu 18.04Each command to globalprotect (for example globalprotect help OR globalprotect connect) returns the answer:Cannot connect to local gpd service.I tried to restart gpd service (sudo systemctl restart gpd), it didn't helpCommand systemctl stat...

ogoili by • L0 Member
  • 70403 Views
  • 4 replies
  • 0 Likes

Email Notifications

hi,I would like to forward an email notification for specific alerts, ONLY to the person to whom the incident was assigned to.I don't see any subtype option to the Distribution List. Has anyone found a solution to achieve this ? (slack messaging is not an option) thank you

Expedition not importing NAT or security policies from PA-3020s running PAN-OS 9.1

I'm working on a project to upgrade 2 x PA-3020s each with their own configuration into an HA pair of PA-1420s and am having trouble with Expedition. I've tried importing the devices using the API key and also by exporting the running-config.xml file as a superuser and manually importing it into Expedition. Both are giving the same results. My "...

  • 24458 Posts
  • 125 Subscriptions
Top Solution Authors
Top Liked Authors
Labels