General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Announcements
Scheduled Maintenance: November 14–15 (starting Nov. 14 at 12:00 AM PST)
LIVEcommunity will temporarily operate in read-only mode as we prepare to welcome Idira!
Public content will remain accessible, but log-ins, posting and community interactions will be paused during this period. Thank you for your patience!
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

Resolved! Web-gui access with no secure certificate.

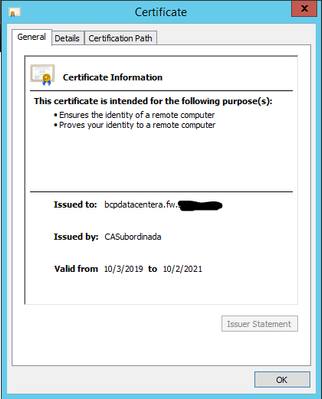
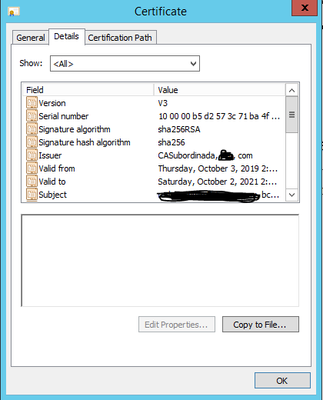
I access via GUI from Chrome and observe that the connection is not secure.I created the certificate for the firewall, but Chrome keeps saying that my connection is not secure.How can I solve this problem if the AC I have is internal to the company?Is there any way to generate certificates with AES-GCM?in chrome, the following legend appears to me.

image005.png
image002.png
image006.png
image007.png
SaulGlz by • L1 Bithead
  • 21953 Views
  • 8 replies
  • 0 Likes

Firewall idmgr High Availability State Showing difference

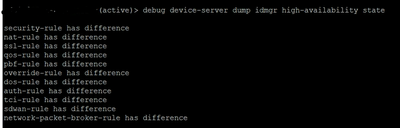
I have configure a RMA replacement HA device by following below guide How to Configure a High Availability Replacement Device - Knowledge Base - Palo Alto Networks I follow until step 10 need to use below command to check the state debug device-server dump idmgr high-availability state Result showing difference. I also tried to reboot and c...

JiaXiang_0-1659429368761.png
JiaXiang by • L4 Transporter
  • 4069 Views
  • 3 replies
  • 0 Likes

Migration / Import of configuration only to a destination vsys, a particular vsys

Migration / Import of configuration only to a destination Vsys, a particular vsys. Hello good afternoon, as always thank you very much for the support and collaboration as always. Please your your suggestions, advice and / or guidance, how is it possible to perform the import/load config, of a PA configuration, to be loaded only, but only in a...

Metgatz by • L4 Transporter
  • 4177 Views
  • 2 replies
  • 0 Likes

Resolved! Unable to Deactivate PA - VM license through Panorama

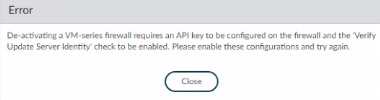
Accidentally, while terminating PA VM in hosted in AWS, the license was not removed from the firewall. I am trying to deactivate the license through panorama but it is giving us an error. Also clicking on Complete manually gives us the same error as follows: Have followed this article here https://docs.paloaltonetworks.com/vm-series/9-1/vm-...

MicrosoftTeams-image (2).png

PAN platnium support

I have Platnium support with PAN and I opened a TAC case yesterday evening explicitly requesting TAC support Monday-Friday between 8am-5pm US EST. The case went to APAC TAC and he said that he is looking into the issue. I sent me an email to tell him that need "TAC support Monday-Friday between 8am-5pm EST". Got an email back from TAC that "I...

dtran by • L4 Transporter
  • 4329 Views
  • 5 replies
  • 0 Likes

Resolved! Panorama settings - auth key issue

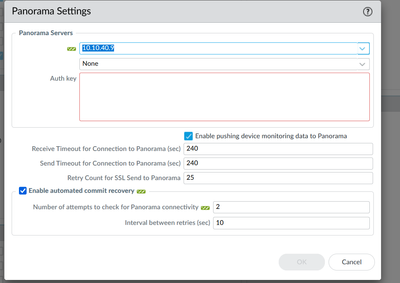
I have successfully on-boarded a FW to Panorama (both version 10.1.6-h3) using auth key. I've set a single use for key so now it disappeared as expected. Now I am trying to change Panorama settings (to disable auto recovery) and it won't allow me to click 'OK' button without auth key. Surely this is a bug? You don't have to re-authenticate FW...

santonic_0-1659699282812.png
santonic by • L6 Presenter
  • 4442 Views
  • 1 replies
  • 0 Likes

Multiple unexpected failovers - need help understanding FW behavior

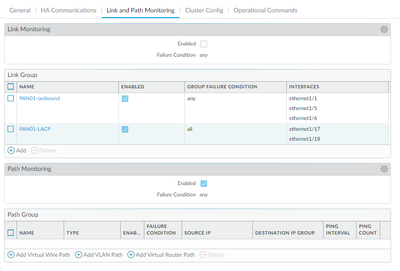
Hi all, We have two PA-3220 devices configured in Active-Passive mode (no preemption). Firmware version is 10.1.2. In the last three weeks we had three failover incidents that we are investigating (no device reboots though). We've opened a support case regarding this, however I'm here just to confirm if the explanation we've been given is corr...

Nielsen_0-1659673836438.png
Nielsen by • L0 Member
  • 5064 Views
  • 2 replies
  • 0 Likes

Please help with log collectors and collector groups in Panorama mode!

Hello all! We have had a single Panorama appliance running in Panorama mode as a local log collector in its own collector group. Firewall logs are sent to Panorama, and all is working well. We now have procured a second Panorama appliance for HA. Hardware, disks etc., are all the same, and I've successfully set them up in HA, synced and healt...

ECMP Virtual Router restart question

Very quick question. We have set up another virtual router (currently running two with active users) and are trying to enable ECMP on the new virtual router. When we attempt to enable ECMP, a firewall message states that 'Enabling/Disabling ECMP and configuration changes require a virtual router restart. Existing sessions may be impacted.' ...

What exactly is the naming convention for Prisma Access?

We have Prisma Access ( Panorama Managed ) in our environment. Example of one of the compute locations is named as "europe-central-cranberry". Is this an SPN? And after certain bandwidth will be get a new SPN in europe central like "europe-central-xxx" so in total we will have two SPN in Europe Central Compute location? Will these names remain ...

Resolved! It appears as a blocked URL, but you can still access the page without decrypt

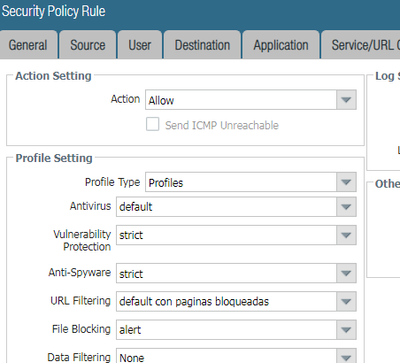
I want to block the page XDRAY.COM. In this case it is about XDRAY.COM https://ydray.com/ I have created a URL filtering profile and I have it applied in the security rule where it works ok, however, although in the url filtering monitor I see this session as block-url, the user can open this url Any idea why it may be failing? Attached are ...

Alpalo_0-1659431671536.png
Alpalo_1-1659431743545.png
Alpalo by • L4 Transporter
  • 3855 Views
  • 2 replies
  • 0 Likes

Resolved! How in the hell do i open a support case?

I see no way of opening a support case... I called the tech support phone number, but it hangs up with me beacause I have no support case #... I didn't think customer service could actually get worse, but it has

jreed2 by • L0 Member
  • 2623 Views
  • 1 replies
  • 0 Likes

FIPS-CC Security Functions- can you trust PAN documentation?

According to PAN documentation: https://docs.paloaltonetworks.com/pan-os/10-1/pan-os-admin/certifications/fips-cc-security-functions MS-CHAPv2 is not compatible with FIPS-CC mode. It is recommended to use RADIUS with TLS. However, in my test with my PAN-820 in FIPs mode, it works perfectly with RADIUS PEAP with MSCHAP-v2. Can you even trus...

dtran by • L4 Transporter
  • 2439 Views
  • 2 replies
  • 0 Likes
  • 24481 Posts
  • 125 Subscriptions
Top Solution Authors
Labels