General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

App-ID Policy to Explicitly Block - Allow WiFi Calling

Hello,I tried searching but was surprised to find no ready answers for this.. I'm trying to determine the App-ID policy to explicitly block or allow voice calling over wifi (or wifi calling) on Verizon, AT&T, etc. I can't seem to find this in App-ID's database. Any advice?Thanks!

REganEVO by • L1 Bithead
  • 7239 Views
  • 2 replies
  • 0 Likes

Global Protect will connect then immediately disconnect

A GP issue I am dealing with at the moment is where the client will successfully connect but I cannot ping anything on my network. It appears to immediately disconnect. I have attached the log files if anyone may know how to help determine the cause. I have gone through them but I am not having any luck just yet. The user is running the late...

nthen by • L3 Networker
  • 12135 Views
  • 8 replies
  • 0 Likes

Enabling Jumbo Frames on HA Pair

I have an active passive PA850 pair, and want to turn on jumbo frames. I wondering about the best order-Can I:do the passive unit first, and rebootfail over and do the primary then fail back. Any issues with the HA function while one unit has jumbo enabled and the other does not?Was thinking I'd manually set all interfaces to 1500 firstAny other...

NeilR by • L2 Linker
  • 4350 Views
  • 1 replies
  • 0 Likes

Resolved! GlobalProtect HIP check issue

HIP object is correctly setup. We are testing the missing patches HIP check object and noticed that an VPN endpoint is showing 3 missing patches (on the HIP report).However the machine is showing it's installed these patches already.How does Palo detect the missing patches as Windows is showing them as installed? Using ver: 8.1.10

Resolved! DNS Security - High Risk Sites

thumbnails.trvl-media.com used by www.hotels.com to host its images is classified as a high risk siteIf this is a false positive, how do I get Palo Alto DNS Service to take a second look or find out why it's classified as high risk? How are other people using the high risk category? Are they using url blocking, sink-holing, or custom file block...

DMZ, inside, outside - is it simple thing?

Hi there. I have a PA-200.Internal net is 192.168.0.0/24 eth1/2 , inside L3 interface (default gw) - 192.168.0.254One external ip address is using for outside inteface, eth1/1.For connection to Internet I typically use pair inside-outside with:1. NAT : dynamic-ip-and-port to outside interface address nat-rule2. Security policy "allow from ins...

mxe2fmk by • L1 Bithead
  • 10016 Views
  • 6 replies
  • 0 Likes

Unable to reach GP Portal while on internal network

Hi All, I was working with a site that has a PA firewall with a GP Portal and Gateway. Some time ago, I had an issue where my users couldn't upgrade their globalprotect version while in the office. I was able to resolve this issue by creating a No NAT rule where if the source was internal and the destination was the IP of the portal. That work...

ce1028 by • L4 Transporter
  • 7061 Views
  • 4 replies
  • 0 Likes

Inability to Download GlobalProtect Client from Firewall

We are currently attempting to update our globalprotect client on our Palo Alto firewall, a PA-500. The version we are attempting to download is 5.0.8. Currently when attempting to download we get the following error Which hasn't given us much indication of what the issue is, and how to rectify it.We have checked the logs in an attempt to find...

0 (2).png

Dual Isp - Two webserver

Hi all, i have a problem, maybe stupid for all of you, but i can't understand how to configure my pan-220.I had only one isp and all it's ok (internet, webserver, 2 vlans, etc).Now i have another ISP and, if is possibile, i need to publish a web server with this connection (without failover. only publish a webserver with another ip)Anybody can h...

Resolved! aggregated-ethernet - combine SFP+ and Cu port possible

Hello We increased our Internet speed beyond 1Gbs. The connection between the firewall node and the Internet switch is facilitated using one SFP-Port (1Gbps). Is it possible (and supported) to combine Cu-Ports and SFP-Ports (both with the same speed and duplex) into one aggregated-ethernet? All interfaces on the Internet switch are 1G Cu ports.

SSL Decryption severe throughput impact

Hi EDIT2: Please see follow up post belowEDIT: One open ticket is being investigated by TAC escalation as a possible known issue. I will update again as I know more. In the last month 3 different customers came to me with the same issue - when SSL Decryption is enabled their HTTPS throughput/bandwidth decreases noticeably, one customer said it d...

ShaiW by • L4 Transporter
  • 7164 Views
  • 2 replies
  • 0 Likes

GLobalProtect Portal not found

I can get to the GlobalProtect portal on the PA firewall from outside and login and download GlobalProtect client. However, after installing the client and try to connect, it says "Portal not found" Any ideas? Client is joined to domain, it did not ask for credential when trying to connectSSL CA and Gateway is self signed on PA and Root CA and ...

Resolved! Policy-Based Forwarding with dual ISP's

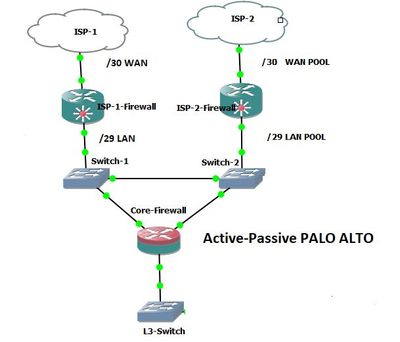
Hi ALL, We are planning to build active passive PA with 2 ISP's and want to send S2S VPN traffic through ISP1 and Internet traffic through ISP 2. We are running static routing for both the ISP.Can someone suggest how to configure PBR in PA.

PALO_ALTO.JPG
Yusuf_PA by • L1 Bithead
  • 9494 Views
  • 6 replies
  • 0 Likes

downtime for migration from MPLS to VPN with BGP with bgp routing

Hello community! I have currently two sites connected through MPLS and I plan to configure a VPN with bgp routing to migrate traffic. I am calculating the downtime that may require the migration from MPLS with static routing to the VPN with bgp routing. I´m considering the following:- Routes learned from IBGP has default AD = 200 and static rout...

Carracido by • L4 Transporter
  • 2797 Views
  • 1 replies
  • 0 Likes
  • 24465 Posts
  • 125 Subscriptions
Top Solution Authors
Top Liked Authors
Labels