General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

Resolved! A critical error has been detected preventing proper boot PAN 3220

I received a replacement firewall from another and when I tried to put it into operation this message appeared, .( "[1K Welcome to the Maintenance Recovery Tool[mATTENTION: A critical error has been detected preventing proper boot[68Dup of the device. Please contact Palo Alto Networks to resolve this[67Dissue.r support@paloaltonetworks...

Resolved! Trouble routing from Guest zone to Internal Server

I'm not sure where to turn from here but my organization is trying to do a configuration we haven't set up before related to our student self-service system. To try and summarize the issue, we have a guest-wireless zone that we need to allow anybody access to another server that is internal on our production network. Our system architect regi...

cnorwich by • L1 Bithead
  • 4616 Views
  • 5 replies
  • 0 Likes

Resolved! Site to Site IPSEC Clarification

I'm moving from a Cisco ASA to a Palo Alto firewall for the first time. I've imported the config to Expedition and am prepping it for import to the firewall, but I noticed only the first of my crypto peers for each tunnel was imported to an IKE gateway. After some research it seems I'm going to need a separate IKE gateway for each remote peer as...

Palo Alto Search Filtering in Contains

Hello, I write a basic python code for 'contains' filtering in in rule name search. And I want to share with community also community can give an advice for me. The code: """"""""""""""""""""""" def generate_output(numbers) : output_strings = [] for number in numbers: output_strings.append("(name contains 'Rule " + str(num...

tombombadil_0-1706780527481.png

Global Protect Asymmetric routing issue

Hey team hope someone can help me. I am pretty new to Palo and I am trying to setup Global Protect PreLogon in our corporate environment. I have managed to get it all working in the lab (awesome) now doing that in the live environment is different ball game... Issue is that I am getting asymmetric routing, our default route goes out via another...

Shadmin by • L1 Bithead
  • 5922 Views
  • 4 replies
  • 0 Likes

Radius Group for GP authentication

Hi All, We need to setup a specific user group in Radius should only access the GP. No other users should access GP. Currently authentication method set for GP is Radius and in the same radius we need a specific group of users only to authenticate. May i know how i can acheive this please? Do i need to setup something like Data Redistribution se...

Resolved! PAN-OS Uprage PATH to 11.0.2-h3

Confirming the Upgrade Path - Currently version 10.2.3-h2 upgrade to 11.0.2-h3 1. Download 11.0 2. Download and install 11.0.2-h3 Am I correct? do I need to reboot twice for this OS upgrade? NGFW

Radius Authentication and NPS

Hello everyone, I'm having trouble configuring palo alto with a Radius NPS server. Basically we do not want to use chap protocols to avoid enabling reversible password. So we wanted to use EAP-TLS but it does not seem compatible with Palo Alto. Then after some research we noticed that palo alto recommended to enable PAP protocol here https://kno...

zakergfx by • L1 Bithead
  • 2569 Views
  • 1 replies
  • 0 Likes

NAT & port forward with dynamic IP on outside/untrust/Internet facing interface?

So, I'd like to accomplish the following: Client A on the Internet needs to access port 80 on server B. Server B resides behind the PA FW in the trust zone. The untrust zone consists of only one interface with a DHCP configured L3 interface. This IP is expected to change from time to time. What I have configured is the following: a) A NAT ...

O.Olsson by • L0 Member
  • 2122 Views
  • 1 replies
  • 0 Likes

One isp to multiple isp site to site tunnel

Hi Team, We want to configure ipsec site to site tunnel between two locations as per below details 1) Location A having single ISP address i.e Wan address (1.1.1.1/30) will connect to location B having 2 ISP address (2.2.2.1/30 & 3.3.3.1/30) and form a IPsec site to site tunnel. Is it possible for doing the Same ?. If yes how my traff...

Disable IoT Service as workaround of PAN-216043

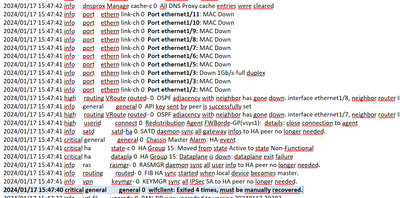
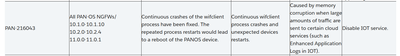
We are having a problem in our PA cluster. One of the firewalls is restarted and HA is activated. This problem occurs approximately every 3 weeks and the error I found is from Wifclient and according to the paloalto documentation the workaround is to disable the IoT services. https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g00...

EliasCoranti_1-1706792909590.png
EliasCoranti_0-1706792814014.png

Resolved! Show hit count in CLI

I was searching this forum and official documentation, but I can't find the following: Is there equivalent to Cisco ASA "show access-list acl_name" command in the PAN-OS CLI. I am looking for the command that will show hit count for every configured security rule. Also if the object groups are used either in source or destination address it woul...

Resolved! Point to site VPN on pan 0S 11+ (Client to remote VPN server)

I remember reading some where Palo Alto firewalls works like a client to access remote VPN servers eg I can setup the PALO to access a OpenVPN server and give access to user on my palo managed local network to access that remote resource, than user installing the OpenVPN application on their computer and connecting. Hope I'm making any sen...

din100 by • L3 Networker
  • 3015 Views
  • 3 replies
  • 0 Likes

Impact of run tcpdump on every interface.

Hi, We need to execute tcpdump in PA-VM for a specific reason. We need to TCPdump data from firewalls for 15 minutes at various intervals; there is no specified source or destination. When we run tcpdump from every interface, we want to know if it has any effect? The current utilization Management CPU 15% Data Plane CPU 65% Session Count 2484 ...

Data From ACC Not shown for 15 minutes and 1 hours

Hallo All, I have issue after upgrade PANOS 11.1.0, The ACC can not shown data for 15 minutes or 1 hours. except both I mentioned, all time running well. We have restarted log-reciver and still not shown data 15 minutes or 1 hours. We have conclusion for update to 11.1.1 for fixing issue. After upgrade to 11.1.1, issue still same. ...

  • 24479 Posts
  • 125 Subscriptions
Top Solution Authors
Labels