General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Announcements

Welcome Idira to LIVEcommunity!

Our community just got stronger! Explore new identity security resources, connect with experts, and discover more ways to learn and collaborate.

Meet Idira

General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

Wrong HIP match

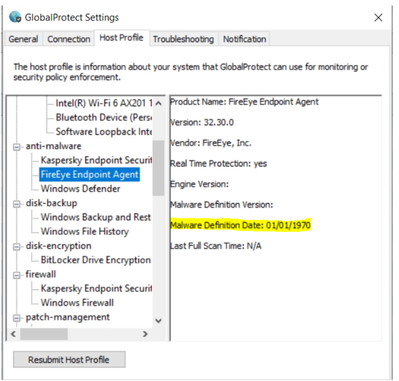
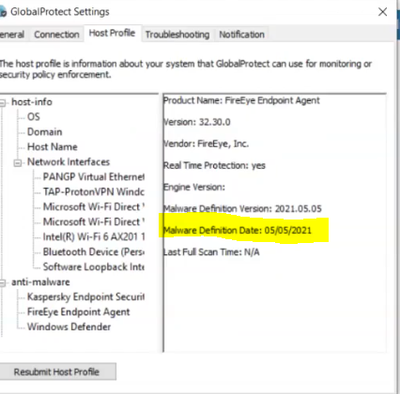
Dear All,issue: I have the firewall 5220 with PAN-OS 10.0.3 and I am facing an below issue:-As GlobalProtect 5.2.6 is released with support for OPSWAT v4 only while OPSWAT v3 is discontinued starting from 5.2.6, I tried to test it on a few machines. We apply HIP checking for the below:- FireEye Endpoint Agent – Installed & Real Time P...

Jafar_Hussain_0-1620221429240.png
Jafar_Hussain_1-1620221429270.png
Jafar_Hussain_2-1620221429286.png
Jafar_Hussain_3-1620221429307.png

Resolved! Captive Portal Redirect Issue

Hello! Quick question:I have captive portal set up for one zone and it works well, where my captive portal "redirect host" ip is in the same zone/subnet as my users who need to authenticate. But I'm needing to expand this so that users from several zones/subnets can authenticate via captive portal. The problem I'm having is that for users in ...

Prevent OSPF routing loops - Area 0

Hello, We have a PA5050 with a couple of VRs. VR1 is the main VR with interfaces into the main customer networks, internet access and a 3rd party linkVR2 is for GlobalProtect clients and a separate internet link for the GlobalProtect Portals/Gateways There is an eBGP Peer between the VRs so that VR2 can learn all the corporate networks and the ...

gcampbe9 by • L0 Member
  • 2993 Views
  • 1 replies
  • 0 Likes

GlobalProtect: Existing user session..?

Hi all.. I'm sure this will be a simple question to answer, but I can't find any explanation. In the following snip from our GlobalProtect traffic log on a PA200:12/23/2014 17:142/23/2014 17:14GlobalProtect gateway user login succeeded. Login from: 75.89.141.221, User name: w__0.12/23/2014 17:142/23/2014 17:14GlobalProtect gateway user logout s...

thatguy by • L2 Linker
  • 10264 Views
  • 3 replies
  • 0 Likes

Understand App_overrride

Hi, We did a change from another vendor to PA. We realise that backups (vmware) were transferring very slow. So we created a app_override in order to avoid L7 in this VMware traffic. After that the spped for backpus got better.So i have several qestions:-Why is this happening? whats wrong L7 inspection does in order to slowness?-what kind of tra...

BigPalo by • L4 Transporter
  • 4496 Views
  • 7 replies
  • 0 Likes

Resolved! ssl inbound inspection

Hi community, Will PA support inbound ispection if key exchnge mechanism is DHE/ECDHE ?.i hope PA wont be proxying inbound SSL connection. whether PA changed this behaviour from any versions?is there is a way to configure PA as proxy( we have server certificate/key installed in PA, only issue is PA resources. So if my website traffic is usually ...

Google Earth (Pro) and SSL Decrypt

Anybody figured out a the magic combo to get Google Earth (Pro) not to warn on startup with SSL Decrypt? Before you ask "yes" SSL decrypt is working no errors or warnings in browsers (i.e. CA's in trust store) and yes I thought about the ICA issue and imported the GTS CA 1O1 cert on the off chance that was the issue. Any other ideas outside "b...

PeterT by • L2 Linker
  • 5146 Views
  • 2 replies
  • 0 Likes

Host with sinkhole action, what to do ?

Hello Bro, We have subscribed to the Palo alto DNS-Security feature and we have it applied now.after few days, I have a dynamic object now with many host has been sinkholed for contacting a malicious domains.Many Domains contacted, what is the recommendations regarding this many malicious domains contacted by our users? what is the ...

Resolved! DNAT with different external port to different internal port.

Hello, how are you all, I hope you are well.I would like to do the following: In Fortinet is the following possible, DNAT, with Public IP example:198.10.100.100:8081 ( alternate port ) ---DNAT-Mapping---Private IP destination 192.168.100.100:80 ( Port 80) This in PALO ALTO, how is it configured, please your support, thank you very much.Greetings...

Metgatz by • L4 Transporter
  • 7266 Views
  • 6 replies
  • 0 Likes

Resolved! PAN-OS 10.5 WiFi HotSpot

Hello World, I am simply attempting to setup a portal to where my guest are able to accept the terms of service in order to access the internet. Is this possible with Palo Alto? I've done this on other vendor platforms and it wasn't rocket science to achieve this. Upon my research I ran across the following links. https://live.paloalt...

Decrypt-error with Inbound Decryption DHE or ECDHE on 8.1.3

Greetings all, I feel like I'm probably missing something simple here, but I'm running into a decrypt-error issue on 8.1.3 in regards to a server that is negotiating DHE or ECDHE ciphers with the client. On Chrome I get: ERR_SSL_VERSION_OR_CIPHER_MISMATCH And on Firefox I get: SSL_ERROR_NO_CYPHER_OVERLAP If I turn off decryption for this or set...

jsalmans by • L4 Transporter
  • 23366 Views
  • 17 replies
  • 0 Likes

LED's on startup

Recently migrate to a pair of 3200 series firewalls. Everything was fine and dandy until we powered them down to migrate to the correct rack. Once we powered them up, one came up fine, but the other has a green power light and nothing else. the fans are going crazy like it's trying to come up, but stays like that. Tried consoling in upon bootup,...

Error when I try to add the SAML Identiti Provider for Okta

Upload SAML IdP Failed. No IDPSSODescriptor node found. Any ideas? Here's the file I'm trying to import <md:EntityDescriptor entityID="http://www.okta.com/exk....."><md:IDPSSODescriptor WantAuthnRequestsSigned="false" protocolSupportEnumeration="urn:oasis:names:tc:SAML:2.0:protocol"><md:KeyDescriptor use="signing"><ds:KeyIn...

Firewall is sending traffic when becoming passive for a few minutes

Hello friends, I am experimenting a strange behaviour. When performing a manual failover with the command: request high-avaliability state suspend, the firewall that become passive continues sending traffic to the BGP peers for about 3 minutes (ICMP packets), this is causing that those peers activate an anti-loop feature that freezes our MAC add...

  • 24485 Posts
  • 125 Subscriptions
Top Solution Authors
Labels