General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

ISP failure after 2-3 packet drops

We are using one VOIP application over internet which is disconnecting after drop in 2-3 packet. For seamless connectivity we are looking for ISP failure if 2-3 packets are dropping.We can configure path monitoring ( By default ping interval is 3sec and count is 5) . We want to know this path-monitoring will fail after 15 consecutive pings or ho...
Deepak_K by • L3 Networker
  • 3379 Views
  • 2 replies
  • 0 Likes

Resolved! Globalprotect check operational system on the portal/gateway without collecting HIP data and using HIP profiles/HIP objects?

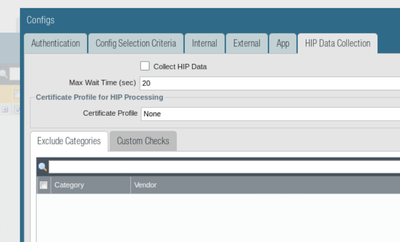
I found out that you can use the operational system without a HIP object/profile to do things on the Gateway/Portal even if the collection of HIP data is stopped on the Portal. Portal config: Gateway Config: Can someone tell me why when I try to check if the operational system is Linux in a HIP object/profile and I attach it to secu...

NikolayDimitrov_1-1621011523428.png
NikolayDimitrov_0-1621011296270.png

Global Load Balancer (DNS) for GlobalProtect Portal

Looking to set up multiple data center redundancy for GlobalProtect and I'm unsure if Palo Alto would support a global load balancer (GLB) for the solution. We have global load balancer DNS servers that detect the status of our DC internet connections and will remove the IP's from the DNS entry if an ISP is down. The TTL on the DNS entries is ...

yostie by • L0 Member
  • 8705 Views
  • 1 replies
  • 2 Likes

Resolved! Always On Global Protect and file share access

I now have GP connected automatically with a certificate pushed out via InTune. This is on a Surface Laptop running Win 10. I typically log in with face recognition. After I log on and notice that I have TCP/IP access through the GP connection and internal DNS is working - I am trying to then go to a file share. \\whatever\sys$\whichever say. I ...

HTTPS Response pages

Hi, I know that there are many threads here about this. We would like to show the response pages for https. We saw this link but i have several doubts:https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000ClFKCA0This command is enabled globally: "set deviceconfig setting ssl-decrypt url-proxy yes". So, is this command decrypt...

BigPalo by • L4 Transporter
  • 8024 Views
  • 9 replies
  • 0 Likes

Resolved! Block wetransfer Upload

Hello everyone,I have a problem with allowing wetransfer to download and blocking the download,Wetransfer is part of the 'Online-storage-and-backup' category.The choice is to block this category and create a bypass just for downloading on wetransfer,On my side, I tried to create a URL whitlist category:we.tl/*wetransfer.com/downloads/*Do you hav...

QuentinH by • L1 Bithead
  • 10164 Views
  • 4 replies
  • 0 Likes

Bulk Emails

Hi Team, We need our PA devices to block bulk mails from our trust zone.We have an email relay in our organisation.Can we achieve it through custom vulnerability signature by creating an signature and applying threshold value

Resolved! PBF for incoming connections

NAT translation goes like this:Destination NAT and Security Policy:https://docs.paloaltonetworks.com/pan-os/8-1/pan-os-admin/networking/nat/nat-configuration-examples/destination-nat-exampleone-to-one-mapping.htmlPolicy Based Forwarding:Polices > Policy Based Forwarding >Under General Tab > Name "Incoming"Under Source Tab > Zone "Out...

jmora by • L1 Bithead
  • 3125 Views
  • 1 replies
  • 0 Likes

Site to site vpn

Hello, can anyone please help me for the below request? site to site vpn setup for oracle cloud using palo alto CPE. Can someone please tell me recommend setting for Phase 1 (ISAKMP) and Phase 2 (IPsec)?? thank you!

Poo173 by • L0 Member
  • 2302 Views
  • 1 replies
  • 0 Likes

Mitel telework phone one way audio

Anyone ever seen a one way audio when mitel phone configured for telework mode is on the inside trusted network? The mitel border gateway is in the dmz nat'd to an outside public ip, and works fine with all phones but telework enabled phones when on the inside lan. Thanks, Jeff

  • 24460 Posts
  • 125 Subscriptions
Top Solution Authors
Top Liked Authors
Labels