General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

SSL inbound inspection wildcard certificate

Trying to configure ssl inbound inspection for one of my web sites hosted internally. The IIS server has many sites being served thru host headers. All of the SSL bound sites use the same wildcard certificate *.external-domain-name on this server. I export this cert with key and import into pa.I make decryption policy to match a specific url in ...

Panorama - HA Group 10: Anti-Virus version does not match

Hi Experts, From Panorama, we're managing around 20+firewalls. In Panorama system logs, we're seeing " HA Group 10: Anti-Virus version does not match error messages".Though the errors are self expalantory , how do we confirm out of 20 firewalls which firewall is configured with HA Group ID 10 which is generating this error message. Please assi...

Resolved! Update 0.9.46 Broken (at least for me)

Hey all, So my Minemeld appliance updated to 0.9.46 at some point which broke the system. I was able to temporarily fix the issue by just changing the symlink in /opt/minemeld/engine from 0.9.46 to 0.9.44. Obviously, this is not ideal. When I look in the 0.9.46 folder I see that there are a lot of files that are missing that are present in t...

How to report false positive if I'm not a customer

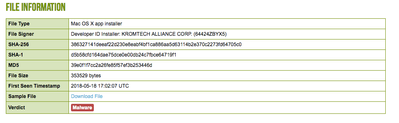
Hello there, I represent Kromtech company(https://kromtech.com) which produces MacKeeper app (https://mackeeper.com). We have report from our partners that your WildFire service marks our products as Malware.We would like to report false positive but I didn't find a way how to do that if I don't own your service. Could you please help me with th...

Screen Shot 2018-05-18 at 10.41.48 AM.png
ze0adik by L1 Bithead
  • 3305 Views
  • 1 replies
  • 0 Likes

Resolved! VM50 on Server 2016 HypperV

Does anyone know if the VM50 is supported on Windows Server 2016 Hyper-V? I have downloaded the PANOS 8.0 Vhdx file and installed it based on the Server 2012 R2 Guidelines, but every time I try to start the VM, I receive a message the virtual machine failed to change states. I've verified my CPU, Memory and Network settings, and can't figu...

User-ID/Facebook allow group

Hello, I am having trouble with this configuration. In a Windows domain environment. I installed User-ID on server and confirmed User-ID is running and IP/user mapping is all listed in the monitoring log. User-ID agent is connected in the firewall. I created two AD groups one that permits FB and one that blocks it. I created two security ru...

MineMeld Splunk App

Hi Guys, I'm new to this community. At the moment, we are actively exploring MineMeld in our environment and would like to know if there is any connectors available for Splunk to consume intel collected by MineMeld .Please advise.Thank you.

Is my upgrade the cause of a vlan not working

After I upgraded my palo alto fro 7.1.15 to 7.1.16 I had a report that a certain vlan can not longer access the internet. I have a back up of the config before the upgrade and one after the upgrade and so far I don't see any change in virtual routers that would have cause the PA to block the traffic. I know that is very little information but i...

jdprovine by L4 Transporter
  • 5405 Views
  • 9 replies
  • 0 Likes

Arp getting time out after 30 min on sub interface

We are facing some starnge issue .We are having an ISP which is connected to sub interface.We are trying to repalce it with new one. Same Subnet /29 but different IP. NAT rules also same because same subnet.The issue we are facing is when new ISP configured , we are getting the ARP entries for ISP gateway on Palo Alto Sub interface however its e...

Static Routes

We have a Cisco ASA that has tunnels to our branch offices. An Example is 192.168.9.0/24. The local network is 192.168.10.0/24. The lan port of the ASA is 192.168.10.10. The lan port of the Palo Alto is 192.168.10.1. When I change the gateway to one of the servers to use the Palo, it can ping a host on the 192.168.9.x network and the remote...

Resolved! Risky ports

What are the risky ports we should not allow from user zone (internal network) to external network (internet / external network)? Like we don't allow 21/23 etc, please suggest other ports too.....

SumitB by L1 Bithead
  • 3973 Views
  • 3 replies
  • 0 Likes

Resolved! excluding threats from TAP allerting?

We have a TAP interface listening to a number of vlans (internal and external) We get a lot of noise in our allerts from threats we would prefer not to get alerted on. For example, presently "SipVicious" scans are occuring all the time to what are actually unused IP addresses on one VLAN. How can we dial these out??? ThanksRob

MineMeld and ELK

Hi all, I'm having some trouble parsing MineMeld events into Logstash, and then into ELasticSearch. Does anyone have any resources available for this kind of set up?

tom.dell by L0 Member
  • 4614 Views
  • 2 replies
  • 0 Likes
  • 24450 Posts
  • 125 Subscriptions
Top Solution Authors
Labels



