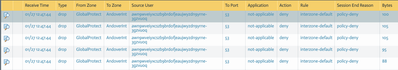
Weird GP source username on traffic logs
I came across this weird source name on the traffic logs while checking a GlobalProtect issue. Has anyone seen this case? Other users' logs are displayed with corporate\domain correctly.

Hi. who can help me this topic?Person A must configure vpn with person B. Person A must configure two vpn connection and all data flow to vpn 1 node but if vpn node1 goes down, aoutomatic all traffic must flow through with node 2.
HelloWe have a Firewall PaloAlto with free space 509MB in partition /dev/md2, and 609MB in partition dev/md5, actually we need to upgrade the PanOS since 7.1.18 to 8.1.12, and there are 5 PANOS to upgrade, so the information is keep in /dev/md5 but before the installation We would like to know if the /dev/md2 root partition has little free space...
I am trying to block Internet Explorer traffic going out to the internet from my internal users. I have decryption in place and followed this article: https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000ClEdCAKI am seeing some websites being blocked but some of them are not despite decryption. Has anyone tried blocking IE?P...
Hello -Basically I would like to start blocking external email access from the internal network such as Yahoo Mail. I don't want to block access to Yahoo itself, just inbound email from Yahoo and other sites like that. Is there any documentation on how to best accomplish this? Thanks in advance!
Planning to implement a certificate-based authentication method in Global protect VPN in some of the iPad. All other clients should be able to log in just using with LDAP(username/password). The customer doesn’t have GP Portal license. Can we achieve this on 8.1.x PAN-OS with two client authentication profile? Anyone did this one 8.1.X OS?
Which is the latest maintenance release from 8.0.4 to 8.1? I can see on my firewall that 8.0.19-h1 and 8.0.20 are available. Thank you,
Have had an open case with support since August 2019 with HIP checks setup for Global Protect. There are options to allow HIP checks for a large number of different AV vendors and their products. The issue we have come across is that we have defined specific AV vendors that can be used and all others are denied. The vendors we have allowed we...
Hello,I am trying to establish a successful VPN connection between my Palo Alto firewall and a Check Point firewall. The VPN tunnel on the Palo Alto side shows all green for phase 1 and 2, however on the Check Point side I keep getting a failure per the log "IKE failure no response from peer".In the "Monitor" > "System" log of the Palo Alto t...
Hi Gang, Excuse me for my ignorance. We had firewalls Palo literally thrown at us, and instantaneously put into production (not great!). I have a pair of Palo's in HA Active/Passive with preemptive enabled on active/primary. These are in turn, patched to an INET switch (internet handed off via a single ethernet patch cable to this switch). We ...
Hi, I was wondering when I went through the bootstrap documentation, it mentions that it should display logs of the bootstrap even if successful but in either case, nothing appears on the console, not even a single word about bootstrap... where should this be displayed or how can i check these logs?
Hello, I am trying to create rule that allowed specific users from the active directory. Strange enough on the rule, i am unable to get active directory users. Please advise
I have one more query, If I change week encryption to strong encryption in tunnel traffics like Global Protect, IP sec tunnels, will it get affect the clients ??Of course We have to check the peer side before we change the encryption methods & algorithms for IPsec tunnel but what about global protect ??If we change the GlobalProtect IPSec Cr...
Hello Folks,I'm planning on getting two new Palo Alto firewalls for setting up IPSec tunnels. I think the first tunnel will be a primary tunnel and the second tunnel will be back up. I'm tempted to set up my new firewalls as active/passive HA, to make life easy. But to be sure, please could someone suggest what are the advantages of using active...
Sorry if this is a dumb question, I'm still a bit new to PA. I've recently had a case where a few workstations cannot access anything beyond the local network. A trace shows that they can reach their default GW, but not the next hop, which is the PA. As a workaround, I found that changing their IP address resolved the issue. I then found that if...
| Subject | Likes |
|---|---|
| 5 Likes | |
| 3 Likes | |
| 3 Likes | |
| 1 Like | |
| 1 Like |
| User | Likes Count |
|---|---|
| 5 | |
| 4 | |
| 3 | |
| 2 | |
| 2 |





