Next-Generation Firewall Discussions
Palo Alto Networks Next-Generation Firewalls provide true, complete visibility everywhere, along with precise policy control. Ask your questions or provide insightful answers in the discussion forum specific to NGFW.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Announcements
Scheduled Maintenance: November 14–15 (starting Nov. 14 at 12:00 AM PST)
LIVEcommunity will temporarily operate in read-only mode as we prepare to welcome Idira!
Public content will remain accessible, but log-ins, posting and community interactions will be paused during this period. Thank you for your patience!
Next-Generation Firewall Discussions
Palo Alto Networks Next-Generation Firewalls provide true, complete visibility everywhere, along with precise policy control. Ask your questions or provide insightful answers in the discussion forum specific to NGFW.
About Next-Generation Firewall Discussions
Palo Alto Networks Next-Generation Firewalls provide true, complete visibility everywhere, along with precise policy control. Ask your questions or provide insightful answers in the discussion forum specific to NGFW.

Discussions

Welcome to the Next-Generation Firewall Discussions!

To make this forum valuable and enjoyable for everyone, please review the following guidelines before participating: Rules and Best Practices Be Respectful: Treat fellow community members with professionalism and courtesy. Constructive discussions are encouraged; disrespectful or inflammatory comments are not. Stay On-Topic: This board is d...
JayGolf by • Community Team Member
  • 4877 Views
  • 0 replies
  • 1 Likes

i can‘t commit after upgrading to 11.0.2 version

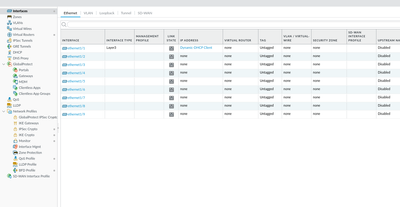
hi, i can't commit after upgrading 11.0.2 version from 10.2.X, For testing purposes, I changed any of the small options and did not make any other changes, but I cannot commit them。 tip: Details Partial changes to commit: changes to configuration by administrators: admin Changes to policy and objocts confguration DHcP Client Interface has no...

david.ge by • L1 Bithead
  • 2139 Views
  • 1 replies
  • 0 Likes

Can Palo notice and react to a flapping Internet link?

Hi All, We have simple setup, when firewall is connected over physical interface to a L2 switch, while L2 switch is connected to 2 CPEs of different ISPs. Obviously, next hop for our firewall going out is an interface of the CPE. We are tracking default routes for both ISP using route monitoring feature. Unfortunately, that does not seem to...

File Blocking block/continue issue

Hi everyone, I'm trying to setup fileblocking on PanOS 11.0.2-h1 and I'm facing strange behaviors. With some sites I get block or continue page, and DataFiltering logs. With others, I get an empty file download for both continue or block actions and a traffic log with threat as end of session reason : I prefer to get a block or continue page ...

masdidier_0-1706806542509.png

Policy commit failures due to profiles exceeding platform capacity using version 10.1.8-h2

We have not updated the number of profiles and have been successfully committing policy for probably a year with this same number of policies, but all of a sudden we are not able to commit policy pushes either from gui or cli. We have gone through and deleted alot of shared profiles and are still getting the following error: Error: Total num...

Interface migration to fiber over SFP 10G

Hello team, I have a Palo Alto 3220 cluster that is connected to a CORE switch over ethernet and I need to migrate that connection to fiber over SFP 10G converter. I am trying to define a procedure to migrate with no downtime and I had thought to start with the standby node, suspending this node for HA, dehabilitating the link monitoring inter...

ALDIAZEG by • L0 Member
  • 1717 Views
  • 1 replies
  • 0 Likes

Packets dropped: forwarded to different zone

We have a PaloAlto firewall that we have configured differrent zones, everything is working fine, except for a specific traffic between IP 10.40.129.49 and 172.26.2.58. The 10.40.129.49 is located on a subnet directly in a zone defined on the firewall, 172.26.2.58 is a remote host over a WAN link going via another zone on the firewall. Traffic...

vnkhwazi by • L1 Bithead
  • 4374 Views
  • 5 replies
  • 0 Likes

Malicious IP address log sudden increasein traffic

Our Malicious IP Traffic Alert typically registers a few dozen hits a day. However over the last weekend this has suddenly increased to a couple of thousand a day. I cannot see anything different apart from the quantity. The IP addresses are the same or from the same subnet. Should I just leave it or what actions would you suggest.

peeryog by • L1 Bithead
  • 4306 Views
  • 2 replies
  • 0 Likes

IP blocked then allowed

Hi, I'm reviewing a logs regarding a low reputation IP which in the first log it's action is dropped, and 5 minutes later 3 logs with action allowed. Why does it dropped then allowed it?Logs category: spyware action: dropped Threat Name: CobaltStrike.Gen Command and Control TrafficThreat ID: 18005

PA-410 bug - disable-predefined-reports

PA-410 running PAN-OS 11.1.0. This firewall had been upgrade from 10.2.latest to 11.1.0. After making an unrelated change to mitigate CVE-2023-48795, validate fails with: Could not get schema node for xpath /config/devices/entry[@name='localhost.localdomain']/deviceconfig/setting/management/disable-predefined-reports Commits fail with: devicec...

jasonroy by • L3 Networker
  • 4414 Views
  • 5 replies
  • 1 Likes

Strata Sales training guide

Hi team, I m new in the system as a sales solution specialist i see the Prisma SASE and Prisma cloud having the proper sales pre sales post sales guide to understand the in depth product where i came to strata there is no Sales guide i found can anyone help me to get how i can start the Strata training from sales than pre-sales after sometime ...

  • 1658 Posts
  • 63 Subscriptions
Top Solution Authors



