General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

Security Policy

hello we have taken over support of a PA there are a number of entries configured under the Security policy our customer has reported an issue that we are trying to troubleshoot can I use packet trace or packet capture to see what policy an IP Address is using ?
Change panorama mode from "management-only" to panorama-mode

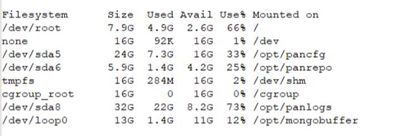
Hi, We have a panorama (version 10.1.6) in management-only mode. This panorama is maging 6 FWs. We would like to change the mode to panorama in order to get the logs. So what implications should keep in mind? i think it should be necessary to increase add a new disk with high space in Vmware? Its that correct? what is the recommendation about...

SIZE.JPG
BigPalo by • L4 Transporter
  • 12210 Views
  • 7 replies
  • 0 Likes

FW wrongfully declared as a spare

Hello, One of my FW is wrongfully declared as a spare and thus I can't update it without transferring licences from another FW. It seems that I can't chage this property on my managing asstets page. Can anyone help. ? Regards

PA440 management interface doesn't take configuration

I used to think I knew how to do this stuff, but apparently not. This is an out of the box configuration of a PA440 - I set the firewall to configure system in standard mode and use static addressing. Initial configset deviceconfig system ip-address 192.168.1.1set deviceconfig system netmask 255.255.255.0set deviceconfig system update-server up...

Resolved! PAN-OS Certificate exprie and panorama

Currently, Panorama and the firewall are connected. However, the connection will be disconnected in April 2024. Even if the connection is lost, is it possible to connect through syslog?

qmso475_2-1706166397204.png
qmso475 by • L3 Networker
  • 1987 Views
  • 1 replies
  • 1 Likes

Resolved! Force user GlobalProtect client refresh

Piggy backing off of this earlier thread (LIVEcommunity - Force GlobalProtect Portal refresh of connected clients? - LIVEcommunity - 514881 (paloaltonetworks.com)). It there a way whether by registry or whatever, to force the client to grab its new config. We are switching over from on-demand to always-on and want to have users connect without t...

Claw4609 by • L5 Sessionator
  • 12116 Views
  • 10 replies
  • 0 Likes

Resolved! API call fortmat

Hello, I want to know, what is the issue with this API call?<request><content><upgrade><install><sync-to-peer>yes</sync-to-peer><version><lastest></lastest></version></install></upgrade></content></request> I would like to sync the content update by API call...

RobertoParra_0-1705959598802.png

WildFire Appliance Config Status Out of Sync

Hi, We are currently facing a issue with our WildFire Appliance, and we seek your assistance in resolving it. The config status at the WildFire Appliance is out of sync, with detail this " '/config/device/entry[localhost.localdomain]/deviceconfig/system/update-server' on remote, but not on panorama ". i am not sure how to get this fix. kind...

Screenshot 2024-01-24 145854.png

URLs visited

We use Palo Alto firewalls PA3020. How can I generate a report that shows how many times a URL has been visited? Also, can we see who visited the URL? Thanks!

CVE Description clarification

I'm looking at CVE-2023-6795 and in the description I see "enables an authenticated administrator to disrupt system processes and potentially execute arbitrary code with limited privileges on the firewall" This means that all admin included the readonly admin like the SuperUser (ReadOnly) can do the execute arbitrary code?

XSOAR Access denied

Hello We have a user with the same permissions that the other users in XSOAR and in CSP who cannot log in XSOAR. It keeps giving an error: Unauthorized 401403. Has anyone seen this? Regards

  • 24475 Posts
  • 125 Subscriptions
Top Solution Authors
Top Liked Authors
Labels