Want to allow specific file name file blocking
Hello Team, Please let me know is there any way to allow particular file name . Example:- I want to allow for all user that they can download test.txt but i want to block all other .txt file.
Dear Team, The following error is occurring in the firewall type : ctd-agent severity : high event : ctd-agent-connection description : Failed to establish GRPC connection to service : failed to start grpc connection with address ----- I would like to know what causes this error and how to fix it If anyone has had a similar experience, p...
Hello all, Our client company uses FQDN A and B that Nslookup the same IP, and the firewall has a DNS access policy applied with these FQDN.Recently, the customer deleted the DNS of B, and if it is normal operation, it should be normal service with FQDN of A, but DNS blocking issue occurred. In addition, entering FQDN refresh from the CLI does n...
Hello all,Hope you are doing well!Currently, we are checking the process through Hip profile setting. However, some PCs are facing an issue where the Process Check information list is not displayed. I checked the HIP Object settings and found that they are using the same settings and that the same program is running on the PC.In addition, I trie...
Hi there,Has any one been able to successfully use the XML API to query the predefined EDL lists and have the ENTIRE list returned back in the response? When I attempt to query say the panw-torexit-ip-list, the XML response only returns using this command: https://<firewall>/api/?REST_API_TOKEN=**********&type=op&cmd=%3Crequest...
I have a Paloalto cluster and in the active FW I get the following error when trying to download and install the dynamic updates. Anybody can helps me? Regards
Mobile users connect to wifi through to active directory authentication but in log-trafic- source users name not showing.(For laptop/desktop source users showing perfectly- this authentication also through AD)
Hi, my firewall is set to send PDF reports daily, attachments are usually not visible when receiving emails using Outlook. I tested sending reports to Gmail, but I can't see attachments when I use Outlook to receive emails. But you can see in the web version of Gmail Studying the source code of this email found that Outlook can display attac...
A strange trend we're seeing the application ms-update return a threat of: PNG File Chunk Length Abnormal It's been occurring since June and the png files related to the threat are named: sw_saber_rey.png sw_saber_luke.png sw_saber_vader.png Anyone else come accross this threat and application/file reference?
Hi, Today, I could not access A2 (Auto Assistant).When I access https://autoassistant.paloaltonetworks.com/#/dashboard/my-view-case,returned 504 Gateway Time-out.Why? A2 is very helpful for my customer support business. Thank you.
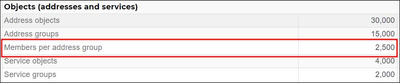
Hello all,As shown in the attached photo below, the limit on the number of members in the address group of PA-3220 is 2500.1. We are going to apply about 2000 Object Members per address Group to the PA-3220, is there any performance issue? If there were, what performance issues would there be?2. If 4,000 objects are grouped, is there no problem ...
On firewall datasheets we have two max session values :Max sessions (IPv4 or IPv6) = AMax concurrent decryption sessions = B Question in here : are these two separate buckets ? lets imagine decryption sessions reach out to Value B , does it mean that firewall still able to process no-decrypted sessions ?
Hi All, I have followed a few guides but cannot manage to get a /30 RIPE subnet advertised to our ISP. I have followed the following guide for route distribution, however, i cannot see them in the Local RIB and RIB out tables. https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000Cm2ICAS Any help is greatly appreciated. Ou...
is it just me or anyone seeing SIPVicious Scanner Detection alerts a lot recently?
Good afternoon! I have a set of Palo Alto PA-820s and 850s that I'd like to converge their configurations. For instance, have the same whitelist or blacklist policy outlines that I can add or remove websites, countries, and so forth. I see I can share policies between virtual routers, but is there an easy or easier way to copy a policy from o...