Resolved! Logging for deny/drop policy
Hi Team, what is the recommended/ best practice logging option for policies with action set as deny/drop? is it "log at session end" or "log at session start"?

Hi, Can we achieve the following points, 1.Required only our office domain user can able to access upload/download file2.Hotmail user can only access for downloading / uploading block3.Another domain user (Guest user) only downloading the file uploading block I know that we can block other domains but can we achieve this requirement downloading...
Hello All, I installed minemeld on aws instance, when I am trying to logging getting "Error checking credential: bad gateway". I checked Minemeld services and getting error as : minemeld-engine FATAL Exited too quickly (process log may have details)minemeld-supervisord-listener RUNNING pid 1921, uptime 0:08:47minemeld-t...
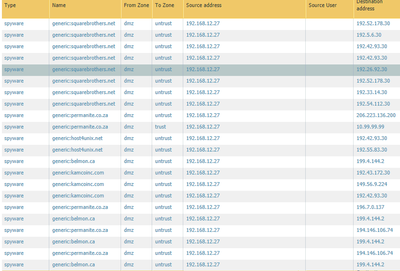
Hi Guys, I am seeing a ton of "generic:<random-url>" hits in my threat logs under the spyware category for DNS queries from my email spam filter server out to the world. I have DNS security set up on the Palo so they are being sinkholed, but there are a ton of them, and several dozen different URL's. The spam filter uses a proprietary sof...
Just wondering what is best practice for this?We have a /29 on our outside interface. We are using the IP assigned for client NAT translation.Over the coming months we’ll be configuring several VPNs to the same cloud provider. Should these terminate via a loopback or just on the physical interface and we should add an address to the physical int...
I have a consultant who is asking if the Global Protect VPN would connect with an OpenVPN-based client? I suspect he is working from a Linux PC.does Palo support it?
Hi Guys, Our company has recently made several acquisitions. All of them have non-palo alto firewalls. We will be migrating each of non-palo firewalls to our palos.Now, for migrating the rules, we are using expedition. But, some of them have overlapping IP addressing. We are planning to resolve that problem with NAT.But wanted to ask here: Is th...
Does MM have the ability to remove HTTP:// and/or HTTPS:// from a list of URL's before creating the output file for EDL?
I have PAN running version 8.1.17 and it is configured with two DNS servers on the management interface, you know the usual, nothing special. I have security and NAT rule on the PAN firewall the uses FQDN. Is there a way to detect when the PAN fails to query the DNS server? Is there anything in the system log that will tell me the PAN can NOT...
Hi Community,We wish to add a batch of users to the local database, I'm just wondering if anyone has had experience with scripting this or doing this in batch. With the command "set shared local-user-database user testuser" it requires separate user input to add the password so this is out of the question. I thought the command "set shared local...
Hi everyone, We have our PA Firewalls in different countries all around the globe.Lets call them Country1, Country2. Country3 and so on.All locations are connected to each other via S2S VPN.We have Panorama in location Country1. And it manages firewalls in all countries over the S2S VPN.At all sites, we do have local admin accounts.Now, my conce...
Hi All, I use PA-220's in HA pairs often, and I've always used a straight-through cable to connect port 7 and 8 from FW1 to port 7 and 8 on FW2. I've never had ANY issues with this configuration. I just learned that PAN says to use a crossover cable when connecting the firewalls directly to one another like I have been doing all this time with ...
has anyone noticed that globalprotect portal allows a user to download the software without authentication? I'm running 5.0.4. Here's the exact link:https://{IP/FQDN}/global-protect/getsoftwarepage.esp .
I am trying to access http://www.brokercheck.com from behind the PAN firewall via dynamic NAT without any success. I have other customers behind different PAN firewalls, regardless of PAN OS version, with the same issue access website http://www.brokercheck.com. The FW rule is wide open "any any accept log" It works for customers NOT behind PAN...
Hi Guys,Just want to seek your inputs about what can be the best integration approach for this scenario.Currently, the VLAN gateway is in my core switch and I will be introducing PA FW into my network. I want to have control and visibility for my intervlan switching, will the virtual-wire approach be the best for this scenario? I am a bit not co...
| Subject | Likes |
|---|---|
| 3 Likes | |
| 3 Likes | |
| 3 Likes | |
| 1 Like | |
| 1 Like |
| User | Likes Count |
|---|---|
| 4 | |
| 3 | |
| 3 | |
| 2 | |
| 2 |





