Block Facebook App
We are using a Palo Alto Firewall and have facebook blocked on the browser, but the mobile app still works on Android and iPhone. What is the catch all way to block the facebook app?
Greetings On PAN-OS 7.1.8 configuring EDL is giving some unexpected results - I have an application based security policie set for my PA management IP addresses to fetch the updates i.e. "paloalto-updates, widlfire, pan-db-cloud, ssl and web-browsing" with service set to application default. No profile actions set to block. After populating the...
Hello I'm on 7.1.7 PANOS and I need to generate traps for testing purposes. I didn't find in manual such CLI command. please advice me how to generate from CLI or if it's not possible how to make a workaround (ie. using trap on virus condition or so) With regardsSLawek
Has anyone set up a PAN alert for egress bandwidth utilization? For example: If any internal host transfers more than (x) GB in (y) Minutes to the Internet - throw an alert.
Hi All, I have met a problem with access to my Active Pan Device by Web Admin GUI.I can access by SSH Console and I can access to Standby Device in HA System.My device: PAN 3020, OS Version 6.1.4. Have anyone meet the same problem, please share the solutions. Error logs---------------------2017-03-21 11:04:21.009 +0700 Error: pan_authd_user_is_l...
Hi alli have this little issue: I have panorama with a pa 5050 cluster firewall 7.1.5 with wildfire licence. I have a rule to control smtp traffic with a wildfire profile.In the wildfire i have disable benign responce and in the configuration i have selected this: The problem is that i don't see anymore, after a malicous responce, the recipent/s...
I know it is possible to get unused rules since last reboot, but it is obvious the data is in Panorama. Is there no way to get a list of rules not used since a specified date? https://live.paloaltonetworks.com/t5/Learning-Articles/How-to-Identify-Unused-Policies-on-a-Palo-Alto-Networks-Device/ta-p/53202
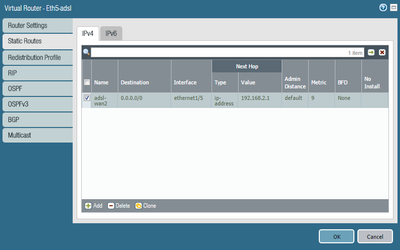
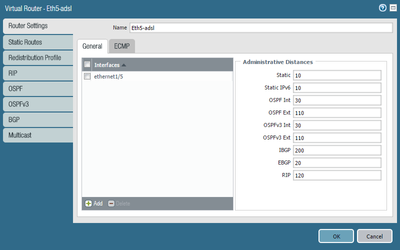
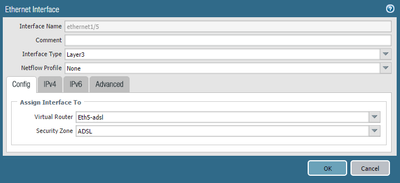
Hi all, i've connected a adsl modem to our 3020 to redirect some clients to, configured the interface as dhcp client, the port successfully gets an ip address from the modem but i can not ping the modem interface from firewall's cli. I might be missing a simple step but i'm fairly new with PA, any help appreciated, thank you
Hi All, Do we have an application for Line Messenger: https://line.me/en/ Cannot see it in Palo database. Thx,Myky
Hi everybody I like to know if there is a way to block incoming connections attemps to port TCP 22. I have an end-customer which has lots of connections to his public ip range 0.0.0.0/24 to port TCP22 but not hit the vulnerability 40015 (SSH User Authentication Brute-force Attempt) because it neves triggers the child signature 31914 (SSH2 Login ...
heyhey we have some problem with old system that are beeign stuck after some tome it is working and on the logs we see the session end reason is "tcp-reuse" my questions are:1) what should be happaning on the network flow for this end-reason log to apear2) will the FW generate some traffic to the client and server to "close" their existing conne...
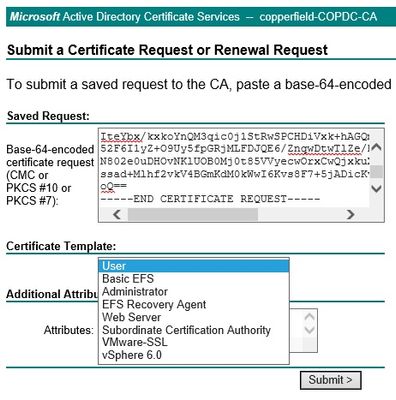
Hello folks! I have seen a few articles and documentation for generating CSR and submitting to Microsoft CA for subordinates. What about just a root stand alone enterprise Microsoft CA? I am preparing to configure a Global Protect portal, generated/exported my CSR, pasted into the Microsoft CA interface, but unclear of what option settings to s...
Hello Guys.I have a question about syslog service of PaloAlto Firewall. Customer want to send a logs of paloalto firewall to syslog server using TCP. Can PAN possible to do that?Thanks.Regards,Roh
On Feb 2017, some universities, Mozilla, Cloudflare, and Google released this paper on corporate and desktop HTTPS interception. First they figured out how to identify when someone connects to a web server through an SSL interception appliance. Then they found that most corporate "man-in-the-middle' appliances expose security vulnuerabilities. B...
I've been using the cli debug pcap captures for a number of issues recently but was frustrated in the last one by a lack of detail. In this case I was capturing OSPF (debug routing pcap ospf on). When I viewed the capture it looks more like a summary of the hello messages without the contents. Is there a generic was to turn up the level of infor...