Ip missing in output
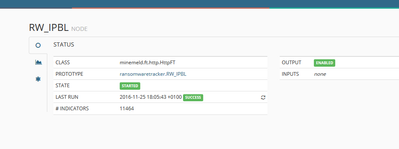
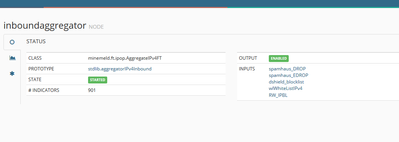
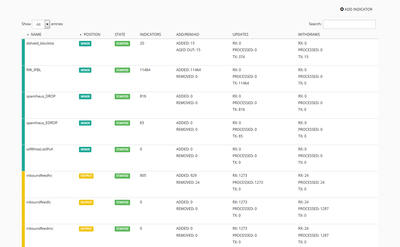
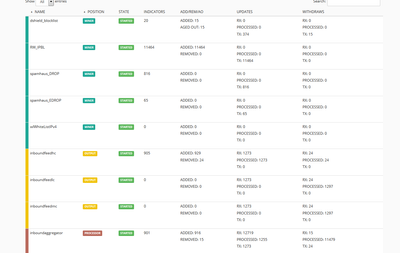
Hi, I have default profile. I added a node "RW_IPBL NODE" that has 11464 ips But after processing I only see 900. Generated I think by other nodes.What can be wrong? Thank you
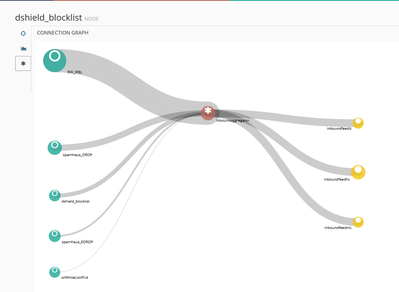
Hi, We have a Pa500. It read that only permit 10 list with a max 5000 ip's.it is right? I have deployed a MineMeld with default configuration. I have a list configured in Pa-500 https://ip-minemeld/feeds/inboundfeedhc. What does the pa-500 to be the largest list of 5000 ip? Do you only load the first 5000 ip's or do not load this list?Som...
Hey guys, We have a PA 200 as lab firewall and I want to setup SSL vpn. Can you tell me which licenses I need for it? The GP window (Device -> GP Client) is completely empty. When I check for new versions, it says "The device does not have support". The same if I want to check for new PAN OS Software. I thougt it would be sufficient with the ...
Seems like a bug any one faced in 7.0.9. We have several firewall and 2 time it happened group mapping lost suddenly and we have manaually refresh to get it it back.
I know I've seen an article/documentation on this somewhere, but I am struggling to find it. When running a show system environmentals, and more specifically the "Thermal" area for the processors, does anyone know what functions are being handled by which processor? We are running PA-5060 devices in our network. This would be helpful in our tra...
Hi, Testing with Rome release I notice we need to have trusted CA on the Minemeld webserver. You can't use the Minemeld default certificate to import on the PA firewall. So I had to manually change certificate in the NGINX. Maybe this could be included in the webinterface of Minemeld that you can upload and change the certificate?
What happens if if whitelist some IP and then MineMeld is shutdown ? Will source or destination in the rule be replaced by 'any' ?
Hi there, if we are going to the tab "Policy" we will see 7 different sub tabs. The tabs are: SecurityNATQoSPBFApp OverrideCaptive PortalDoS Protection So I know for example that Security rules are always checked before NAT rules but whats about the rest? I spent planty of time google for this information but without success.
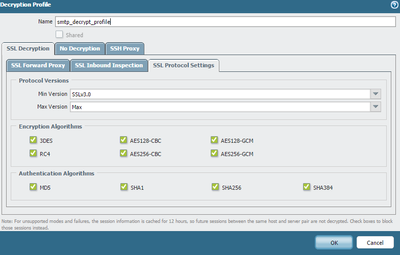
We have decyption turned on for inbound smtp trafffic. It is only decrpyting a portion of the encypted traffic. I have an open ticket with support but still working through it but I wanted to check to see if anyone else is experiencing issues. I do not believe it is something misconfigured on the firewall as it decrpyts as expected sometimes. T...
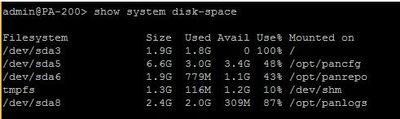
Hello , I have a problem with my firewall PA-200. When I try to open the GUI , I found an error message with a session out . You can find in the attachement this error message . I read that may be this problem can be related to the disk space. I do a show disk-space command and i found the the result in the attachement . Any one can help me to ...
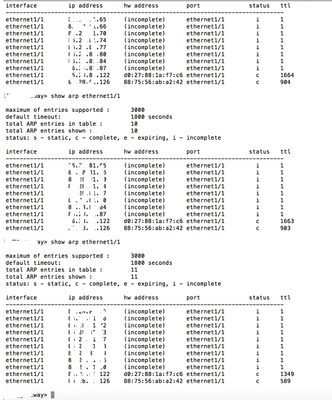
Hello All, Need some clarification on ARP table. For some reason, once we swapped the devices from 2020>3020 our ARP table is seen as incomplete but services are working fine withing on that particular external subnet (before they did but we use gratuitous arp) . Also the time out of the "incomplete" entries pretty much a second ( ttl =1): ...
Hello, GlobalProtect GW with x-auth is enabled for IPsec VPN client services. However, only one concurrent session per user is allowed and any subsequent sessions disconnects the previous session user. Same issue happens whether the user is a local account or an AD account. We need to have multiple sessions running with the same user account. An...
MindeMeld or EDL (external dynamic list) in general can whitelist Office 365 but only per destination. Is there a way do build dynamic access lists based on source IPs ?
Does anyone have any experience with configuring VPN to use the UPN instead of sAMAccountName? I'm trying to get a configuration working using a Radius Multifactor system that requires the UPN, and while I can get that part to work, I can't figure out how to control access to the VPN via AD group membership. If I put AD groups in the allow filte...
I would like to get to know which specifc traffic is being checked by specific features of Palo-alto NGFW. To be more precise after enabling all the features on the device which traffic is being checked by URL filtering , IPS Anti- Spyware and other features. The traffic must be using specific ports?