Panorama custom reports hang
Custom reports on my Panorama (9.1.6) were working fine until this week. Today, any report i run gets stuck in "please wait" indefinitely. Nothing has changed on the machine. Any ideas what i should look for?
As per the below mention snap-shot, we observed user id get changed with AD user and we have allowed the internet access to local user id which is configured in Palo Alto. Due to issue user facing internet issue. We have not configure this user in AD domain, then how user id gets change in the Palo Alto automatically ? While authenticating via ...
Hi all, I need schedule some cli command which i execute manually from SSH console like below; Command line 1: test vpn ipsec-sa tunnel Xtunnelname:XtunnelProxyIdCommand line 2: test vpn ike-sa gateway Xtunnelname Is there any way schedule tasks in palo alto? Regards.
Hello everyone, most lately have started seeing a warning messaged "Failed to Launch Help" pop up randomly while connected to GloabalProtect(5.1.5). Tried looking for KB Articles around it and could not find any. Was wondering if I could get some insight on what could be causing this and how to get rid of it? Thank you,VC
Hi Community, I have the following scenario:user_1/password_1 Active Directory credentials for login into windows system and domainuser_2/password_2 Active Directory credentials only for globalprotect authentication. I´d like to know if there is a way to change the password_2 for user_2 through the GP agent application? Thank you!
Hello Team, I moved up from Fortinet/Ubiquity, bought a used PAN 5050 and upgrade the OS to 8.1.18 for a Home Use. However, since i am new to PAN during the configuration i realized PAN 5050 does not support DDNS. In my case i am home user I don't have a Static IP. As you all know, having Dynamic IP is a pain for almost all firewalls and limited...
I understand that for an EDL of type URL, the format is either company.com*.company.com This will include any additional subdomains, whether at the beginning or the end of the URL. Regarding the forward slash, will a URL like the following be a valid entry that will be processed? company.com/subpage/QWERTY/ Additionally, does that mean only th...
We have recently upgraded our HA firewall cluster (PA-3020) from 7.1.22 to 9.1.6 following the suggested upgrade path by PA.We have captive portal in place, before the upgrade, all our corporate windows 10 laptops as soon as we power them on, they used to connect to our corporate Wi-Fi and allowed users to login as per normal.Since the time we h...
Hi guys, I believe the MISP miner for Minemeld needs a re-visit. None of the tagged indicators are being pulled by Minemeld from our MISP instance. I think there are a lot of changes to the current API as compared to the ones used by the current miners. Also, a lot of new queries such as Decay Model and Timeline can be done through API. I don't ...
Hi Team, what is the recommended/ best practice logging option for policies with action set as deny/drop? is it "log at session end" or "log at session start"?
Hi, Can we achieve the following points, 1.Required only our office domain user can able to access upload/download file2.Hotmail user can only access for downloading / uploading block3.Another domain user (Guest user) only downloading the file uploading block I know that we can block other domains but can we achieve this requirement downloading...
Hello All, I installed minemeld on aws instance, when I am trying to logging getting "Error checking credential: bad gateway". I checked Minemeld services and getting error as : minemeld-engine FATAL Exited too quickly (process log may have details)minemeld-supervisord-listener RUNNING pid 1921, uptime 0:08:47minemeld-t...
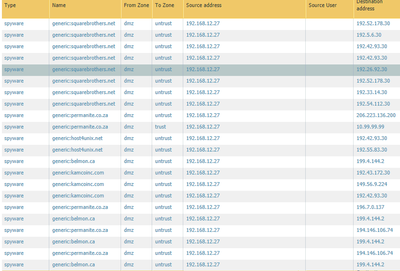
Hi Guys, I am seeing a ton of "generic:<random-url>" hits in my threat logs under the spyware category for DNS queries from my email spam filter server out to the world. I have DNS security set up on the Palo so they are being sinkholed, but there are a ton of them, and several dozen different URL's. The spam filter uses a proprietary sof...
Just wondering what is best practice for this?We have a /29 on our outside interface. We are using the IP assigned for client NAT translation.Over the coming months we’ll be configuring several VPNs to the same cloud provider. Should these terminate via a loopback or just on the physical interface and we should add an address to the physical int...
I have a consultant who is asking if the Global Protect VPN would connect with an OpenVPN-based client? I suspect he is working from a Linux PC.does Palo support it?
| Subject | Likes |
|---|---|
| 1 Like | |
| 1 Like | |
| 1 Like | |
| 1 Like | |
| 1 Like |
| User | Likes Count |
|---|---|
| 2 | |
| 2 | |
| 1 | |
| 1 | |
| 1 |




