Admin password is expiring
We have configured password profile and getting notification for that at the time of login. My query is that can i modify after admin password expired or can i get pup-op for assign new password after grace period over.
Hi all, I have been setting up the domain credential phishing with a colleague and we have run into an issue where the service account is unable to bind to the LDAP on the RODC. We have followed the troubleshooting guidelines in the following document but unfortunately we still hit the same issue. Has anyone else experienced this issue or knows ...
Hi all, I am trying to migrate one of our customers from a PA-200 to a PA-220 AND add create an HA cluster with active/passive configuration with two PA-220's I was wondering, what approach would you take in regard to achieving the above outcome? 1. Would you first configure the PA-220 in an HA configuration then migrate the configuration to the...
We have used application over ride for specific app and name is "server_443" and its working fine, we are able to see that application is showing in traffic logs. In access rule i have allowed any application from trust to untrust zone. My query is that is it compulsory to use costume application in security rule?
Hi all, Hope you all are doing Good. Guys, I have a query can we configure multiple Nat policies, security policies, address objects, address group, etc using scripts through CLI. Is my query achievable and if it is so how can we do it. Please share some articles to understand. Many thanks in advance.
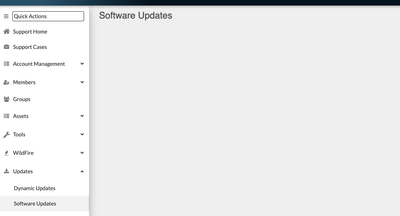
Is anyone else having issues with software updates page being blank on support portal? I see dynamic updates are displayed but not software updates. I have tried Firefox, safari & chrome with no luck.
Greetings all, I'm looking for other admins' experiences with utilizing the SSL Forward Proxy decryption options in a university environment. General overall experiences would be good but, specifically, I'm wondering about: Did you go SSL Decrypt everywhere or only on certain networks (i.e. academic networks but no residence networks for on-cam...
We are managing 4 location firewalls from Panorama. Panorama and one of the location is on 9.0.9-h1. Rest of the location firewalls are on 8.1.5.We have activated DNS security licence on that upgraded firewall which is running on panos 9.0.9-h1.We are using shared anti-spyware profile for all firewalls. If we enable DNS security setting in same...
Hi I have a PA firewall, is it possible to create an email alert for ISP link up or down in PA 220 device
Hi Gang,Still getting grips to everything so would love your help in understanding the behaviour of traffic when it is NATed and allowed. The Scenario: Zones: outside and insideA DNAT rule from outside-to-outside that NATs 1.1.1.1:22 which translates to 192.168.1.1:22A security policy that from outside-to-inside traffic for 1.1.1.1:22Result:Any...
We have been trying to block the following website to stop students at our school playing Pacman https://www.google.co.uk/search?hl=en&site=webhp&source=hp&q=pacman&oq=pac&gs_l=hp.1.0.0l3j0i131k1j0l6.965.1399.0.3543.3.3.0.0.0.0.32.89.3.3.0....0...1.1.64.hp..0.3.87.NoYdh0ojI_E#clb=clb&spf=1495713448440Obvioulsy we want th...
I have two PA 5220s running active/passive and HA but connecting to dual ISPs. In a failover situation the passive firewall would assume the active firewalls default route but physically has a connection to the backup ISPs gateway not the active ISPs. How do I configure this active/passive config to allow the passive firewall to route to the bac...
Hi community, I need to forward all traffic and threat logs to a log collector. I understand most of the process except the security policy part. Once I create a syslog server profile and then a log forwarding profile, I then need to use that log forwarding profile in my security policy. Our firewalls have many rules and my only instructions hav...
Just curious about what I'm seeing. I have two interfaces that are in a vwire. The switch interfaces which go to the the FW were shut down last week yet looking on the firewall, I see that there are still active sessions which show these two interfaces as the ingress and egress points. These sessions would have been established before the inter...
External ipaddress 23.35.182.93 is getting incorrectly mapped to a rule "Permit Intranet Sites". The rule uses a Urlcategory for Intranet sites and the destination has trust/untrust zones with a negate on one specific destination address. What might cause the firewall to misapply rules if the dns to ipaddress mappings are effectively static? I a...
| Subject | Likes |
|---|---|
| 3 Likes | |
| 2 Likes | |
| 2 Likes | |
| 1 Like | |
| 1 Like |