- Access exclusive content
- Connect with peers
- Share your expertise
- Find support resources

Hi All, I have a customer that looses it's access to the Web GUI of the PAN Firewall except console connection. Aggregate Interface is configured. Can I assign an interface management profile via CLI on the aggregate interfaces? E.g. ae1.100? When i type set network interface aggregate-ethernet and hit the "?" I can't see tha aggregate interface...
We have configured the SSL inbound decryption.When we do the PCAPS on the PA we do not see POST message on the re and tx pcaps. Need to know is this default behaviour?On traffic logs we see decryption flag as checked.Also from CLI i verify that PA is decrypting the traffic.
Hi Team, we have firewall running version 9.0.6,9.0.4 and 9.0.7, well in this case what could be the suggested version of panorama?i have heard , panorama should run with same or later version firewall OS, Is it talking about the major version like 7.x,8.x or 9.xor talking about minor release?
Hi Community, All the agents in my traps setup on ver 4.2.5 shown as disconnected. As the issue looks like ESM server related, i have followed the document https://docs.paloaltonetworks.com/traps/4-2/traps-endpoint-security-manager-admin/troubleshooting/troubleshoot-esm-console-issues/why-do-all-endpoints-appear-as-disconnected-in-the-esm-consol...
Hello, I'm planning to upgrade storage capacity M-500.It's using 12 slots with 1TB disks, I'm going to insert 2TB disks to empty slots and replace 1TB to 2TB. As I know, after add new disks, panorama will redistribute existing logs.While that process, can I replace 1TB disk to 2TB? Thanks
Hi,Here I am trying to create a site to site vpn in Paloalto firewall, now in local network I have 8 individual /32 ips and for remote 10 individual /32 ips. This is for policy based vpn. Now if I add proxy ids for local and remote ips. I am getting around 80 proxy ids. Requirement is to only use ips not subnets. Now few connections are not work...
Hello everybody, We are trying to replace our Lan-to-Lan concentrator (currently a Cisco ASA) with a PAN-5220 version 8.1. On the Cisco ASA firewall, we are currently doing source and destination NAT for each incoming connection. We change the source IP address because our partners use many different private subnets that we can't route or that ...
Hi community, I'm just curious why does the Firewall detect a malicious action/file but the traps stays quite about like do they have difference in alerting?
Does anybody know how to output the detailed HIP match logs to syslog?As it stands, we've got to go to Monitor > HIP Match > Magnifying Glass Icon to see them.We'd like to send this rich data set to Splunk or another tool to write reports against.
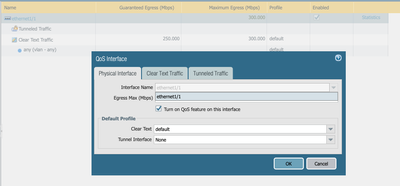
Hi All, I've created a generic QoS profile under Network >> QoS but when I view the graph it shows the bandwidth as being much less that I know it is. At the moment I'm streaming music which is around 2 Mbps but the graph never goes above 0.25 Mbps Have I missed something in the config?
Hi, We are working to create a global protect vpn connetion between our windows 10 devices and the PA FW ver. 8.0.1. The VPN tunnel needs to use a pre-login tunnel initially (authenticating via the machine cert) which when the user logs in re-authenticates the user using SAML (Azure via ADFS) and renames the existing VPN tunnel. We have an exis...
I have migrated HA pair in Panoroma.Let's say I make some changes from Panoroma and push to only active device.Now with config sync enabled locally on the firewalls, will it sync the running config to passive device. Panoroma shows config out of synch on passive device that's fine as it's one way sync but on actual firewall will it be synchroni...
Instead of manually installing certificates from a certificate authority on each managed device under Panorama, is it possible to push certs from Panorama? Thank you.
Hi all since last night i get alot of erros from wildfire, antivirus updates, content updates...All sheduled updates and even manual checks from the gui bring up errors.No HA config.Problem is on a 3020 and a old 500.Ping and trace work to eu.wildfire.paloaltonetworks, wildfire.paloaltonetworks and updates.paloaltonetworksDNS seems to be ok.Syst...
| Subject | Likes |
|---|---|
| 5 Likes | |
| 3 Likes | |
| 3 Likes | |
| 1 Like | |
| 1 Like |
| User | Likes Count |
|---|---|
| 5 | |
| 4 | |
| 3 | |
| 2 | |
| 2 |